@@ -162,12 +136,12 @@ Instead of rebuilding that process in every prompt, you install it once and make
ECC is MIT-licensed open source. It works best with Claude Code today, has a supported Codex sync path, and provides capability-limited adapters for Cursor, OpenCode, Gemini, Zed, GitHub Copilot, Antigravity, Qwen, and other harnesses. See the [support status matrix](#platform-support) before assuming feature parity.
-Access to 68 agents, 286 skills, and 94 legacy command shims, plus hooks, rules, memory, continuous learning, and AgentShield security scanning. The agents are specialized for planning, review, build repair, security, architecture, and domain work.
+Access to 68 agents, 289 skills, and 94 legacy command shims, plus hooks, rules, memory, continuous learning, and AgentShield security scanning. The agents are specialized for planning, review, build repair, security, architecture, and domain work.
| Included | Count | What it gives you |
| ---------------- | ----------: | ------------------------------------------------------------------------------------ |
| Agents | 68 agents | Planning, review, build repair, security, architecture, and domain work |
-| Skills | 286 skills | TDD, research, security, docs, frontend, data, ML, operations, and more |
+| Skills | 289 skills | TDD, research, security, docs, frontend, data, ML, operations, and more |
| Commands | 94 commands | Convenient entry points while ECC moves to a skills-first surface |
| Hooks and memory | Runtime | Enforcement, session summaries, continuous learning, instincts, and context controls |
| Rules | Selective | Always-loaded standards you choose by language or project |
@@ -191,25 +165,81 @@ Access to 68 agents, 286 skills, and 94 legacy command shims, plus hooks, rules,
### Recommended: universal guided setup
-Run the package command from your terminal. For Claude Code setup, updates,
-scope changes, and hook-profile changes:
+For Claude Code plugin setup, updates, scope changes, and hook-profile changes:
```bash
-npx ecc-universal setup
+npx ecc-universal@2.2.1 setup
```
-To configure Claude Code, Codex, or Kimi Code in one reviewed flow:
+If npm reports a version or cache error, confirm the registry version before retrying:
```bash
-npx ecc-universal install --guided
+npm view ecc-universal version
```
+ECC 2.2 supports the same guided setup through modern package runners:
+
+| Package runner | Guided setup command |
+|---|---|
+| npm / npx | `npx ecc-universal@2.2.1 setup` |
+| pnpm | `pnpm dlx ecc-universal@2.2.1 setup` |
+| Yarn 2+ | `yarn dlx ecc-universal@2.2.1 setup` |
+| Bun | `bunx ecc-universal@2.2.1 setup` |
+
+The examples select [the published ECC 2.2.1 release](https://www.npmjs.com/package/ecc-universal/v/2.2.1), matching this repository's release version. A version pin is not a security audit or an integrity check. Review the release source and registry integrity before running package code; use a reviewed checkout for unreleased changes.
+
+Yarn Classic 1 does not provide `yarn dlx`; use `npx`, install the package globally, or upgrade Yarn for a temporary one-shot run.
+
+The wizard inventories the official marketplace and every native Claude install scope before making changes, then installs, updates, or safely moves `ecc@ecc` to the scope you choose. Rerun the same command whenever you want to update ECC, change scope, or change its hook profile. This setup wizard currently configures the Claude Code plugin; use the multi-harness wizard below for Codex or Kimi Code.
+
+To configure more than one coding agent in one reviewed flow, use the multi-harness wizard:
+
+```bash
+npx ecc-universal@2.2.1 install --guided
+```
+
+It lets you select any combination of Claude Code, Codex, and Kimi Code, shows each install channel and destination, preflights every selection before the first write, and asks for one final confirmation.
+
+| Harness | Guided install behavior |
+|---|---|
+| Claude Code | Native `ecc@ecc` plugin with one `user`, `project`, or `local` scope and an ECC hook profile |
+| Codex | Native Codex marketplace/plugin lifecycle; hook review and trust remain Codex-owned |
+| Kimi Code | Managed project files under `./.kimi-code`; ECC hooks, model/provider settings, and authentication are not configured |
+
+For automation, make every provider-specific choice explicit:
+
+```bash
+npx ecc-universal@2.2.1 install --guided \
+ --harness claude --harness codex --harness kimi \
+ --claude-scope local --claude-hooks standard \
+ --profile core --yes
+```
+
+Verify the native guided Codex path and managed Kimi path without writing first:
+
+```bash
+npx ecc-universal@2.2.1 install --guided --harness codex --dry-run
+npx ecc-universal@2.2.1 install --profile core --target kimi --dry-run
+```
+
+Additional package-name commands are also available through the 2.2 alias:
+
+```bash
+npx ecc-universal@2.2.1 consult "security reviews" --target claude
+npx ecc-universal@2.2.1 install --profile minimal --target claude --with capability:machine-learning
+npx ecc-universal@2.2.1 doctor --target kimi
+```
+
+Do not use `npx ecc-install --profile minimal --target claude`: `ecc-install` is a binary name inside `ecc-universal`, not a separately published npm package.
+
+ECC also ships advanced managed adapters for `cursor`, `antigravity`, `gemini`, `opencode`, `codebuddy`, `joycode`, `qwen`, `zed`, `hermes`, and `openclaw`. Those targets still use their documented `ecc install --target ...` paths until each adapter has passed the guided collision, update, repair, and uninstall lifecycle matrix. Neither wizard silently installs into every detected harness.
+
### Pick one path only (per harness)
You can use ECC with Claude Code, Codex, and other harnesses at the same time. Choose one install method for each harness:
- **Recommended default:** run the guided Claude plugin setup above
-- **Also supported for Claude Code:** use the [native plugin commands above](#install-with-claude-code)
+- **Also supported for Claude Code:** use the [native plugin commands](#claude-code-details)
- **Available in release 2.2:** guided package setup for Claude Code, Codex, and Kimi Code
- **Works:** Claude Code plugin + Codex native plugin
- **Works:** Claude Code plugin + the legacy Codex sync flow
@@ -224,6 +254,15 @@ If you already layered multiple installs and things look duplicated, skip straig
### Claude Code details
+Alternatively, run Claude Code's native plugin commands inside Claude Code:
+
+```text
+/plugin marketplace add https://github.com/affaan-m/ECC
+/plugin install ecc@ecc
+```
+
+The native path installs ECC's skills, agents, commands, and plugin-managed hooks. If you choose it, stop there. Do not also run a full manual install into Claude Code.
+
Claude Code owns these built-in commands, including their errors when a marketplace, plugin, or conflicting scope already exists. ECC cannot intercept that parser. If either native command reports an existing install or scope conflict, use the 2.2 guided setup or resolve the conflicting Claude plugin scope before retrying; do not layer a manual install on top.
After ECC is installed, `/ecc:configure-ecc` is the namespaced in-Claude reconfiguration skill. It delegates to the same safe setup flow, but it is available only after the plugin is installed and cannot replace Claude Code's built-in `/plugin` command during a first install.
@@ -350,74 +389,8 @@ Cursor installs agent definitions under `.cursor/agents/ecc-*.md`. Cursor-native
Deep per-harness notes (feature parity, hook adapters, limitations) live in [Platform Support](#platform-support) below.
-## Self-Hosted Models and Custom Endpoints
-
-ECC works through each harness's normal configuration, so you can use an official provider, a compatible custom API endpoint or model gateway, or a self-hosted model without changing ECC's workflows.
-
-For Claude Code, ECC does not hardcode Anthropic-hosted transport settings. Minimal gateway example:
-
-```bash
-export ANTHROPIC_BASE_URL=https://your-gateway.example.com
-export ANTHROPIC_AUTH_TOKEN=your-token
-claude
-```
-
-If your gateway remaps model names, configure that in Claude Code rather than in ECC. ECC's hooks, skills, commands, and rules are model-provider agnostic once the `claude` CLI is already working. See Anthropic's [LLM gateway documentation](https://docs.anthropic.com/en/docs/claude-code/llm-gateway) and [model configuration documentation](https://docs.anthropic.com/en/docs/claude-code/model-config).
-
-Run or self-host any open-source model behind that gateway using separate compute and serving setup. If you need GPU capacity, [Itô](https://compute.itomarkets.com) is ECC's preferred compute sponsor; any GPU provider works. The sponsorship link is passive: it does not invoke an RFQ, reserve capacity, provision compute, or configure serving. Separately, `ecc ito find` invokes the explicitly configured canonical Itô CLI and submits a live authenticated RFQ; it does not reserve capacity. Managed inference through Itô is not live yet.
-
-### Self-host Kimi with ECC + Itô compute
-
-The Kimi Code harness and the model-serving layer are separate. ECC configures the agent harness; you bring an API endpoint ([get a Kimi API key](https://platform.kimi.ai?aff=ecc)) or self-host an open-weight Kimi model on your own GPU capacity. This adapter is verified against Kimi Code 0.31.x (`@moonshot-ai/kimi-code`):
-
-
-
-Configure the endpoint with Kimi Code's
official provider guide, then install ECC:
-
-```bash
-bash ./install.sh --target kimi --profile minimal
-node scripts/ecc.js doctor --target kimi
-kimi
-```
-
-Kimi Code discovers the installed `.kimi-code/AGENTS.md` instructions and `.kimi-code/skills/` workflows natively; project-level `.agents/skills/` is also an official discovery location. ECC safely merges project MCP entries into `.kimi-code/mcp.json` and does not change the user-level `~/.kimi-code/config.toml`. Kimi Code supports native hooks, but ECC's current managed-project adapter does not configure them, so this installer does not offer Kimi hook profiles. The installer dry-run and regression suite verify that every managed Kimi write stays inside the project-local `.kimi-code/` root.
-
-### Itô compute CLI bridge
-
-`ecc ito` delegates to the separately installed canonical Itô client; ECC does not maintain a second API client. `ecc ito login [--no-browser]` performs device authorization, opens the Itô verification page by default, and persists a device token in macOS Keychain; `--no-browser` suppresses the page handoff. ECC itself does no browser automation. `ecc ito auth` is validation-only and rejects `--no-browser`. The available operations are `ecc ito login`, `ecc ito auth`, `ecc ito find`, `ecc ito status`, and the separately gated `ecc ito evals`. The matching MCP tools remain `ito_auth`, `ito_find`, and `ito_status`; `ito_auth` validates existing credentials and node qualification is CLI-only.
-
-The `ito-compute-cli` package is currently unpublished. Build it locally from the Itô runtime repo (private while the desk hardens; design partners get access) under `cli/ito-compute-cli`, run `npm ci` and `npm run check`, then set `ECC_ITO_CLI_EXECUTABLE` to that build's absolute `dist/bin/ito.js` path. Login never inherits `ITO_API_KEY`; auth, find, and status forward `ITO_API_KEY` directly when configured, and `ITO_AUTH_MODE=legacy` is not required. `ecc ito logout` revokes the current device credential and retains its local copy if remote revocation cannot be confirmed. Device tokens use macOS Keychain by default; explicit file fallback must retain owner-only directory/file permissions. ECC does not discover this credential-bearing client through `PATH`. See the [`ito-compute` skill](skills/ito-compute/SKILL.md) for the full RFQ authority and MCP setup contract.
-
-`find` submits a live authenticated RFQ. It does not reserve capacity. `evals` requires both `ITO_ENABLE_SIXTYTWO_LIVE=1` and `--live-sixtytwo`, a separately installed `sixtytwo-cli==0.3.33`, an explicit node list, and an existing absolute configuration directory. It cannot rent, launch, recover, repair, or purchase. ECC exposes no quote lock, purchase, workload, or inference path, and it never replaces a missing client or failed live call with a local result.
-
## Advanced Install Options
-The options stay here, directly under the main install paths, so you do not have to hunt through the README when the default setup is not the right fit.
-
Low-context install with no hook runtime
@@ -426,7 +399,7 @@ The options stay here, directly under the main install paths, so you do not have
Use this when you want ECC's rules, agents, commands, platform config, and core workflows without runtime hooks:
```bash
-npx ecc-universal install --profile minimal --target claude
+npx ecc-universal@2.2.1 install --profile minimal --target claude
```
From a source checkout, the equivalent command is:
@@ -592,7 +565,7 @@ ECC-managed install and Codex sync flows will skip or remove those bundled serve
`multi-*` commands are **not** covered by the base plugin/rules install.
-To use `/multi-plan`, `/multi-execute`, `/multi-backend`, `/multi-frontend`, and `/multi-workflow`, you must also install the `ccg-workflow` runtime. Initialize it with `npx ccg-workflow`.
+To use `/multi-plan`, `/multi-execute`, `/multi-backend`, `/multi-frontend`, and `/multi-workflow`, you must also install the `ccg-workflow` runtime. Choose and review an exact release using the [upstream CCG installation guide](https://github.com/fengshao1227/ccg-workflow#readme), then initialize that installed runtime. ECC does not bundle CCG or attest to a compatible, audited CCG release; this guide does not bootstrap an unspecified registry version.
That runtime provides the external dependencies these commands expect, including:
@@ -611,11 +584,11 @@ If you installed from the universal package, run these commands from the same
project directory used for installation:
```bash
-npx ecc-universal list-installed
-npx ecc-universal doctor
-npx ecc-universal repair
-npx ecc-universal uninstall --dry-run
-npx ecc-universal uninstall
+npx ecc-universal@2.2.1 list-installed
+npx ecc-universal@2.2.1 doctor
+npx ecc-universal@2.2.1 repair
+npx ecc-universal@2.2.1 uninstall --dry-run
+npx ecc-universal@2.2.1 uninstall
```
From a source checkout, inspect the managed state before reinstalling:
@@ -646,74 +619,6 @@ If you stacked methods, clean up in this order:
4. Reinstall once, using a single path.
-## Universal guided setup details
-
-> [!IMPORTANT]
-> These package-runner commands require `ecc-universal` 2.2.0 or newer and
-> Node.js 18 or newer. Claude plugin setup also requires Git and Claude Code
-> 2.1 or newer on `PATH`.
-
-For Claude Code plugin setup, updates, scope changes, and hook-profile changes:
-
-```bash
-npx ecc-universal setup
-```
-
-ECC 2.2 supports the same guided setup through modern package runners:
-
-| Package runner | Guided setup command |
-|---|---|
-| npm / npx | `npx ecc-universal setup` |
-| pnpm | `pnpm dlx ecc-universal setup` |
-| Yarn 2+ | `yarn dlx ecc-universal setup` |
-| Bun | `bunx ecc-universal setup` |
-
-Yarn Classic 1 does not provide `yarn dlx`; use `npx`, install the package globally, or upgrade Yarn for a temporary one-shot run.
-
-The wizard inventories the official marketplace and every native Claude install scope before making changes, then installs, updates, or safely moves `ecc@ecc` to the scope you choose. Rerun the same command whenever you want to update ECC, change scope, or change its hook profile. This setup wizard currently configures the Claude Code plugin; use the multi-harness wizard below for Codex or Kimi Code.
-
-To configure more than one coding agent in one reviewed flow, use the multi-harness wizard:
-
-```bash
-npx ecc-universal install --guided
-```
-
-It lets you select any combination of Claude Code, Codex, and Kimi Code, shows each install channel and destination, preflights every selection before the first write, and asks for one final confirmation.
-
-| Harness | Guided install behavior |
-|---|---|
-| Claude Code | Native `ecc@ecc` plugin with one `user`, `project`, or `local` scope and an ECC hook profile |
-| Codex | Native Codex marketplace/plugin lifecycle; hook review and trust remain Codex-owned |
-| Kimi Code | Managed project files under `./.kimi-code`; ECC hooks, model/provider settings, and authentication are not configured |
-
-For automation, make every provider-specific choice explicit:
-
-```bash
-npx ecc-universal install --guided \
- --harness claude --harness codex --harness kimi \
- --claude-scope local --claude-hooks standard \
- --profile core --yes
-```
-
-Verify the native guided Codex path and managed Kimi path without writing first:
-
-```bash
-npx ecc-universal install --guided --harness codex --dry-run
-npx ecc-universal install --profile core --target kimi --dry-run
-```
-
-Additional package-name commands are also available through the 2.2 alias:
-
-```bash
-npx ecc-universal consult "security reviews" --target claude
-npx ecc-universal install --profile minimal --target claude --with capability:machine-learning
-npx ecc-universal doctor --target kimi
-```
-
-Do not use `npx ecc-install --profile minimal --target claude`: `ecc-install` is a binary name inside `ecc-universal`, not a separately published npm package.
-
-ECC also ships advanced managed adapters for `cursor`, `antigravity`, `gemini`, `opencode`, `codebuddy`, `joycode`, `qwen`, `zed`, `hermes`, and `openclaw`. Those targets still use their documented `ecc install --target ...` paths until each adapter has passed the guided collision, update, repair, and uninstall lifecycle matrix. Neither wizard silently installs into every detected harness.
-
## Start Using ECC
Start with the workflow you need, not the full catalog.
@@ -728,7 +633,7 @@ Start with the workflow you need, not the full catalog.
| Checking context pressure | `/context-budget` |
| Ending a long session | `/save-session` or `/learn-eval` |
| Resuming later | `/resume-session` |
-| Auditing agent config | `/security-scan` or `npx -y ecc-agentshield scan --path .` |
+| Auditing agent config | `/security-scan` with a reviewed scanner, or installed `agentshield scan --path .` |
Plugin commands and manual commands
@@ -806,271 +711,83 @@ e2e-testing skill -> e2e-runner: critical user flow
```
-## What's New: ECC 2.1
+## Self-Hosted Models and Custom Endpoints
-> [!IMPORTANT]
-> **NEW IN ECC 2.1: Plan Canvas · Kimi harness · self-hosted compute on Itô GPUs.**
-> [See the full release notes →](https://github.com/affaan-m/ECC/blob/main/docs/releases/2.1.0/release-notes.md)
+ECC works through each harness's normal configuration, so you can use an official provider, a compatible custom API endpoint or model gateway, or a self-hosted model without changing ECC's workflows.
-### Plan Canvas: review plans by pointing, not retyping
-
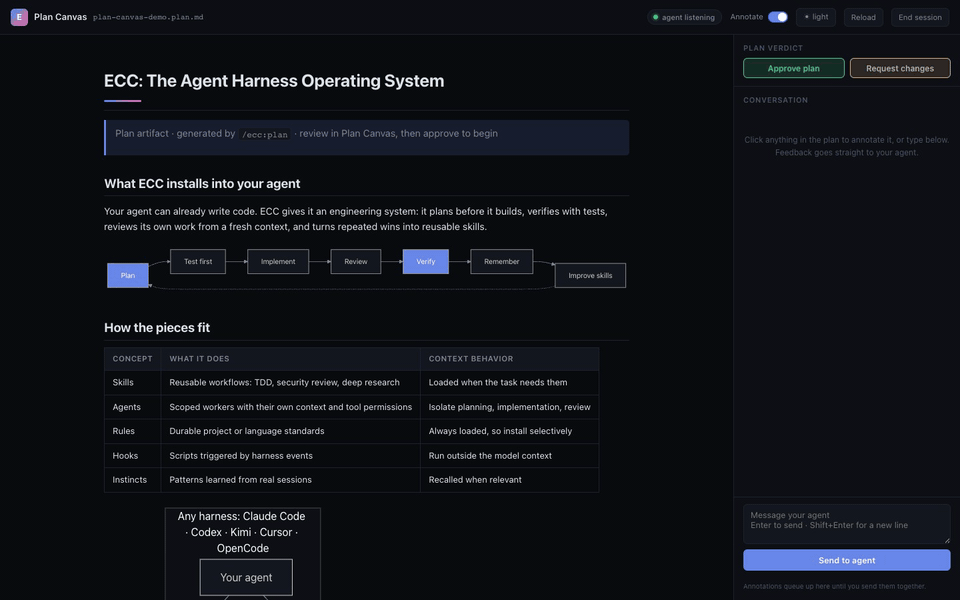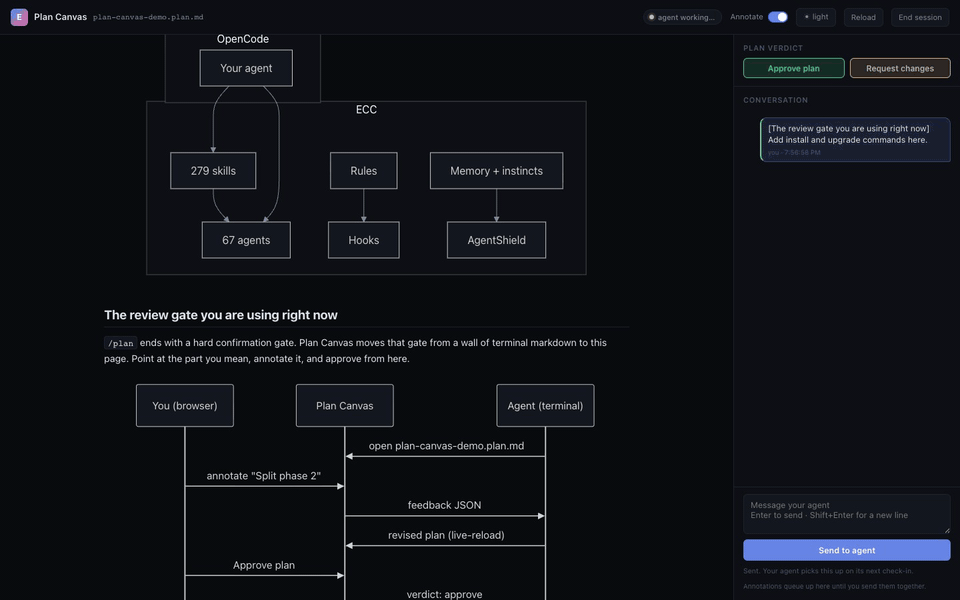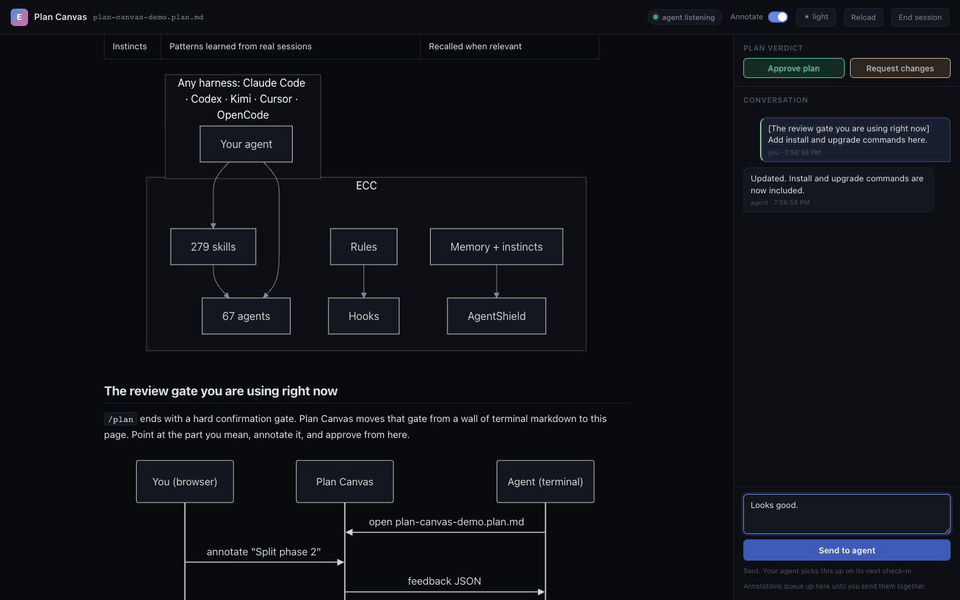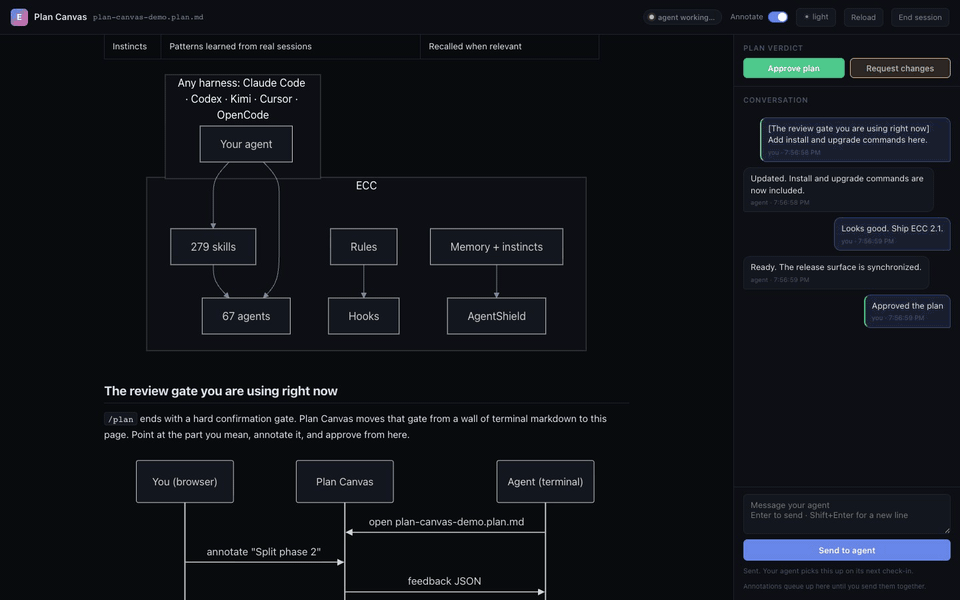
-Your agent writes a plan, then opens it in a loopback-only browser canvas. Click the part you mean, attach numbered annotations, chat from a side rail, and hit **Approve plan** or **Request changes**. The verdict maps straight onto `/plan`'s CONFIRM gate. Mermaid diagrams render live, and edits to the plan file reload the page.
-
-
-
-It's harness- and model-agnostic: a plain CLI (`ecc-plan-canvas`) speaking JSON, so any agent can drive it. Try it: ask your agent to `/ecc:plan` anything, then review from the page instead of the terminal.
-
-[Open the plan used in this demo →](https://github.com/affaan-m/ECC/blob/main/docs/releases/2.1.0/plan-canvas-demo.plan.md)
-
-### Also in 2.1
-
-- **Kimi Code install target** (`--target kimi`): ECC installs natively into [Moonshot AI](https://www.moonshot.ai)'s Kimi Code CLI
-- **Self-host on GPUs**: a verified path with [Itô](https://compute.itomarkets.com), ECC's preferred compute sponsor, including the opt-in `ecc ito find` RFQ bridge (details and disclosures above in [Self-Hosted Models and Custom Endpoints](#self-hosted-models-and-custom-endpoints))
-- **Moonshot AI (Kimi), Itô, and Atlas Cloud** are now public sponsors
-- **Hermes + OpenClaw install targets**, a Codex navigation guide, consolidated PostToolUse hooks, and supply-chain hardening
-
-### Current development: Unified Memory Vault
-
-`ecc memory` gives Claude, Codex, Hermes, OpenClaw, Kimi, and other harnesses one local, inspectable Markdown format for durable context and handoffs. The optional `ecc-memory-mcp` stdio server exposes the same bounded save/search/read/doctor surface without enabling itself by default. Full detail in [Share context between harnesses](#share-context-between-harnesses) below.
-
-
-Previous releases
-
-| Version | Highlights |
-|---|---|
-| [v2.0.0](https://github.com/affaan-m/ECC/releases/tag/v2.0.0) | The Agent Harness Operating System: cross-harness graduation, control-pane substrate, `orch-*` orchestrators, Discord + ECC bot, single-connector MCP policy |
-| [v1.10.0](https://github.com/affaan-m/ECC/releases/tag/v1.10.0) | Surface refresh, operator workflows, ECC 2.0 alpha |
-| [v1.9.0](https://github.com/affaan-m/ECC/releases/tag/v1.9.0) | Selective install, ECC Tools Pro, 12 language ecosystems |
-| [v1.8.0](https://github.com/affaan-m/ECC/releases/tag/v1.8.0) | Harness performance and cross-platform reliability |
-| [v1.7.0](https://github.com/affaan-m/ECC/releases/tag/v1.7.0) | Cross-platform expansion and presentation builder |
-| [v1.6.0](https://github.com/affaan-m/ECC/releases/tag/v1.6.0) | Codex Edition and the ECC Tools GitHub App |
-| [v1.5.0](https://github.com/affaan-m/ECC/releases/tag/v1.5.0) | Universal Edition |
-| [v1.4.0](https://github.com/affaan-m/ECC/releases/tag/v1.4.0) | Multi-language rules, installation wizard, PM2 orchestration |
-| [v1.3.0](https://github.com/affaan-m/ECC/releases/tag/v1.3.0) | Complete OpenCode plugin support |
-| [v1.2.0](https://github.com/affaan-m/ECC/releases/tag/v1.2.0) | Unified commands and skills |
-| [v1.1.0](https://github.com/affaan-m/ECC/releases/tag/v1.1.0) | Cross-platform support and community fixes |
-| [v1.0.0](https://github.com/affaan-m/ECC/releases/tag/v1.0.0) | Official plugin release |
-
-
-
-
-Release history in detail
-
-### v2.0.0: The Agent Harness Operating System (Jun 2026)
-
-Stable graduation of the 2.0 line: the control-pane substrate (session adapters + MCP inventory), the worktree-lifecycle service, the `orch-*` orchestrator family, and the launch of the [ECC Discord community](https://discord.gg/36yGMHGFbR). Full notes: [docs/releases/2.0.0/release-notes.md](docs/releases/2.0.0/release-notes.md).
-
-### v2.0.0-rc.1: Surface Refresh, Operator Workflows, and ECC 2.0 Alpha (Apr 2026)
-
-- **Dashboard GUI**: New Tkinter-based desktop application (`ecc_dashboard.py` or `npm run dashboard`) with dark/light theme toggle, font customization, and project logo in header and taskbar.
-- **Public surface synced to the live repo**: metadata, catalog counts, plugin manifests, and install-facing docs now match the actual OSS surface.
-- **Operator and outbound workflow expansion**: `brand-voice`, `social-graph-ranker`, `connections-optimizer`, `customer-billing-ops`, `ecc-tools-cost-audit`, `google-workspace-ops`, `project-flow-ops`, and `workspace-surface-audit` round out the operator lane.
-- **Media and launch tooling**: `manim-video`, `remotion-video-creation`, and upgraded social publishing surfaces make technical explainers and launch content part of the same system.
-- **Framework and product surface growth**: `nestjs-patterns`, richer Codex/OpenCode install surfaces, and expanded cross-harness packaging keep the repo usable beyond a single harness.
-- **Itô prediction-market skill pack**: the consolidated `ito-baskets` skill (read-only basket index, comparison, market briefs, and non-executable planning worksheets — replacing the former `ito-market-intelligence`, `ito-basket-compare`, `ito-trade-planner`, and `ito-data-atlas-agent` skills), plus `prediction-market-oracle-research` and `prediction-market-risk-review`, add public, non-advisory market/basket workflows while keeping live Itô API access gated and separate from ECC Tools billing.
-- **Optimization skill pack**: `parallel-execution-optimizer`, `benchmark-optimization-loop`, `data-throughput-accelerator`, `latency-critical-systems`, and `recursive-decision-ledger` turn repeated speed/recursion prompts into bounded benchmark, throughput, and decision-ledger workflows.
-- **ECC 2.0 alpha in-tree**: the Rust control-plane prototype in `ecc2/` builds locally and exposes `dashboard`, `start`, `sessions`, `status`, `stop`, `resume`, and `daemon` commands.
-- **Operator status snapshots**: `ecc status --markdown --write status.md` turns the local state store into a portable handoff covering readiness, active sessions, skill-run health, install health, pending governance events, and linked work items from Linear/GitHub/handoffs.
-- **Ecosystem hardening**: AgentShield, ECC Tools cost controls, billing portal work, and website refreshes continue to ship around the core plugin instead of drifting into separate silos.
-
-### v1.9.0: Selective Install and Language Expansion (Mar 2026)
-
-- **Selective install architecture**: Manifest-driven install pipeline with `install-plan.js` and `install-apply.js` for targeted component installation. State store tracks what's installed and enables incremental updates.
-- **6 new agents**: `typescript-reviewer`, `pytorch-build-resolver`, `java-build-resolver`, `java-reviewer`, `kotlin-reviewer`, `kotlin-build-resolver` expand language coverage to 10 languages.
-- **New skills**: `pytorch-patterns`, `documentation-lookup`, `bun-runtime`, `nextjs-turbopack`, 8 operational domain skills, and `mcp-server-patterns`.
-- **Session and state infrastructure**: SQLite state store with query CLI, session adapters for structured recording, skill evolution foundation for self-improving skills.
-- **Orchestration overhaul**: Deterministic harness audit scoring, hardened orchestration status and launcher compatibility, observer loop prevention with 5-layer guard.
-- **Observer reliability**: Memory explosion fix with throttling and tail sampling, sandbox access fix, lazy-start logic, and re-entrancy guard.
-- **12 language ecosystems**: New rules for Java, PHP, Perl, Kotlin/Android/KMP, C++, and Rust join existing TypeScript, Python, Go, and common rules.
-- **Community contributions**: Korean and Chinese translations, biome hook optimization, video processing skills, operational skills, PowerShell installer, Antigravity IDE support.
-- **CI hardening**: 19 test failure fixes, catalog count enforcement, install manifest validation, and full test suite green.
-
-### v1.8.0: Harness Performance System (Mar 2026)
-
-- **Harness-first release**: ECC is explicitly framed as an agent harness performance system, not just a config pack.
-- **Hook reliability overhaul**: SessionStart root fallback, Stop-phase session summaries, and script-based hooks replacing fragile inline one-liners.
-- **Hook runtime controls**: `ECC_HOOK_PROFILE=minimal|standard|strict` and `ECC_DISABLED_HOOKS=...` for runtime gating without editing hook files.
-- **New harness commands**: `/harness-audit`, `/loop-start`, `/loop-status`, `/quality-gate`, `/model-route`.
-- **NanoClaw v2**: model routing, skill hot-load, session branch/search/export/compact/metrics.
-- **Cross-harness parity**: behavior tightened across Claude Code, Cursor, OpenCode, and Codex app/CLI.
-- **997 internal tests passing**: full suite green after hook/runtime refactor and compatibility updates.
-
-### v1.7.0: Cross-Platform Expansion and Presentation Builder (Feb 2026)
-
-- **Codex app + CLI support**: Direct `AGENTS.md`-based Codex support, installer targeting, and Codex docs
-- **`frontend-slides` skill**: Zero-dependency HTML presentation builder with PPTX conversion guidance and strict viewport-fit rules
-- **5 new generic business/content skills**: `article-writing`, `content-engine`, `market-research`, `investor-materials`, `investor-outreach`
-- **Broader tool coverage**: Cursor, Codex, and OpenCode support tightened so the same repo ships cleanly across all major harnesses
-- **992 internal tests**: Expanded validation and regression coverage across plugin, hooks, skills, and packaging
-
-### v1.6.0: Codex CLI, AgentShield, and Marketplace (Feb 2026)
-
-- **Codex CLI support**: New `/codex-setup` command generates `codex.md` for OpenAI Codex CLI compatibility
-- **7 new skills**: `search-first`, `swift-actor-persistence`, `swift-protocol-di-testing`, `regex-vs-llm-structured-text`, `content-hash-cache-pattern`, `cost-aware-llm-pipeline`, `skill-stocktake`
-- **AgentShield integration**: `/security-scan` runs AgentShield directly from Claude Code; 1282 tests, 102 rules
-- **GitHub Marketplace**: ECC Tools GitHub App live at [github.com/marketplace/ecc-tools](https://github.com/marketplace/ecc-tools) with free/pro/enterprise tiers
-- **30+ community PRs merged**: Contributions from 30 contributors across 6 languages
-- **978 internal tests**: Expanded validation suite across agents, skills, commands, hooks, and rules
-
-### v1.4.1: Bug Fix (Feb 2026)
-
-- **Fixed instinct import content loss**: `parse_instinct_file()` was silently dropping all content after frontmatter (Action, Evidence, Examples sections) during `/instinct-import`. ([#148](https://github.com/affaan-m/ECC/issues/148), [#161](https://github.com/affaan-m/ECC/pull/161))
-
-### v1.4.0: Multi-Language Rules, Installation Wizard, and PM2 (Feb 2026)
-
-- **Interactive installation wizard**: New `configure-ecc` skill provides guided setup with merge/overwrite detection
-- **PM2 and multi-agent orchestration**: 6 new commands (`/pm2`, `/multi-plan`, `/multi-execute`, `/multi-backend`, `/multi-frontend`, `/multi-workflow`) for managing complex multi-service workflows
-- **Multi-language rules architecture**: Rules restructured from flat files into `common/` + `typescript/` + `python/` + `golang/` directories. Install only the languages you need
-- **Chinese (zh-CN) translations**: Complete translation of all agents, commands, skills, and rules (80+ files)
-- **GitHub Sponsors support**: Sponsor the project via GitHub Sponsors
-- **Enhanced CONTRIBUTING.md**: Detailed PR templates for each contribution type
-
-### v1.3.0: OpenCode Plugin Support (Feb 2026)
-
-- **Full OpenCode integration**: 12 agents, 24 commands, 16 skills with hook support via OpenCode's plugin system (20+ event types)
-- **3 native custom tools**: run-tests, check-coverage, security-audit
-- **LLM documentation**: `llms.txt` for comprehensive OpenCode docs
-
-### v1.2.0: Unified Commands and Skills (Feb 2026)
-
-- **Python/Django support**: Django patterns, security, TDD, and verification skills
-- **Java Spring Boot skills**: Patterns, security, TDD, and verification for Spring Boot
-- **Session management**: `/sessions` command for session history
-- **Continuous learning v2**: Instinct-based learning with confidence scoring, import/export, evolution
-
-See the full changelog in [Releases](https://github.com/affaan-m/ECC/releases).
-
-
-## Why Choose ECC?
-
-| Without a system | With ECC |
-| ------------------------------------------------------- | --------------------------------------------------------------------- |
-| Plans disappear into chat history | Plans become editable artifacts before implementation starts |
-| "Please use TDD" is an instruction the model may forget | TDD becomes a gated RED -> GREEN -> REFACTOR workflow with evidence |
-| The same context writes and reviews the code | A fresh-context reviewer looks for regressions and blind spots |
-| Memory means saving an enormous transcript | Sessions are distilled into summaries, instincts, and reusable skills |
-| Quality checks depend on reminders | Hooks can enforce deterministic checks outside the prompt |
-| Agent configuration is trusted by default | AgentShield scans the harness itself as an attack surface |
-
-### TDD: Test-Driven Development
-
-```text
-/ecc:plan "Add usage-based billing alerts"
- -> confirm or edit the plan
- -> activate tdd-workflow
- -> capture RED evidence before implementation
- -> implement until GREEN
- -> review from fresh context
- -> fix findings with regression tests
- -> verify build, lint, types, and tests
-```
-
-A result is not just code. It's a trail of evidence: the plan, the failing test, the passing test, the review findings, and the final verification.
-
-### Skills keep the context focused
-
-Rules, skills, agents, and hooks solve different problems. Keeping those jobs separate is how ECC adds capability without dumping the entire repository into every session.
-
-| Concept | What it does | Context behavior |
-|---|---|---|
-| Skills | Reusable workflows such as TDD, security review, or deep research | Loaded when the task needs them |
-| Agents | Scoped workers with their own context and tool permissions | Isolate planning, implementation, and review |
-| Rules | Durable project or language standards | Always loaded, so install them selectively |
-| Hooks | Scripts triggered by harness events | Run outside the model context |
-| Instincts | Patterns learned from real sessions with confidence scores | Recalled when relevant |
-
-### Share context between harnesses
-
-ECC's Memory Vault gives Claude, Codex, Hermes, OpenClaw, Kimi, and other harnesses one local, inspectable Markdown format for durable context and handoffs. Project and team memories live under `.ecc/memory/`; user memories live under `~/.ecc/memory/`.
+For Claude Code, ECC does not hardcode Anthropic-hosted transport settings. Minimal gateway example:
```bash
-npm install -g ecc-universal
-ecc memory init --scope project
-ecc memory search "authentication migration" --target-harness codex
-ecc memory doctor
+export ANTHROPIC_BASE_URL=https://your-gateway.example.com
+export ANTHROPIC_AUTH_TOKEN=your-token
+claude
```
-Memory is unreviewed context, not executable policy. Verify important claims against authoritative sources and promote accepted knowledge into governed project documentation. The optional `ecc-memory-mcp` server exposes the same bounded save, search, read, and doctor surface without enabling itself by default.
+If your gateway remaps model names, configure that in Claude Code rather than in ECC. ECC's hooks, skills, commands, and rules are model-provider agnostic once the `claude` CLI is already working. See Anthropic's [LLM gateway documentation](https://docs.anthropic.com/en/docs/claude-code/llm-gateway) and [model configuration documentation](https://docs.anthropic.com/en/docs/claude-code/model-config).
-[Open the Unified Memory workflow →](skills/unified-memory/SKILL.md)
+Run or self-host any open-source model behind that gateway using separate compute and serving setup. If you need GPU capacity, [Itô](https://compute.itomarkets.com) is ECC's preferred compute sponsor; any GPU provider works. The sponsorship link is passive: it does not invoke an RFQ, reserve capacity, provision compute, or configure serving. Separately, `ecc ito find` invokes the explicitly configured canonical Itô CLI and submits a live authenticated RFQ; it does not reserve capacity. Managed inference through Itô is not live yet.
-
-Memory Vault in depth: scopes, handoffs, and trust boundaries
+### Self-host Kimi with ECC + Itô compute
-The Memory Vault stores portable `ecc.memory.v1` Markdown documents instead of copying vendor transcripts or emailing context between agents. Project memories are protected by a fail-closed `.gitignore`; use the team scope only for human-inspected, version-controlled sharing. Team memories remain unreviewed context even after they are committed.
+The Kimi Code harness and the model-serving layer are separate. ECC configures the agent harness; you bring an API endpoint ([get a Kimi API key](https://platform.kimi.ai?aff=ecc)) or self-host an open-weight Kimi model on your own GPU capacity. This adapter is verified against Kimi Code 0.31.x (`@moonshot-ai/kimi-code`):
-Skill-only, minimal, manual, and Claude plugin installs do not put the Memory Vault runtime on `PATH`. Install the npm runtime separately before using the CLI or optional MCP server:
-
-```bash
-npm install -g ecc-universal
-ecc memory --help
-command -v ecc-memory-mcp
-```
-
-```bash
-# Initialize the project vault.
-ecc memory init --scope project
-
-# Write a handoff body to a regular file, then target the next harness.
-ecc memory handoff \
- --from hermes \
- --target codex \
- --title "Continue authentication migration" \
- --body-file ./handoff.md
-
-# Recall it from another harness.
-ecc memory search "authentication migration" --target-harness codex
-ecc memory read
-
-# Validate the vault before sharing team memories.
-ecc memory doctor
-```
-
-Memory bodies are accepted only through `--stdin` or `--body-file`, not as command-line values. The first release keeps every vault entry unreviewed and create-only; human review promotes accepted knowledge into governed project documentation rather than changing memory trust. Normal search recall returns active project and team memories. A direct ID read may inspect a non-active entry. User-scope recall must be requested explicitly. Agents must verify important claims against authoritative sources and must never treat recalled bodies as executable instructions or policy.
-
-For opt-in MCP access, add the `ecc-memory-vault` entry from [`mcp-configs/mcp-servers.json`](mcp-configs/mcp-servers.json) to each harness that needs it, then run `ecc-memory-mcp`. The server exposes only `memory_save`, `memory_search`, `memory_read`, and `memory_doctor`. Each server must launch with a lowercase `ECC_MEMORY_HARNESS` identity; the identity is server-bound and cannot be supplied by a tool caller. User scope additionally requires the operator-controlled `ECC_MEMORY_ALLOW_USER_SCOPE=1` opt-in. See [`skills/unified-memory/SKILL.md`](skills/unified-memory/SKILL.md) for the workflow and trust boundaries, and [`docs/design/ecc-memory-vault.md`](docs/design/ecc-memory-vault.md) for the capability contract.
-
-
-## Guides
-
-This repo is the raw code. The guides explain everything.
-
-
+
-| Topic | What You'll Learn |
-|-------|-------------------|
-| Token Optimization | Model selection, system prompt slimming, background processes |
-| Memory Persistence | Hooks that save/load context across sessions automatically |
-| Continuous Learning | Auto-extract patterns from sessions into reusable skills |
-| Verification Loops | Checkpoint vs continuous evals, grader types, pass@k metrics |
-| Parallelization | Git worktrees, cascade method, when to scale instances |
-| Subagent Orchestration | The context problem, iterative retrieval pattern |
+Configure the endpoint with Kimi Code's official provider guide, then install ECC:
-[Commands Quick Reference](./COMMANDS-QUICK-REF.md) | [Manual Adaptation Guide](docs/MANUAL-ADAPTATION-GUIDE.md)
+```bash
+bash ./install.sh --target kimi --profile minimal
+node scripts/ecc.js doctor --target kimi
+kimi
+```
+
+Kimi Code discovers the installed `.kimi-code/AGENTS.md` instructions and `.kimi-code/skills/` workflows natively; project-level `.agents/skills/` is also an official discovery location. ECC safely merges project MCP entries into `.kimi-code/mcp.json` and does not change the user-level `~/.kimi-code/config.toml`. Kimi Code supports native hooks, but ECC's current managed-project adapter does not configure them, so this installer does not offer Kimi hook profiles. The installer dry-run and regression suite verify that every managed Kimi write stays inside the project-local `.kimi-code/` root.
+
+### Itô compute CLI bridge
+
+`ecc ito` delegates to the separately installed canonical Itô client; ECC does not maintain a second API client. `ecc ito login [--no-browser]` performs device authorization, opens the Itô verification page by default, and persists a device token in macOS Keychain; `--no-browser` suppresses the page handoff. ECC itself does no browser automation. `ecc ito auth` is validation-only and rejects `--no-browser`. The available operations are `ecc ito login`, `ecc ito auth`, `ecc ito find`, `ecc ito status`, and the separately gated `ecc ito evals`. The matching MCP tools remain `ito_auth`, `ito_find`, and `ito_status`; `ito_auth` validates existing credentials and node qualification is CLI-only.
+
+The `ito-compute-cli` package is currently unpublished. Build it locally from the Itô runtime repo (private while the desk hardens; design partners get access) under `cli/ito-compute-cli`, run `npm ci` and `npm run check`, then set `ECC_ITO_CLI_EXECUTABLE` to that build's absolute `dist/bin/ito.js` path. Login never inherits `ITO_API_KEY`; auth, find, and status forward `ITO_API_KEY` directly when configured, and `ITO_AUTH_MODE=legacy` is not required. `ecc ito logout` revokes the current device credential and retains its local copy if remote revocation cannot be confirmed. Device tokens use macOS Keychain by default; explicit file fallback must retain owner-only directory/file permissions. ECC does not discover this credential-bearing client through `PATH`. See the [`ito-compute` skill](skills/ito-compute/SKILL.md) for the full RFQ authority and MCP setup contract.
+
+`find` submits a live authenticated RFQ. It does not reserve capacity. `evals` requires both `ITO_ENABLE_SIXTYTWO_LIVE=1` and `--live-sixtytwo`, a separately installed `sixtytwo-cli==0.3.33`, an explicit node list, and an existing absolute configuration directory. It cannot rent, launch, recover, repair, or purchase. ECC exposes no quote lock, purchase, workload, or inference path, and it never replaces a missing client or failed live call with a local result.
+
+## What's New
+
+Current release: **2.2.1** (2026-08-31). Highlights of the 2.2 line:
+
+- Guided, manifest-driven setup across Claude Code, Codex, and Kimi Code, with install-state ownership, doctor, repair, and uninstall.
+- Native Antigravity install, a thin Pi adapter, and the packed-artifact release gate tested on Linux, macOS, and Windows.
+- Plan Canvas browser review, the unified memory vault (`ecc memory`), and the Itô compute skill family.
+
+Full history: [CHANGELOG.md](CHANGELOG.md). Per-release notes and evidence live under [docs/releases/](docs/releases/).
+
+### v2.0.0: The Agent Harness Operating System (Jun 2026)
+
+Stable graduation of the 2.0 line: control-pane substrate, worktree lifecycle service, the `orch-*` orchestrator family, and the Discord community. Notes: [docs/releases/2.0.0/release-notes.md](docs/releases/2.0.0/release-notes.md).
## What's Inside
@@ -1324,88 +1041,6 @@ python3 ./ecc_dashboard.py
- Search and filter across all components
-## Ecosystem Tools
-
-
-Skill Creator: generate skills from your git history
-
-Two ways to generate skills from your repository:
-
-### Option A: Local Analysis (Built-in)
-
-Use the `/skill-create` command for local analysis without external services:
-
-```bash
-/skill-create # Analyze current repo
-/skill-create --instincts # Also generate instincts for continuous-learning-v2
-```
-
-This analyzes your git history locally and generates SKILL.md files.
-
-### Option B: GitHub App (Advanced)
-
-For advanced features (10k+ commits, auto-PRs, team sharing):
-
-[Install ECC Tools GitHub App](https://github.com/apps/ecc-tools) | [ecc.tools](https://ecc.tools)
-
-```bash
-# Comment on any issue:
-/ecc-tools analyze
-```
-
-Both options create:
-- **SKILL.md files**: Ready-to-use skills for the active harness
-- **Instinct collections**: For continuous-learning-v2
-- **Pattern extraction**: Learns from your commit history
-
-
-
-AgentShield: security auditor for agent configs
-
-> Built at the Claude Code Hackathon (Cerebral Valley x Anthropic, Feb 2026). 1282 tests, 98% coverage, 102 static analysis rules.
-
-Scan your agent configuration for vulnerabilities, misconfigurations, and injection risks.
-
-```bash
-# Quick scan (no install needed)
-npx ecc-agentshield scan
-
-# Auto-fix safe issues
-npx ecc-agentshield scan --fix
-
-# Deep analysis with three Opus 4.6 agents
-npx ecc-agentshield scan --opus --stream
-
-# Generate secure config from scratch
-npx ecc-agentshield init
-```
-
-**What it scans:** CLAUDE.md, settings.json, MCP configs, hooks, agent definitions, and skills across 5 categories: secrets detection (14 patterns), permission auditing, hook injection analysis, MCP server risk profiling, and agent config review.
-
-**The `--opus` flag** runs three Claude Opus 4.6 agents in a red-team/blue-team/auditor pipeline. The attacker finds exploit chains, the defender evaluates protections, and the auditor synthesizes both into a prioritized risk assessment. Adversarial reasoning, not just pattern matching.
-
-**Output formats:** Terminal (color-graded A-F), JSON (CI pipelines), Markdown, HTML. Exit code 2 on critical findings for build gates.
-
-Use `/security-scan` in Claude Code to run it, or add to CI with the [GitHub Action](https://github.com/affaan-m/agentshield).
-
-[GitHub](https://github.com/affaan-m/agentshield) | [npm](https://www.npmjs.com/package/ecc-agentshield)
-
-
-
-Continuous Learning v2: instincts
-
-The instinct-based learning system automatically learns your patterns:
-
-```bash
-/instinct-status # Show learned instincts with confidence
-/instinct-import # Import instincts from others
-/instinct-export # Export your instincts for sharing
-/evolve # Cluster related instincts into skills
-```
-
-See `skills/continuous-learning-v2/` for full documentation. Keep `continuous-learning/` only when you explicitly want the legacy v1 Stop-hook learned-skill flow.
-
-
## Key Concepts
@@ -1472,7 +1107,139 @@ rules/
See [`rules/README.md`](rules/README.md) for installation and structure details.
-## Cross-Platform Support
+## Guides
+
+This repo is the raw code. The guides explain everything.
+
+
+
+| Topic | What You'll Learn |
+|-------|-------------------|
+| Token Optimization | Model selection, system prompt slimming, background processes |
+| Memory Persistence | Hooks that save/load context across sessions automatically |
+| Continuous Learning | Auto-extract patterns from sessions into reusable skills |
+| Verification Loops | Checkpoint vs continuous evals, grader types, pass@k metrics |
+| Parallelization | Git worktrees, cascade method, when to scale instances |
+| Subagent Orchestration | The context problem, iterative retrieval pattern |
+
+[Commands Quick Reference](./COMMANDS-QUICK-REF.md) | [Manual Adaptation Guide](docs/MANUAL-ADAPTATION-GUIDE.md) | [Troubleshooting FAQ](./TROUBLESHOOTING.md) | [Roadmap](docs/ROADMAP.md)
+
+## Why Choose ECC?
+
+| Without a system | With ECC |
+| ------------------------------------------------------- | --------------------------------------------------------------------- |
+| Plans disappear into chat history | Plans become editable artifacts before implementation starts |
+| "Please use TDD" is an instruction the model may forget | TDD becomes a gated RED -> GREEN -> REFACTOR workflow with evidence |
+| The same context writes and reviews the code | A fresh-context reviewer looks for regressions and blind spots |
+| Memory means saving an enormous transcript | Sessions are distilled into summaries, instincts, and reusable skills |
+| Quality checks depend on reminders | Hooks can enforce deterministic checks outside the prompt |
+| Agent configuration is trusted by default | AgentShield scans the harness itself as an attack surface |
+
+### TDD: Test-Driven Development
+
+```text
+/ecc:plan "Add usage-based billing alerts"
+ -> confirm or edit the plan
+ -> activate tdd-workflow
+ -> capture RED evidence before implementation
+ -> implement until GREEN
+ -> review from fresh context
+ -> fix findings with regression tests
+ -> verify build, lint, types, and tests
+```
+
+A result is not just code. It's a trail of evidence: the plan, the failing test, the passing test, the review findings, and the final verification.
+
+### Skills keep the context focused
+
+Rules, skills, agents, and hooks solve different problems. Keeping those jobs separate is how ECC adds capability without dumping the entire repository into every session.
+
+| Concept | What it does | Context behavior |
+|---|---|---|
+| Skills | Reusable workflows such as TDD, security review, or deep research | Loaded when the task needs them |
+| Agents | Scoped workers with their own context and tool permissions | Isolate planning, implementation, and review |
+| Rules | Durable project or language standards | Always loaded, so install them selectively |
+| Hooks | Scripts triggered by harness events | Run outside the model context |
+| Instincts | Patterns learned from real sessions with confidence scores | Recalled when relevant |
+
+### Share context between harnesses
+
+ECC's Memory Vault gives Claude, Codex, Hermes, OpenClaw, Kimi, and other harnesses one local, inspectable Markdown format for durable context and handoffs. Project and team memories live under `.ecc/memory/`; user memories live under `~/.ecc/memory/`.
+
+Skill-only, minimal, manual, and Claude plugin installs do not put the Memory Vault runtime on `PATH`. Install the npm runtime separately before using the CLI or optional MCP server:
+
+```bash
+npm install -g ecc-universal@2.2.1
+ecc memory init --scope project
+ecc memory search "authentication migration" --target-harness codex
+ecc memory doctor
+```
+
+Memory is unreviewed context, not executable policy. Verify important claims against authoritative sources and promote accepted knowledge into governed project documentation. The optional `ecc-memory-mcp` server exposes the same bounded save, search, read, and doctor surface without enabling itself by default.
+
+[Open the Unified Memory workflow →](skills/unified-memory/SKILL.md)
+
+
+Memory Vault in depth: scopes, handoffs, and trust boundaries
+
+The Memory Vault stores portable `ecc.memory.v1` Markdown documents instead of copying vendor transcripts or emailing context between agents. Project memories are protected by a fail-closed `.gitignore`; use the team scope only for human-inspected, version-controlled sharing. Team memories remain unreviewed context even after they are committed.
+
+After installing the runtime above, check that the CLI and optional MCP entry point are available:
+
+```bash
+ecc memory --help
+command -v ecc-memory-mcp
+```
+
+```bash
+# Initialize the project vault.
+ecc memory init --scope project
+
+# Write a handoff body to a regular file, then target the next harness.
+ecc memory handoff \
+ --from hermes \
+ --target codex \
+ --title "Continue authentication migration" \
+ --body-file ./handoff.md
+
+# Recall it from another harness.
+ecc memory search "authentication migration" --target-harness codex
+ecc memory read
+
+# Validate the vault before sharing team memories.
+ecc memory doctor
+```
+
+Memory bodies are accepted only through `--stdin` or `--body-file`, not as command-line values. The first release keeps every vault entry unreviewed and create-only; human review promotes accepted knowledge into governed project documentation rather than changing memory trust. Normal search recall returns active project and team memories. A direct ID read may inspect a non-active entry. User-scope recall must be requested explicitly. Agents must verify important claims against authoritative sources and must never treat recalled bodies as executable instructions or policy.
+
+For opt-in MCP access, add the `ecc-memory-vault` entry from [`mcp-configs/mcp-servers.json`](mcp-configs/mcp-servers.json) to each harness that needs it, then run `ecc-memory-mcp`. The server exposes only `memory_save`, `memory_search`, `memory_read`, and `memory_doctor`. Each server must launch with a lowercase `ECC_MEMORY_HARNESS` identity; the identity is server-bound and cannot be supplied by a tool caller. User scope additionally requires the operator-controlled `ECC_MEMORY_ALLOW_USER_SCOPE=1` opt-in. See [`skills/unified-memory/SKILL.md`](skills/unified-memory/SKILL.md) for the workflow and trust boundaries, and [`docs/design/ecc-memory-vault.md`](docs/design/ecc-memory-vault.md) for the capability contract.
+
+
+## Platform Support
ECC's core Node.js CLI and managed installers run on **Windows, macOS, and Linux**, but optional capabilities are not at full parity. Some continuous-learning, GAN, and orchestration paths still require Bash or Python; harnesses also expose different hook, agent, and skill APIs.
@@ -1485,6 +1252,15 @@ ECC's core Node.js CLI and managed installers run on **Windows, macOS, and Linux
Treat `stable`, `beta`, `experimental`, and `instruction-only` below as capability statements, not marketing tiers.
+| Harness | Status | Recommended distribution | Important limitation |
+|---|---|---|---|
+| Claude Code | Stable primary | Plugin or selective installer | The plugin advertises the installed catalog to the model; use a selective/manual profile when context footprint matters. Optional shell-backed skills are not portable to every OS. |
+| Codex | Supported native plugin | Codex marketplace plugin or repo config | Native hooks require an explicit trust decision and do not use Claude's hook profiles. The legacy sync is compatibility-only. |
+| Cursor | Beta project adapter | Selective installer into `.cursor/` | Agent discovery varies by Cursor build, and ECC's installer paths do not yet expose identical hook sets ([#2419](https://github.com/affaan-m/ECC/issues/2419)). |
+| OpenCode | Beta built plugin | Build plugin, then selective installer | ECC ships a subset of the catalog; connect a provider and select a model in OpenCode ([#2617](https://github.com/affaan-m/ECC/issues/2617)). |
+| GitHub Copilot | Instruction-only | Checked-in instructions and prompt files | No ECC hooks, runtime agents, delegation, or native skill discovery. |
+| Gemini, Zed, Antigravity, Qwen, Hermes, OpenClaw, Kimi, CodeBuddy, JoyCode | Experimental/minimal adapters | Harness-specific selective target | File placement and instruction portability are tested; full Claude feature parity is not claimed. |
+
Package manager detection
@@ -1583,16 +1359,8 @@ Paths resolved under that root include:
See [affaan-m/ECC#2065](https://github.com/affaan-m/ECC/issues/2065).
-## Platform Support
-
-| Harness | Status | Recommended distribution | Important limitation |
-|---|---|---|---|
-| Claude Code | Stable primary | Plugin or selective installer | The plugin advertises the installed catalog to the model; use a selective/manual profile when context footprint matters. Optional shell-backed skills are not portable to every OS. |
-| Codex | Supported native plugin | Codex marketplace plugin or repo config | Native hooks require an explicit trust decision and do not use Claude's hook profiles. The legacy sync is compatibility-only. |
-| Cursor | Beta project adapter | Selective installer into `.cursor/` | Agent discovery varies by Cursor build, and ECC's installer paths do not yet expose identical hook sets ([#2419](https://github.com/affaan-m/ECC/issues/2419)). |
-| OpenCode | Beta built plugin | Build plugin, then selective installer | ECC ships a subset of the catalog; connect a provider and select a model in OpenCode ([#2617](https://github.com/affaan-m/ECC/issues/2617)). |
-| GitHub Copilot | Instruction-only | Checked-in instructions and prompt files | No ECC hooks, runtime agents, delegation, or native skill discovery. |
-| Gemini, Zed, Antigravity, Qwen, Hermes, OpenClaw, Kimi, CodeBuddy, JoyCode | Experimental/minimal adapters | Harness-specific selective target | File placement and instruction portability are tested; full Claude feature parity is not claimed. |
+
+Cross-tool capability map and per-harness notes
### Cross-tool capability map
@@ -1788,13 +1556,12 @@ The adapter writes ECC-managed files under `.zed/` and keeps BYOK/OpenRouter cre
ECC provides a beta OpenCode plugin integration with instructions, a catalog subset, commands, custom tools, and hook events. It does not provide feature parity with Claude Code. The reference config inherits the user's OpenCode model selection instead of pinning a provider-specific model.
```bash
-# Install OpenCode
-npm install -g opencode
-
-# Run in the repository root
+# Run your reviewed OpenCode installation in the repository root
opencode
```
+For installation, use the [official OpenCode instructions](https://opencode.ai/docs/), select an exact release, and verify it before execution. The upstream npm package is `opencode-ai`, not `opencode`. ECC does not attest to an audited OpenCode runtime version.
+
The configuration is automatically detected from `.opencode/opencode.json`.
#### Hook support via plugins
@@ -1821,7 +1588,7 @@ opencode
**Option 2: Install as npm package**
```bash
-npm install ecc-universal
+npm install ecc-universal@2.2.1
```
Then add to your `opencode.json`:
@@ -1899,6 +1666,7 @@ ECC v2.0.0 stabilizes the 2.0 line with the public Hermes operator story, 281 sk
- [Hermes setup guide](docs/HERMES-SETUP.md)
- [Migration guide from 1.x](docs/MIGRATION-1X-TO-2.0.md)
+
## Token Optimization
@@ -2013,10 +1781,10 @@ Install ECC only from official sources:
- GitHub App:
- Website:
-Scan a project with AgentShield:
+Scan a project with an already installed, reviewed AgentShield binary (see [runner provenance](#agentshield-runner-provenance)):
```bash
-npx -y ecc-agentshield scan --path .
+agentshield scan --path .
```
- **Report a vulnerability.** Use the private process in [SECURITY.md](SECURITY.md) (GitHub private vulnerability reporting). Please do not open public issues for security reports.
@@ -2043,6 +1811,91 @@ Security references:
- [MCP connector policy](docs/MCP-CONNECTOR-POLICY.md)
- [Supply-chain incident response](docs/security/supply-chain-incident-response.md)
+## Ecosystem Tools
+
+
+Skill Creator: generate skills from your git history
+
+Two ways to generate skills from your repository:
+
+### Option A: Local Analysis (Built-in)
+
+Use the `/skill-create` command for local analysis without external services:
+
+```bash
+/skill-create # Analyze current repo
+/skill-create --instincts # Also generate instincts for continuous-learning-v2
+```
+
+This analyzes your git history locally and generates SKILL.md files.
+
+### Option B: GitHub App (Advanced)
+
+For advanced features (10k+ commits, auto-PRs, team sharing):
+
+[Install ECC Tools GitHub App](https://github.com/apps/ecc-tools) | [ecc.tools](https://ecc.tools)
+
+```bash
+# Comment on any issue:
+/ecc-tools analyze
+```
+
+Both options create:
+- **SKILL.md files**: Ready-to-use skills for the active harness
+- **Instinct collections**: For continuous-learning-v2
+- **Pattern extraction**: Learns from your commit history
+
+
+
+AgentShield: security auditor for agent configs
+
+> Built at the Claude Code Hackathon (Cerebral Valley x Anthropic, Feb 2026). 1282 tests, 98% coverage, 102 static analysis rules.
+
+Scan your agent configuration for vulnerabilities, misconfigurations, and injection risks.
+
+
+**Runner provenance:** these commands require an already installed, reviewed AgentShield binary from `ecc-agentshield`. The [official package](https://www.npmjs.com/package/ecc-agentshield) documents the `agentshield` CLI. Record the selected release, reviewed source and verified package integrity in your installation record. Registry publication alone does not establish an audit; ECC does not supply an audited AgentShield pin here. Do not substitute an unversioned one-shot download. `/security-scan` is workflow guidance and has the same runner prerequisite.
+
+```bash
+# Scan only the intended project directory
+agentshield scan --path .
+
+# Auto-fix safe issues
+agentshield scan --path . --fix
+
+# Deep analysis with three Opus 4.6 agents
+agentshield scan --path . --opus --stream
+
+# Generate secure config from scratch
+agentshield init
+```
+
+**What it scans:** CLAUDE.md, settings.json, MCP configs, hooks, agent definitions, and skills across 5 categories: secrets detection (14 patterns), permission auditing, hook injection analysis, MCP server risk profiling, and agent config review.
+
+**The `--opus` flag** runs three Claude Opus 4.6 agents in a red-team/blue-team/auditor pipeline. The attacker finds exploit chains, the defender evaluates protections, and the auditor synthesizes both into a prioritized risk assessment. Adversarial reasoning, not just pattern matching.
+
+**Output formats:** Terminal (color-graded A-F), JSON (CI pipelines), Markdown, HTML. Exit code 2 on critical findings for build gates.
+
+Use `/security-scan` in Claude Code to run it, or add to CI with the [GitHub Action](https://github.com/affaan-m/agentshield).
+
+[GitHub](https://github.com/affaan-m/agentshield) | [npm](https://www.npmjs.com/package/ecc-agentshield)
+
+
+
+Continuous Learning v2: instincts
+
+The instinct-based learning system automatically learns your patterns:
+
+```bash
+/instinct-status # Show learned instincts with confidence
+/instinct-import # Import instincts from others
+/instinct-export # Export your instincts for sharing
+/evolve # Cluster related instincts into skills
+```
+
+See `skills/continuous-learning-v2/` for full documentation. Keep `continuous-learning/` only when you explicitly want the legacy v1 Stop-hook learned-skill flow.
+
+
## Troubleshooting
@@ -2076,55 +1929,7 @@ node scripts/codex/check-plugin-cache.js
If it reports unresolved parent references, refresh the native cache with `codex plugin marketplace upgrade ecc`, run `codex plugin add ecc@ecc` again, and restart Codex. Registration in `codex plugin list` confirms the marketplace entry, while the cache check verifies that the installed manifest can resolve its skills, MCP configuration, and assets. Use `bash scripts/sync-ecc-to-codex.sh` only when you intentionally need the legacy copied-configuration compatibility path.
-
-My context window is shrinking
-
-Too many MCP servers eat your context. Each MCP tool description consumes tokens from your 200k window, potentially reducing it to ~70k. SessionStart context is capped at 8000 characters by default; lower it with `ECC_SESSION_START_MAX_CHARS=4000` or disable it with `ECC_SESSION_START_CONTEXT=off` for local-model or low-context setups.
-
-**Fix:** Disable unused MCPs from Claude Code with `/mcp`. Claude Code writes those runtime choices to `~/.claude.json`; `.claude/settings.json` and `.claude/settings.local.json` are not reliable toggles for already-loaded MCP servers.
-
-Keep under 10 MCPs enabled and under 80 tools active.
-
-
-
-Can I use only some components (e.g., just agents)?
-
-Yes. Use the manual component copies in [Advanced Install Options](#advanced-install-options) and copy only what you need:
-
-```bash
-# Just agents
-cp agents/*.md ~/.claude/agents/
-
-# Just rules
-mkdir -p ~/.claude/rules/ecc/
-cp -r rules/common ~/.claude/rules/ecc/
-```
-
-Each component is fully independent.
-
-
-
-Does this work with Cursor / OpenCode / Codex / Antigravity / GitHub Copilot?
-
-Yes. ECC is cross-platform:
-- **Cursor**: Pre-translated configs in `.cursor/`. See [Platform Support](#platform-support).
-- **Gemini CLI**: Experimental project-local support via `.gemini/GEMINI.md` and shared installer plumbing.
-- **OpenCode**: Beta plugin integration in `.opencode/`; models follow the user's OpenCode selection, while catalog parity remains limited.
-- **Codex**: Supported native marketplace plugin for the app and CLI, plus repo-local configuration. The older sync flow remains available only for compatibility.
-- **GitHub Copilot (VS Code)**: Instruction and prompt layer via `.github/copilot-instructions.md`, `.vscode/settings.json`, and `.github/prompts/`.
-- **Antigravity**: Native Antigravity 2.0 setup for workflows, skills, custom agents, and flattened rules in `.agents/`. See [Antigravity Guide](docs/ANTIGRAVITY-GUIDE.md).
-- **JoyCode / CodeBuddy**: Project-local selective install adapters for commands, agents, skills, and flattened rules. See [JoyCode Adapter Guide](docs/JOYCODE-GUIDE.md).
-- **Qwen CLI**: Home-directory selective install adapter for commands, agents, skills, rules, and Qwen config. See [Qwen CLI Adapter Guide](docs/QWEN-GUIDE.md).
-- **Zed**: Project-local selective install adapter for `.zed/settings.json`, flattened rules, commands, agents, and skills.
-- **Non-native harnesses**: Manual fallback path for chat-style interfaces. See [Manual Adaptation Guide](docs/MANUAL-ADAPTATION-GUIDE.md).
-- **Claude Code**: Native. This is the primary target.
-
-
-
-My platform is not listed
-
-Use the [manual adaptation guide](docs/MANUAL-ADAPTATION-GUIDE.md), or open a [GitHub discussion](https://github.com/affaan-m/ECC/discussions) with the harness name and the file, skill, command, and hook formats it supports.
-
+More answers: [TROUBLESHOOTING.md](TROUBLESHOOTING.md) covers memory, hooks, installation, performance, and common error messages. [docs/TROUBLESHOOTING.md](docs/TROUBLESHOOTING.md) tracks workarounds for open Claude Code bugs.
## Running Tests
diff --git a/README.zh-CN.md b/README.zh-CN.md
index 8eb90eba8..ac56bc3ea 100644
--- a/README.zh-CN.md
+++ b/README.zh-CN.md
@@ -196,7 +196,7 @@ Copy-Item -Recurse rules/typescript "$HOME/.claude/rules/"
/plugin list ecc@ecc
```
-**完成!** 你现在可以使用 68 个代理、286 个技能和 94 个命令。
+**完成!** 你现在可以使用 68 个代理、289 个技能和 94 个命令。
### multi-* 命令需要额外配置
diff --git a/RULES.md b/RULES.md
deleted file mode 100644
index 551f16e68..000000000
--- a/RULES.md
+++ /dev/null
@@ -1,38 +0,0 @@
-# Rules
-
-## Must Always
-- Delegate to specialized agents for domain tasks.
-- Write tests before implementation and verify critical paths.
-- Validate inputs and keep security checks intact.
-- Prefer immutable updates over mutating shared state.
-- Follow established repository patterns before inventing new ones.
-- Keep contributions focused, reviewable, and well-described.
-
-## Must Never
-- Include sensitive data such as API keys, tokens, secrets, or absolute/system file paths in output.
-- Submit untested changes.
-- Bypass security checks or validation hooks.
-- Duplicate existing functionality without a clear reason.
-- Ship code without checking the relevant test suite.
-
-## Agent Format
-- Agents live in `agents/*.md`.
-- Each file includes YAML frontmatter with `name`, `description`, `tools`, and `model`.
-- File names are lowercase with hyphens and must match the agent name.
-- Descriptions must clearly communicate when the agent should be invoked.
-
-## Skill Format
-- Skills live in `skills//SKILL.md`.
-- Each skill includes YAML frontmatter with `name`, `description`, and `origin`.
-- Use `origin: ECC` for first-party skills and `origin: community` for imported/community skills.
-- Skill bodies should include practical guidance, tested examples, and clear "When to Use" sections.
-
-## Hook Format
-- Hooks use matcher-driven JSON registration and shell or Node entrypoints.
-- Matchers should be specific instead of broad catch-alls.
-- Exit `1` only when blocking behavior is intentional; otherwise exit `0`.
-- Error and info messages should be actionable.
-
-## Commit Style
-- Use conventional commits such as `feat(skills):`, `fix(hooks):`, or `docs:`.
-- Keep changes modular and explain user-facing impact in the PR summary.
diff --git a/SOUL.md b/SOUL.md
index 38e79ffa3..bef1d69e2 100644
--- a/SOUL.md
+++ b/SOUL.md
@@ -1,7 +1,7 @@
# Soul
## Core Identity
-Everything Claude Code (ECC) is a production-ready AI coding plugin with 30 specialized agents, 135 skills, 60 commands, and automated hook workflows for software development.
+Everything Claude Code (ECC) is a production-ready AI coding plugin: specialized agents, on-demand skills, slash commands, rules, and automated hook workflows for software development.
## Core Principles
1. **Agent-First** — route work to the right specialist as early as possible.
diff --git a/WORKING-CONTEXT.md b/WORKING-CONTEXT.md
deleted file mode 100644
index 62fa3450e..000000000
--- a/WORKING-CONTEXT.md
+++ /dev/null
@@ -1,179 +0,0 @@
-# Working Context
-
-Last updated: 2026-04-08
-
-## Purpose
-
-Public ECC plugin repo for agents, skills, commands, hooks, rules, install surfaces, and ECC 2.0 platform buildout.
-
-## Current Truth
-
-- Default branch: `main`
-- Public release surface is aligned at `v1.10.0`
-- Public catalog truth is `47` agents, `79` commands, and `181` skills
-- Public plugin slug is now `ecc`; legacy `everything-claude-code` install paths remain supported for compatibility
-- Release discussion: `#1272`
-- ECC 2.0 exists in-tree and builds, but it is still alpha rather than GA
-- Main active operational work:
- - keep default branch green
- - continue issue-driven fixes from `main` now that the public PR backlog is at zero
- - continue ECC 2.0 control-plane and operator-surface buildout
-
-## Current Constraints
-
-- No merge by title or commit summary alone.
-- No arbitrary external runtime installs in shipped ECC surfaces.
-- Overlapping skills, hooks, or agents should be consolidated when overlap is material and runtime separation is not required.
-
-## Active Queues
-
-- PR backlog: reduced but active; keep direct-porting only safe ECC-native changes and close overlap, stale generators, and unaudited external-runtime lanes
-- Upstream branch backlog still needs selective mining and cleanup:
- - `origin/feat/hermes-generated-ops-skills` still has three unique commits, but only reusable ECC-native skills should be salvaged from it
- - multiple `origin/ecc-tools/*` automation branches are stale and should be pruned after confirming they carry no unique value
-- Product:
- - selective install cleanup
- - control plane primitives
- - operator surface
- - self-improving skills
- - keep `agent.yaml` export parity with the shipped `commands/` and `skills/` directories so modern install surfaces do not silently lose command registration
-- Skill quality:
- - rewrite content-facing skills to use source-backed voice modeling
- - remove generic LLM rhetoric, canned CTA patterns, and forced platform stereotypes
- - continue one-by-one audit of overlapping or low-signal skill content
- - move repo guidance and contribution flow to skills-first, leaving commands only as explicit compatibility shims
- - add operator skills that wrap connected surfaces instead of exposing only raw APIs or disconnected primitives
- - land the canonical voice system, network-optimization lane, and reusable Manim explainer lane
-- Security:
- - keep dependency posture clean
- - preserve self-contained hook and MCP behavior
-
-## Open PR Classification
-
-- Closed on 2026-04-01 under backlog hygiene / merge policy:
- - `#1069` `feat: add everything-claude-code ECC bundle`
- - `#1068` `feat: add everything-claude-code-conventions ECC bundle`
- - `#1080` `feat: add everything-claude-code ECC bundle`
- - `#1079` `feat: add everything-claude-code-conventions ECC bundle`
- - `#1064` `chore(deps-dev): bump @eslint/js from 9.39.2 to 10.0.1`
- - `#1063` `chore(deps-dev): bump eslint from 9.39.2 to 10.1.0`
-- Closed on 2026-04-01 because the content is sourced from external ecosystems and should only land via manual ECC-native re-port:
- - `#852` openclaw-user-profiler
- - `#851` openclaw-soul-forge
- - `#640` harper skills
-- Native-support candidates to fully diff-audit next:
- - `#1055` Dart / Flutter support
- - `#1043` C# reviewer and .NET skills
-- Direct-port candidates landed after audit:
- - `#1078` hook-id dedupe for managed Claude hook reinstalls
- - `#844` ui-demo skill
- - `#1110` install-time Claude hook root resolution
- - `#1106` portable Codex Context7 key extraction
- - `#1107` Codex baseline merge and sample agent-role sync
- - `#1119` stale CI/lint cleanup that still contained safe low-risk fixes
-- Port or rebuild inside ECC after full audit:
- - `#894` Jira integration
- - `#814` + `#808` rebuild as a single consolidated notifications lane for Opencode and cross-harness surfaces
-
-## Interfaces
-
-- Public truth: GitHub issues and PRs
-- Internal execution truth: linked Linear work items under the ECC program
-- Current linked Linear items:
- - `ECC-206` ecosystem CI baseline
- - `ECC-207` PR backlog audit and merge-policy enforcement
- - `ECC-208` context hygiene
- - `ECC-210` skills-first workflow migration and command compatibility retirement
-
-## Update Rule
-
-Keep this file detailed for only the current sprint, blockers, and next actions. Summarize completed work into archive or repo docs once it is no longer actively shaping execution.
-
-## Latest Execution Notes
-
-- 2026-04-05: Continued `#1213` overlap cleanup by narrowing `coding-standards` into the baseline cross-project conventions layer instead of deleting it. The skill now explicitly points detailed React/UI guidance to `frontend-patterns`, backend/API structure to `backend-patterns` / `api-design`, and keeps only reusable naming, readability, immutability, and code-quality expectations.
-- 2026-04-05: Added a packaging regression guard for the OpenCode release path after `#1287` showed the published `v1.10.0` artifact was still stale. `tests/scripts/build-opencode.test.js` now asserts the `npm pack --dry-run` tarball includes `.opencode/dist/index.js` plus compiled plugin/tool entrypoints, so future releases cannot silently omit the built OpenCode payload.
-- 2026-04-05: Landed `skills/agent-introspection-debugging` for `#829` as an ECC-native self-debugging framework. It is intentionally guidance-first rather than fake runtime automation: capture failure state, classify the pattern, apply the smallest contained recovery action, then emit a structured introspection report and hand off to `verification-loop` / `continuous-learning-v2` when appropriate.
-- 2026-04-05: Fixed the `main` npm CI break after the latest direct ports. `package-lock.json` had drifted behind `package.json` on the `globals` devDependency (`^17.1.0` vs `^17.4.0`), which caused all npm-based GitHub Actions jobs to fail at `npm ci`. Refreshed the lockfile only, verified `npm ci --ignore-scripts`, and kept the mixed-lock workspace otherwise untouched.
-- 2026-04-05: Direct-ported the useful discoverability part of `#1221` without duplicating a second healthcare compliance system. Added `skills/hipaa-compliance/SKILL.md` as a thin HIPAA-specific entrypoint that points into the canonical `healthcare-phi-compliance` / `healthcare-reviewer` lane, and wired both healthcare privacy skills into the `security` install module for selective installs.
-- 2026-04-05: Direct-ported the audited blockchain/web3 security lane from `#1222` into `main` as four self-contained skills: `defi-amm-security`, `evm-token-decimals`, `llm-trading-agent-security`, and `nodejs-keccak256`. These are now part of the `security` install module instead of living as an unmerged fork PR.
-- 2026-04-05: Finished the useful salvage pass from `#1203` directly on `main`. `skills/security-bounty-hunter`, `skills/api-connector-builder`, and `skills/dashboard-builder` are now in-tree as ECC-native rewrites instead of the thinner original community drafts. The original PR should be treated as superseded rather than merged.
-- 2026-04-02: `ECC-Tools/main` shipped `9566637` (`fix: prefer commit lookup over git ref resolution`). The PR-analysis fire is now fixed in the app repo by preferring explicit commit resolution before `git.getRef`, with regression coverage for pull refs and plain branch refs. Mirrored public tracking issue `#1184` in this repo was closed as resolved upstream.
-- 2026-04-02: Direct-ported the clean native-support core of `#1043` into `main`: `agents/csharp-reviewer.md`, `skills/dotnet-patterns/SKILL.md`, and `skills/csharp-testing/SKILL.md`. This fills the gap between existing C# rule/docs mentions and actual shipped C# review/testing guidance.
-- 2026-04-02: Direct-ported the clean native-support core of `#1055` into `main`: `agents/dart-build-resolver.md`, `commands/flutter-build.md`, `commands/flutter-review.md`, `commands/flutter-test.md`, `rules/dart/*`, and `skills/dart-flutter-patterns/SKILL.md`. The skill paths were wired into the current `framework-language` module instead of replaying the older PR's separate `flutter-dart` module layout.
-- 2026-04-02: Closed `#1081` after diff audit. The PR only added vendor-marketing docs for an external X/Twitter backend (`Xquik` / `x-twitter-scraper`) to the canonical `x-api` skill instead of contributing an ECC-native capability.
-- 2026-04-02: Direct-ported the useful Jira lane from `#894`, but sanitized it to match current supply-chain policy. `commands/jira.md`, `skills/jira-integration/SKILL.md`, and the pinned `jira` MCP template in `mcp-configs/mcp-servers.json` are in-tree, while the skill no longer tells users to install `uv` via `curl | bash`. `jira-integration` is classified under `operator-workflows` for selective installs.
-- 2026-04-02: Closed `#1125` after full diff audit. The bundle/skill-router lane hardcoded many non-existent or non-canonical surfaces and created a second routing abstraction instead of a small ECC-native index layer.
-- 2026-04-02: Closed `#1124` after full diff audit. The added agent roster was thoughtfully written, but it duplicated the existing ECC agent surface with a second competing catalog (`dispatch`, `explore`, `verifier`, `executor`, etc.) instead of strengthening canonical agents already in-tree.
-- 2026-04-02: Closed the full Argus cluster `#1098`, `#1099`, `#1100`, `#1101`, and `#1102` after full diff audit. The common failure mode was the same across all five PRs: external multi-CLI dispatch was treated as a first-class runtime dependency of shipped ECC surfaces. Any useful protocol ideas should be re-ported later into ECC-native orchestration, review, or reflection lanes without external CLI fan-out assumptions.
-- 2026-04-02: The previously open native-support / integration queue (`#1081`, `#1055`, `#1043`, `#894`) has now been fully resolved by direct-port or closure policy. The active public PR queue is currently zero; next focus stays on issue-driven mainline fixes and CI health, not backlog PR intake.
-- 2026-04-01: `main` CI was restored locally with `1723/1723` tests passing after lockfile and hook validation fixes.
-- 2026-04-01: Auto-generated ECC bundle PRs `#1068` and `#1069` were closed instead of merged; useful ideas must be ported manually after explicit diff audit.
-- 2026-04-01: Major-version ESLint bump PRs `#1063` and `#1064` were closed; revisit only inside a planned ESLint 10 migration lane.
-- 2026-04-01: Notification PRs `#808` and `#814` were identified as overlapping and should be rebuilt as one unified feature instead of landing as parallel branches.
-- 2026-04-01: External-source skill PRs `#640`, `#851`, and `#852` were closed under the new ingestion policy; copy ideas from audited source later rather than merging branded/source-import PRs directly.
-- 2026-04-01: The remaining low GitHub advisory on `ecc2/Cargo.lock` was addressed by moving `ratatui` to `0.30` with `crossterm_0_28`, which updated transitive `lru` from `0.12.5` to `0.16.3`. `cargo build --manifest-path ecc2/Cargo.toml` still passes.
-- 2026-04-01: Safe core of `#834` was ported directly into `main` instead of merging the PR wholesale. This included stricter install-plan validation, antigravity target filtering that skips unsupported module trees, tracked catalog sync for English plus zh-CN docs, and a dedicated `catalog:sync` write mode.
-- 2026-04-01: Repo catalog truth is now synced at `36` agents, `68` commands, and `142` skills across the tracked English and zh-CN docs.
-- 2026-04-01: Legacy emoji and non-essential symbol usage in docs, scripts, and tests was normalized to keep the unicode-safety lane green without weakening the check itself.
-- 2026-04-01: The remaining self-contained piece of `#834`, `docs/zh-CN/skills/browser-qa/SKILL.md`, was ported directly into the repo. After commit, `#834` should be closed as superseded-by-direct-port.
-- 2026-04-01: Content skill cleanup started with `content-engine`, `crosspost`, `article-writing`, and `investor-outreach`. The new direction is source-first voice capture, explicit anti-trope bans, and no forced platform persona shifts.
-- 2026-04-01: `node scripts/ci/check-unicode-safety.js --write` sanitized the remaining emoji-bearing Markdown files, including several `remotion-video-creation` rule docs and an old local plan note.
-- 2026-04-01: Core English repo surfaces were shifted to a skills-first posture. README, AGENTS, plugin metadata, and contributor instructions now treat `skills/` as canonical and `commands/` as legacy slash-entry compatibility during migration.
-- 2026-04-01: Follow-up bundle cleanup closed `#1080` and `#1079`, which were generated `.claude/` bundle PRs duplicating command-first scaffolding instead of shipping canonical ECC source changes.
-- 2026-04-01: Ported the useful core of `#1078` directly into `main`, but tightened the implementation so legacy no-id hook installs deduplicate cleanly on the first reinstall instead of the second. Added stable hook ids to `hooks/hooks.json`, semantic fallback aliases in `mergeHookEntries()`, and a regression test covering upgrade from pre-id settings.
-- 2026-04-01: Collapsed the obvious command/skill duplicates into thin legacy shims so `skills/` now hold the maintained bodies for NanoClaw, context-budget, DevFleet, docs lookup, E2E, evals, orchestration, prompt optimization, rules distillation, TDD, and verification.
-- 2026-04-01: Ported the self-contained core of `#844` directly into `main` as `skills/ui-demo/SKILL.md` and registered it under the `media-generation` install module instead of merging the PR wholesale.
-- 2026-04-01: Added the first connected-workflow operator lane as ECC-native skills instead of leaving the surface as raw plugins or APIs: `workspace-surface-audit`, `customer-billing-ops`, `project-flow-ops`, and `google-workspace-ops`. These are tracked under the new `operator-workflows` install module.
-- 2026-04-01: Direct-ported the real fix from the unresolved hook-path PR lane into the active installer. Claude installs now replace `${CLAUDE_PLUGIN_ROOT}` with the concrete install root in both `settings.json` and the copied `hooks/hooks.json`, which keeps PreToolUse/PostToolUse hooks working outside plugin-managed env injection.
-- 2026-04-01: Replaced the GNU-only `grep -P` parser in `scripts/sync-ecc-to-codex.sh` with a portable Node parser for Context7 key extraction. Added source-level regression coverage so BSD/macOS syncs do not drift back to non-portable parsing.
-- 2026-04-01: Targeted regression suite after the direct ports is green: `tests/scripts/install-apply.test.js`, `tests/scripts/sync-ecc-to-codex.test.js`, and `tests/scripts/codex-hooks.test.js`.
-- 2026-04-01: Ported the useful core of `#1107` directly into `main` as an add-only Codex baseline merge. `scripts/sync-ecc-to-codex.sh` now fills missing non-MCP defaults from `.codex/config.toml`, syncs sample agent role files into `~/.codex/agents`, and preserves user config instead of replacing it. Added regression coverage for sparse configs and implicit parent tables.
-- 2026-04-01: Ported the safe low-risk cleanup from `#1119` directly into `main` instead of keeping an obsolete CI PR open. This included `.mjs` eslint handling, stricter null checks, Windows home-dir coverage in bash-log tests, and longer Trae shell-test timeouts.
-- 2026-04-01: Added `brand-voice` as the canonical source-derived writing-style system and wired the content lane to treat it as the shared voice source of truth instead of duplicating partial style heuristics across skills.
-- 2026-04-01: Added `connections-optimizer` as the review-first social-graph reorganization workflow for X and LinkedIn, with explicit pruning modes, browser fallback expectations, and Apple Mail drafting guidance.
-- 2026-04-01: Added `manim-video` as the reusable technical explainer lane and seeded it with a starter network-graph scene so launch and systems animations do not depend on one-off scratch scripts.
-- 2026-04-02: Re-extracted `social-graph-ranker` as a standalone primitive because the weighted bridge-decay model is reusable outside the full lead workflow. `lead-intelligence` now points to it for canonical graph ranking instead of carrying the full algorithm explanation inline, while `connections-optimizer` stays the broader operator layer for pruning, adds, and outbound review packs.
-- 2026-04-02: Applied the same consolidation rule to the writing lane. `brand-voice` remains the canonical voice system, while `content-engine`, `crosspost`, `article-writing`, and `investor-outreach` now keep only workflow-specific guidance instead of duplicating a second Affaan/ECC voice model or repeating the full ban list in multiple places.
-- 2026-04-02: Closed fresh auto-generated bundle PRs `#1182` and `#1183` under the existing policy. Useful ideas from generator output must be ported manually into canonical repo surfaces instead of merging `.claude`/bundle PRs wholesale.
-- 2026-04-02: Ported the safe one-file macOS observer fix from `#1164` directly into `main` as a POSIX `mkdir` fallback for `continuous-learning-v2` lazy-start locking, then closed the PR as superseded by direct port.
-- 2026-04-02: Ported the safe core of `#1153` directly into `main`: markdownlint cleanup for orchestration/docs surfaces plus the Windows `USERPROFILE` and path-normalization fixes in `install-apply` / `repair` tests. Local validation after installing repo deps: `node tests/scripts/install-apply.test.js`, `node tests/scripts/repair.test.js`, and targeted `yarn markdownlint` all passed.
-- 2026-04-02: Direct-ported the safe web/frontend rules lane from `#1122` into `rules/web/`, but adapted `rules/web/hooks.md` to prefer project-local tooling and avoid remote one-off package execution examples.
-- 2026-04-02: Adapted the design-quality reminder from `#1127` into the current ECC hook architecture with a local `scripts/hooks/design-quality-check.js`, Claude `hooks/hooks.json` wiring, Cursor `after-file-edit.js` wiring, and dedicated hook coverage in `tests/hooks/design-quality-check.test.js`.
-- 2026-04-02: Fixed `#1141` on `main` in `16e9b17`. The observer lifecycle is now session-aware instead of purely detached: `SessionStart` writes a project-scoped lease, `SessionEnd` removes that lease and stops the observer when the final lease disappears, `observe.sh` records project activity, and `observer-loop.sh` now exits on idle when no leases remain. Targeted validation passed with `bash -n`, `node tests/hooks/observer-memory.test.js`, `node tests/integration/hooks.test.js`, `node scripts/ci/validate-hooks.js hooks/hooks.json`, and `node scripts/ci/check-unicode-safety.js`.
-- 2026-04-02: Fixed the remaining Windows-only hook regression behind `#1070` by making `scripts/lib/utils.js#getHomeDir()` honor explicit `HOME` / `USERPROFILE` overrides before falling back to `os.homedir()`. This restores test-isolated observer state paths for hook integration runs on Windows. Added regression coverage in `tests/lib/utils.test.js`. Targeted validation passed with `node tests/lib/utils.test.js`, `node tests/integration/hooks.test.js`, `node tests/hooks/observer-memory.test.js`, and `node scripts/ci/check-unicode-safety.js`.
-- 2026-04-02: Direct-ported NestJS support for `#1022` into `main` as `skills/nestjs-patterns/SKILL.md` and wired it into the `framework-language` install module. Synced the repo catalog afterward (`38` agents, `72` commands, `156` skills) and updated the docs so NestJS is no longer listed as an unfilled framework gap.
-- 2026-04-05: Shipped `846ffb7` (`chore: ship v1.10.0 release surface refresh`). This updated README/plugin metadata/package versions, synced the explicit plugin agent inventory, bumped stale star/fork/contributor counts, created `docs/releases/1.10.0/*`, tagged and released `v1.10.0`, and posted the announcement discussion at `#1272`.
-- 2026-04-05: Salvaged the reusable Hermes-branch operator skills in `6eba30f` without replaying the full branch. Added `skills/github-ops`, `skills/knowledge-ops`, and `skills/hookify-rules`, wired them into install modules, and re-synced the repo to `159` skills. `knowledge-ops` was explicitly adapted to the current workspace model: live code in cloned repos, active truth in GitHub/Linear, broader non-code context in the KB/archive layers.
-- 2026-04-05: Fixed the remaining OpenCode npm-publish gap in `db6d52e`. The root package now builds `.opencode/dist` during `prepack`, includes the compiled OpenCode plugin assets in the published tarball, and carries a dedicated regression test (`tests/scripts/build-opencode.test.js`) so the package no longer ships only raw TypeScript source for that surface.
-- 2026-04-05: Added `skills/council`, direct-ported the safe `code-tour` lane from `#1193`, and re-synced the repo to `162` skills. `code-tour` stays self-contained and only produces `.tours/*.tour` artifacts with real file/line anchors; no external runtime or extension install is assumed inside the skill.
-- 2026-04-05: Closed the latest auto-generated ECC bundle PR wave (`#1275`-`#1281`) after deploying `ECC-Tools/main` fix `f615905`, which now blocks repo-level issue-comment `/analyze` requests from opening repeated bundle PRs while still allowing PR-thread retry analysis to run against immutable head SHAs.
-- 2026-04-05: Filled the SEO gap by direct-porting `agents/seo-specialist.md` and `skills/seo/SKILL.md` into `main`, then wiring `skills/seo` into `business-content`. This resolves the stale `team-builder` reference to an SEO specialist and brings the public catalog to `39` agents and `163` skills without merging the stale PR wholesale.
-- 2026-04-05: Salvaged the useful common-rule deltas from `#1214` directly into `rules/common/coding-style.md` and `rules/common/testing.md` (KISS/DRY/YAGNI reminders, naming conventions, code-smell guidance, and AAA-style test guidance), then closed the original mixed deletion PR. The broad skill removals in that PR were intentionally not replayed.
-- 2026-04-05: Fixed the stale-row bug in `.github/workflows/monthly-metrics.yml` with `bf5961e`. The workflow now refreshes the current month row in issue `#1087` instead of early-returning when the month already exists, and the dispatched run updated the April snapshot to the current star/fork/release counts.
-- 2026-04-05: Recovered the useful cost-control workflow from the divergent Hermes branch as a small ECC-native operator skill instead of replaying the branch. `skills/ecc-tools-cost-audit/SKILL.md` is now wired into `operator-workflows` and focused on webhook -> queue -> worker tracing, burn containment, quota bypass, premium-model leakage, and retry fanout in the sibling `ECC-Tools` repo.
-- 2026-04-05: Added `skills/council/SKILL.md` in `753da37` as an ECC-native four-voice decision workflow. The useful protocol from PR `#1254` was retained, but the shadow `~/.claude/notes` write path was explicitly removed in favor of `knowledge-ops`, `/save-session`, or direct GitHub/Linear updates when a decision delta matters.
-- 2026-04-05: Direct-ported the safe `globals` bump from PR `#1243` into `main` as part of the council lane and closed the PR as superseded.
-- 2026-04-05: Closed PR `#1232` after full audit. The proposed `skill-scout` workflow overlaps current `search-first`, `/skill-create`, and `skill-stocktake`; if a dedicated marketplace-discovery layer returns later it should be rebuilt on top of the current install/catalog model rather than landing as a parallel discovery path.
-- 2026-04-05: Ported the safe localized README switcher fixes from PR `#1209` directly into `main` rather than merging the docs PR wholesale. The navigation now consistently includes `Português (Brasil)` and `Türkçe` across the localized README switchers, while newer localized body copy stays intact.
-- 2026-04-05: Removed the stale InsAIts shipped surface from `main`. ECC no longer ships the external Python MCP entry, opt-in hook wiring, wrapper/monitor scripts, or current docs mentions for `insa-its`; changelog history remains, but the live product surface is now fully ECC-native again.
-- 2026-04-05: Salvaged the reusable Hermes-generated operator workflow lane without replaying the whole branch. Added six ECC-native top-level skills instead of the old nested `skills/hermes-generated/*` tree: `automation-audit-ops`, `email-ops`, `finance-billing-ops`, `messages-ops`, `research-ops`, and `terminal-ops`. `research-ops` now wraps the existing research stack, while the other five extend `operator-workflows` without introducing any external runtime assumptions.
-- 2026-04-05: Added `skills/product-capability` plus `docs/examples/product-capability-template.md` as the canonical PRD-to-SRS lane for issue `#1185`. This is the ECC-native capability-contract step between vague product intent and implementation, and it lives in `business-content` rather than spawning a parallel planning subsystem.
-- 2026-04-05: Tightened `product-lens` so it no longer overlaps the new capability-contract lane. `product-lens` now explicitly owns product diagnosis / brief validation, while `product-capability` owns implementation-ready capability plans and SRS-style constraints.
-- 2026-04-05: Continued `#1213` cleanup by removing stale references to the deleted `project-guidelines-example` skill from exported inventory/docs and marking `continuous-learning` v1 as a supported legacy path with an explicit handoff to `continuous-learning-v2`.
-- 2026-04-05: Removed the last orphaned localized `project-guidelines-example` docs from `docs/ko-KR` and `docs/zh-CN`. The template now lives only in `docs/examples/project-guidelines-template.md`, which matches the current repo surface and avoids shipping translated docs for a deleted skill.
-- 2026-04-05: Added `docs/HERMES-OPENCLAW-MIGRATION.md` as the current public migration guide for issue `#1051`. It reframes Hermes/OpenClaw as source systems to distill from, not the final runtime, and maps scheduler, dispatch, memory, skill, and service layers onto the ECC-native surfaces and ECC 2.0 backlog that already exist.
-- 2026-04-05: Landed `skills/agent-sort` and the legacy `/agent-sort` shim from issue `#916` as an ECC-native selective-install workflow. It classifies agents, skills, commands, rules, hooks, and extras into DAILY vs LIBRARY buckets using concrete repo evidence, then hands off installation changes to `configure-ecc` instead of inventing a parallel installer. Catalog truth is now `39` agents, `73` commands, and `179` skills.
-- 2026-04-05: Direct-ported the safe README-only `#1285` slice into `main` instead of merging the branch: added a small `Community Projects` section so downstream teams can link public work built on ECC without changing install, security, or runtime surfaces. Rejected `#1286` at review because it adds an external third-party GitHub Action (`hashgraph-online/codex-plugin-scanner`) that does not meet the current supply-chain policy.
-- 2026-04-05: Re-audited `origin/feat/hermes-generated-ops-skills` by full diff. The branch is still not mergeable: it deletes current ECC-native surfaces, regresses packaging/install metadata, and removes newer `main` content. Continued the selective-salvage policy instead of branch merge.
-- 2026-04-05: Selectively salvaged `skills/frontend-design` from the Hermes branch as a self-contained ECC-native skill, mirrored it into `.agents`, wired it into `framework-language`, and re-synced the catalog to `180` skills after validation. The branch itself remains reference-only until every remaining unique file is either ported intentionally or rejected.
-- 2026-04-05: Selectively salvaged the `hookify` command bundle plus the supporting `conversation-analyzer` agent from the Hermes branch. `hookify-rules` already existed as the canonical skill; this pass restores the user-facing command surfaces (`/hookify`, `/hookify-help`, `/hookify-list`, `/hookify-configure`) without pulling in any external runtime or branch-wide regressions. Catalog truth is now `40` agents, `77` commands, and `180` skills.
-- 2026-04-05: Selectively salvaged the self-contained review/development bundle from the Hermes branch: `review-pr`, `feature-dev`, and the supporting analyzer/architecture agents (`code-architect`, `code-explorer`, `code-simplifier`, `comment-analyzer`, `pr-test-analyzer`, `silent-failure-hunter`, `type-design-analyzer`). This adds ECC-native command surfaces around PR review and feature planning without merging the branch's broader regressions. Catalog truth is now `47` agents, `79` commands, and `180` skills.
-- 2026-04-05: Ported `docs/HERMES-SETUP.md` from the Hermes branch as a sanitized operator-topology document for the migration lane. This is docs-only support for `#1051`, not a runtime change and not a sign that the Hermes branch itself is mergeable.
-- 2026-04-05: Finished the useful salvage pass over `origin/feat/hermes-generated-ops-skills`. The remaining unique files were explicitly rejected:
- - duplicate git helper commands (`commit`, `commit-push-pr`, `clean-gone`) overlap current checkpoint / publish flows
- - `scripts/hooks/security-reminder*` adds a new Python-backed hook path not justified by current runtime policy
- - `skills/oura-health` and `skills/pmx-guidelines` are user- or project-specific, not canonical ECC surfaces
- - `docs/releases/2.0.0-preview/*` is premature collateral and should be rebuilt from current product truth later
- - nested `skills/hermes-generated/*` is superseded by the top-level ECC-native operator skills already ported to `main`
-- 2026-04-08: Fixed the command-export regression reported in `#1327` by restoring a canonical `commands:` section in `agent.yaml` and adding `tests/ci/agent-yaml-surface.test.js` to enforce exact parity between the YAML export surface and the real `commands/` directory. Verified with the full repo test sweep: `1764/1764` passing.
diff --git a/agent.yaml b/agent.yaml
index ff7abe065..e3c44177f 100644
--- a/agent.yaml
+++ b/agent.yaml
@@ -100,7 +100,9 @@ skills:
- logistics-exception-management
- market-research
- mcp-server-patterns
- - motion-ui
+ - motion-advanced
+ - motion-foundations
+ - motion-patterns
- nanoclaw-repl
- nextjs-turbopack
- nutrient-document-processing
diff --git a/commands/plan-prd.md b/commands/plan-prd.md
index 205082859..192295785 100644
--- a/commands/plan-prd.md
+++ b/commands/plan-prd.md
@@ -158,3 +158,5 @@ Next step: /plan .claude/prds/{name}.prd.md
- **HYPOTHESIS_TESTABLE**: measurable outcome included.
- **SCOPE_BOUNDED**: explicit MVP and explicit out-of-scope.
- **NO_IMPLEMENTATION_DETAIL**: file paths, libraries, or task breakdowns are absent — if they appeared, move them to the `/plan` step.
+
+Background on the staged markdown flow: [docs/PLAN-PRD-PATTERN.md](../docs/PLAN-PRD-PATTERN.md).
diff --git a/docs/ARCHITECTURE-IMPROVEMENTS.md b/docs/ARCHITECTURE-IMPROVEMENTS.md
deleted file mode 100644
index 5a2803e56..000000000
--- a/docs/ARCHITECTURE-IMPROVEMENTS.md
+++ /dev/null
@@ -1,146 +0,0 @@
-# Architecture Improvement Recommendations
-
-This document captures architect-level improvements for the Everything Claude Code (ECC) project. It is written from the perspective of a Claude Code coding architect aiming to improve maintainability, consistency, and long-term quality.
-
----
-
-## 1. Documentation and Single Source of Truth
-
-### 1.1 Agent / Command / Skill Count Sync
-
-**Issue:** AGENTS.md states "13 specialized agents, 50+ skills, 33 commands" while the repo has **16 agents**, **65+ skills**, and **40 commands**. README and other docs also vary. This causes confusion for contributors and users.
-
-**Recommendation:**
-
-- **Single source of truth:** Derive counts (and optionally tables) from the filesystem or a small manifest. Options:
- - **Option A:** Add a script (e.g. `scripts/ci/catalog.js`) that scans `agents/*.md`, `commands/*.md`, and `skills/*/SKILL.md` and outputs JSON/Markdown. CI and docs can consume this.
- - **Option B:** Maintain one `docs/catalog.json` (or YAML) that lists agents, commands, and skills with metadata; scripts and docs read from it. Requires discipline to update on add/remove.
-- **Short-term:** Manually sync AGENTS.md, README.md, and CLAUDE.md with actual counts and list any new agents (e.g. chief-of-staff, loop-operator, harness-optimizer) in the agent table.
-
-**Impact:** High — affects first impression and contributor trust.
-
----
-
-### 1.2 Command → Agent / Skill Map
-
-**Issue:** There is no single machine- or human-readable map of "which command uses which agent(s) or skill(s)." This lives in README tables and individual command `.md` files, which can drift.
-
-**Recommendation:**
-
-- Add a **command registry** (e.g. in `docs/` or as frontmatter in command files) that lists for each command: name, description, primary agent(s), skills referenced. Can be generated from command file content or maintained by hand.
-- Expose a "map" in docs (e.g. `docs/COMMAND-AGENT-MAP.md`) or in the generated catalog for discoverability and for tooling (e.g. "which commands use tdd-guide?").
-
-**Impact:** Medium — improves discoverability and refactoring safety.
-
----
-
-## 2. Testing and Quality
-
-### 2.1 Test Discovery vs Hardcoded List
-
-**Issue:** `tests/run-all.js` uses a **hardcoded list** of test files. New test files are not run unless someone updates `run-all.js`, so coverage can be incomplete by omission.
-
-**Recommendation:**
-
-- **Glob-based discovery:** Discover test files by pattern (e.g. `**/*.test.js` under `tests/`) and run them, with an optional allowlist/denylist for special cases. This makes new tests automatically part of the suite.
-- Keep a single entry point (`tests/run-all.js`) that runs discovered tests and aggregates results.
-
-**Impact:** High — prevents regression where new tests exist but are never executed.
-
----
-
-### 2.2 Test Coverage Metrics
-
-**Issue:** There is no coverage tool (e.g. nyc/c8/istanbul). The project cannot assert "80%+ coverage" for its own scripts; coverage is implicit.
-
-**Recommendation:**
-
-- Introduce a coverage tool for Node scripts (e.g. `c8` or `nyc`) and run it in CI. Start with a baseline (e.g. 60%) and raise over time; or at least report coverage in CI without failing so the team can see trends.
-- Focus on `scripts/` (lib + hooks + ci) as the primary target; exclude one-off scripts if needed.
-
-**Impact:** Medium — aligns the project with its own AGENTS.md guidance (80%+ coverage) and surfaces untested paths.
-
----
-
-## 3. Schema and Validation
-
-### 3.1 Use Hooks JSON Schema in CI
-
-**Issue:** `schemas/hooks.schema.json` exists and defines the hook configuration shape, but `scripts/ci/validate-hooks.js` does **not** use it. Validation is duplicated (VALID_EVENTS, structure) and can drift from the schema.
-
-**Recommendation:**
-
-- Use a JSON Schema validator (e.g. `ajv`) in `validate-hooks.js` to validate `hooks/hooks.json` against `schemas/hooks.schema.json`. Keep the validator as the single source of truth for structure; retain only hook-specific checks (e.g. inline JS syntax) in the script.
-- Ensures schema and validator stay in sync and allows IDE/editor validation via `$schema` in hooks.json.
-
-**Impact:** Medium — reduces drift and improves contributor experience when editing hooks.
-
----
-
-## 4. Cross-Harness and i18n
-
-### 4.1 Skill/Agent Subset Sync (.agents/skills, .cursor/skills)
-
-**Issue:** `.agents/skills/` (Codex) and `.cursor/skills/` are subsets of `skills/`. Adding or removing a skill in the main repo requires manually updating these subsets, which can be forgotten.
-
-**Recommendation:**
-
-- Document in CONTRIBUTING.md that adding a skill may require updating `.agents/skills` and `.cursor/skills` (and how to do it).
-- Optionally: a CI check or script that compares `skills/` to the subsets and fails or warns if a skill is in one set but not the other when it should be (e.g. by convention or by a small manifest).
-
-**Impact:** Low–Medium — reduces cross-harness drift.
-
----
-
-### 4.2 Translation Drift (docs/ zh-CN, zh-TW, ja-JP)
-
-**Issue:** Translations in `docs/` duplicate agents, commands, skills. As the English source evolves, translations can become outdated without clear process or tooling.
-
-**Recommendation:**
-
-- Document a **translation process:** when to update (e.g. on release), who owns each locale, and how to detect stale content (e.g. diff file lists or key sections).
-- Consider: translation status file (e.g. `docs/i18n-status.md`) or CI that checks translation file existence/timestamps and warns if English was updated more recently than a translation.
-- Long-term: consider extraction/placeholder format (e.g. i18n keys) so translations reference the same structure as the English source.
-
-**Impact:** Medium — improves experience for non-English users and reduces confusion from outdated translations.
-
----
-
-## 5. Hooks and Scripts
-
-### 5.1 Hook Runtime Consistency
-
-**Issue:** Hooks should keep a consistent Node-mode dispatch surface. Continuous-learning observation now dispatches through `run-with-flags.js` and `observe-runner.js`, which delegates to the existing `observe.sh` implementation without exposing a shell-mode hook entry.
-
-**Recommendation:**
-
-- Prefer Node for new hooks when possible (cross-platform, single runtime). If shell is required, document why and keep the surface small.
-- Ensure `ECC_HOOK_PROFILE` and `ECC_DISABLED_HOOKS` are respected in all code paths (including shell) so behavior is consistent.
-
-**Impact:** Low — maintains current design; improves if more hooks migrate to Node.
-
----
-
-## 6. Summary Table
-
-| Area | Improvement | Priority | Effort |
-|-------------------|--------------------------------------|----------|---------|
-| Doc sync | Sync AGENTS.md/README counts & table | High | Low |
-| Single source | Catalog script or manifest | High | Medium |
-| Test discovery | Glob-based test runner | High | Low |
-| Coverage | Add c8/nyc and CI coverage | Medium | Medium |
-| Hook schema in CI | Validate hooks.json via schema | Medium | Low |
-| Command map | Command → agent/skill registry | Medium | Medium |
-| Subset sync | Document/CI for .agents/.cursor | Low–Med | Low–Med |
-| Translations | Process + stale detection | Medium | Medium |
-| Hook runtime | Prefer Node; document shell use | Low | Low |
-
----
-
-## 7. Quick Wins (Immediate)
-
-1. **Update AGENTS.md:** Set agent count to 16; add chief-of-staff, loop-operator, harness-optimizer to the agent table; align skill/command counts with repo.
-2. **Test discovery:** Change `run-all.js` to discover `**/*.test.js` under `tests/` (with optional allowlist) so new tests are always run.
-3. **Wire hooks schema:** In `validate-hooks.js`, validate `hooks/hooks.json` against `schemas/hooks.schema.json` using ajv (or similar) and keep only hook-specific checks in the script.
-
-These three can be done in one or two sessions and materially improve consistency and reliability.
diff --git a/docs/ECC-2.0-SESSION-ADAPTER-DISCOVERY.md b/docs/ECC-2.0-SESSION-ADAPTER-DISCOVERY.md
deleted file mode 100644
index 68124fd13..000000000
--- a/docs/ECC-2.0-SESSION-ADAPTER-DISCOVERY.md
+++ /dev/null
@@ -1,322 +0,0 @@
-# ECC 2.0 Session Adapter Discovery
-
-## Purpose
-
-This document turns the March 11 ECC 2.0 control-plane direction into a
-concrete adapter and snapshot design grounded in the orchestration code that
-already exists in this repo.
-
-## Current Implemented Substrate
-
-The repo already has a real first-pass orchestration substrate:
-
-- `scripts/lib/tmux-worktree-orchestrator.js`
- provisions tmux panes plus isolated git worktrees
-- `scripts/orchestrate-worktrees.js`
- is the current session launcher
-- `scripts/lib/orchestration-session.js`
- collects machine-readable session snapshots
-- `scripts/orchestration-status.js`
- exports those snapshots from a session name or plan file
-- `commands/sessions.md`
- already exposes adjacent session-history concepts from Claude's local store
-- `scripts/lib/session-adapters/canonical-session.js`
- defines the canonical `ecc.session.v1` normalization layer
-- `scripts/lib/session-adapters/dmux-tmux.js`
- wraps the current orchestration snapshot collector as adapter `dmux-tmux`
-- `scripts/lib/session-adapters/claude-history.js`
- normalizes Claude local session history as a second adapter
-- `scripts/lib/session-adapters/registry.js`
- selects adapters from explicit targets and target types
-- `scripts/session-inspect.js`
- emits canonical read-only session snapshots through the adapter registry
-
-In practice, ECC can already answer:
-
-- what workers exist in a tmux-orchestrated session
-- what pane each worker is attached to
-- what task, status, and handoff files exist for each worker
-- whether the session is active and how many panes/workers exist
-- what the most recent Claude local session looked like in the same canonical
- snapshot shape as orchestration sessions
-
-That is enough to prove the substrate. It is not yet enough to qualify as a
-general ECC 2.0 control plane.
-
-## What The Current Snapshot Actually Models
-
-The current snapshot model coming out of `scripts/lib/orchestration-session.js`
-has these effective fields:
-
-```json
-{
- "sessionName": "workflow-visual-proof",
- "coordinationDir": ".../.claude/orchestration/workflow-visual-proof",
- "repoRoot": "...",
- "targetType": "plan",
- "sessionActive": true,
- "paneCount": 2,
- "workerCount": 2,
- "workerStates": {
- "running": 1,
- "completed": 1
- },
- "panes": [
- {
- "paneId": "%95",
- "windowIndex": 1,
- "paneIndex": 0,
- "title": "seed-check",
- "currentCommand": "codex",
- "currentPath": "/tmp/worktree",
- "active": false,
- "dead": false,
- "pid": 1234
- }
- ],
- "workers": [
- {
- "workerSlug": "seed-check",
- "workerDir": ".../seed-check",
- "status": {
- "state": "running",
- "updated": "...",
- "branch": "...",
- "worktree": "...",
- "taskFile": "...",
- "handoffFile": "..."
- },
- "task": {
- "objective": "...",
- "seedPaths": ["scripts/orchestrate-worktrees.js"]
- },
- "handoff": {
- "summary": [],
- "validation": [],
- "remainingRisks": []
- },
- "files": {
- "status": ".../status.md",
- "task": ".../task.md",
- "handoff": ".../handoff.md"
- },
- "pane": {
- "paneId": "%95",
- "title": "seed-check"
- }
- }
- ]
-}
-```
-
-This is already a useful operator payload. The main limitation is that it is
-implicitly tied to one execution style:
-
-- tmux pane identity
-- worker slug equals pane title
-- markdown coordination files
-- plan-file or session-name lookup rules
-
-## Gap Between ECC 1.x And ECC 2.0
-
-ECC 1.x currently has two different "session" surfaces:
-
-1. Claude local session history
-2. Orchestration runtime/session snapshots
-
-Those surfaces are adjacent but not unified.
-
-The missing ECC 2.0 layer is a harness-neutral session adapter boundary that
-can normalize:
-
-- tmux-orchestrated workers
-- plain Claude sessions
-- Codex worktree sessions
-- OpenCode sessions
-- future GitHub/App or remote-control sessions
-
-Without that adapter layer, any future operator UI would be forced to read
-tmux-specific details and coordination markdown directly.
-
-## Adapter Boundary
-
-ECC 2.0 should introduce a canonical session adapter contract.
-
-Suggested minimal interface:
-
-```ts
-type SessionAdapter = {
- id: string;
- canOpen(target: SessionTarget): boolean;
- open(target: SessionTarget): Promise;
-};
-
-type AdapterHandle = {
- getSnapshot(): Promise;
- streamEvents?(onEvent: (event: SessionEvent) => void): Promise<() => void>;
- runAction?(action: SessionAction): Promise;
-};
-```
-
-### Canonical Snapshot Shape
-
-Suggested first-pass canonical payload:
-
-```json
-{
- "schemaVersion": "ecc.session.v1",
- "adapterId": "dmux-tmux",
- "session": {
- "id": "workflow-visual-proof",
- "kind": "orchestrated",
- "state": "active",
- "repoRoot": "...",
- "sourceTarget": {
- "type": "plan",
- "value": ".claude/plan/workflow-visual-proof.json"
- }
- },
- "workers": [
- {
- "id": "seed-check",
- "label": "seed-check",
- "state": "running",
- "branch": "...",
- "worktree": "...",
- "runtime": {
- "kind": "tmux-pane",
- "command": "codex",
- "pid": 1234,
- "active": false,
- "dead": false
- },
- "intent": {
- "objective": "...",
- "seedPaths": ["scripts/orchestrate-worktrees.js"]
- },
- "outputs": {
- "summary": [],
- "validation": [],
- "remainingRisks": []
- },
- "artifacts": {
- "statusFile": "...",
- "taskFile": "...",
- "handoffFile": "..."
- }
- }
- ],
- "aggregates": {
- "workerCount": 2,
- "states": {
- "running": 1,
- "completed": 1
- }
- }
-}
-```
-
-This preserves the useful signal already present while removing tmux-specific
-details from the control-plane contract.
-
-## First Adapters To Support
-
-### 1. `dmux-tmux`
-
-Wrap the logic already living in
-`scripts/lib/orchestration-session.js`.
-
-This is the easiest first adapter because the substrate is already real.
-
-### 2. `claude-history`
-
-Normalize the data that
-`commands/sessions.md`
-and the existing session-manager utilities already expose:
-
-- session id / alias
-- branch
-- worktree
-- project path
-- recency / file size / item counts
-
-This provides a non-orchestrated baseline for ECC 2.0.
-
-### 3. `codex-worktree`
-
-Use the same canonical shape, but back it with Codex-native execution metadata
-instead of tmux assumptions where available.
-
-### 4. `opencode`
-
-Use the same adapter boundary once OpenCode session metadata is stable enough to
-normalize.
-
-## What Should Stay Out Of The Adapter Layer
-
-The adapter layer should not own:
-
-- business logic for merge sequencing
-- operator UI layout
-- pricing or monetization decisions
-- install profile selection
-- tmux lifecycle orchestration itself
-
-Its job is narrower:
-
-- detect session targets
-- load normalized snapshots
-- optionally stream runtime events
-- optionally expose safe actions
-
-## Current File Layout
-
-The adapter layer now lives in:
-
-```text
-scripts/lib/session-adapters/
- canonical-session.js
- dmux-tmux.js
- claude-history.js
- registry.js
-scripts/session-inspect.js
-tests/lib/session-adapters.test.js
-tests/scripts/session-inspect.test.js
-```
-
-The current orchestration snapshot parser is now being consumed as an adapter
-implementation rather than remaining the only product contract.
-
-## Immediate Next Steps
-
-1. Add a third adapter, likely `codex-worktree`, so the abstraction moves
- beyond tmux plus Claude-history.
-2. Decide whether canonical snapshots need separate `state` and `health`
- fields before UI work starts.
-3. Decide whether event streaming belongs in v1 or stays out until after the
- snapshot layer proves itself.
-4. Build operator-facing panels only on top of the adapter registry, not by
- reading orchestration internals directly.
-
-## Open Questions
-
-1. Should worker identity be keyed by worker slug, branch, or stable UUID?
-2. Do we need separate `state` and `health` fields at the canonical layer?
-3. Should event streaming be part of v1, or should ECC 2.0 ship snapshot-only
- first?
-4. How much path information should be redacted before snapshots leave the local
- machine?
-5. Should the adapter registry live inside this repo long-term, or move into the
- eventual ECC 2.0 control-plane app once the interface stabilizes?
-
-## Recommendation
-
-Treat the current tmux/worktree implementation as adapter `0`, not as the final
-product surface.
-
-The shortest path to ECC 2.0 is:
-
-1. preserve the current orchestration substrate
-2. wrap it in a canonical session adapter contract
-3. add one non-tmux adapter
-4. only then start building operator panels on top
diff --git a/docs/HERMES-OPENCLAW-MIGRATION.md b/docs/HERMES-OPENCLAW-MIGRATION.md
index 8391398c8..4984a9cbd 100644
--- a/docs/HERMES-OPENCLAW-MIGRATION.md
+++ b/docs/HERMES-OPENCLAW-MIGRATION.md
@@ -46,7 +46,7 @@ That means the shortest safe path is:
Use the current workspace split consistently:
- live code work happens in cloned repos under `~/GitHub`
-- repo-specific active execution context lives in repo-level `WORKING-CONTEXT.md`
+- repo-specific direction lives in the repo's planning docs under `docs/`, shipped change history in `CHANGELOG.md`
- broader non-code context can live in KB/archive layers
- durable cross-machine truth should prefer GitHub, Linear, and the knowledge base
@@ -105,7 +105,7 @@ Source examples:
Translate into:
- `knowledge-ops`
-- repo `WORKING-CONTEXT.md`
+- repo planning docs under `docs/` and `CHANGELOG.md`
- GitHub / Linear / KB-backed durable context
- future deep memory work under `#1049`
diff --git a/docs/MEGA-PLAN-REPO-PROMPTS-2026-03-12.md b/docs/MEGA-PLAN-REPO-PROMPTS-2026-03-12.md
deleted file mode 100644
index 4830deb5c..000000000
--- a/docs/MEGA-PLAN-REPO-PROMPTS-2026-03-12.md
+++ /dev/null
@@ -1,286 +0,0 @@
-# Mega Plan Repo Prompt List — March 12, 2026
-
-## Purpose
-
-Use these prompts to split the remaining March 11 mega-plan work by repo.
-They are written for parallel agents and assume the March 12 orchestration and
-Windows CI lane is already merged via `#417`.
-
-## Current Snapshot
-
-- `everything-claude-code` has finished the orchestration, Codex baseline, and
- Windows CI recovery lane.
-- The next open ECC Phase 1 items are:
- - review `#399`
- - convert recurring discussion pressure into tracked issues
- - define selective-install architecture
- - write the ECC 2.0 discovery doc
-- `agentshield`, `ECC-website`, and `skill-creator-app` all have dirty
- `main` worktrees and should not be edited directly on `main`.
-- `applications/` is not a standalone git repo. It lives inside the parent
- workspace repo at ``.
-
-## Repo: `everything-claude-code`
-
-### Prompt A — PR `#399` Review and Merge Readiness
-
-```text
-Work in: /everything-claude-code
-
-Goal:
-Review PR #399 ("fix(observe): 5-layer automated session guard to prevent
-self-loop observations") against the actual loop problem described in issue
-#398 and the March 11 mega plan. Do not assume the old failing CI on the PR is
-still meaningful, because the Windows baseline was repaired later in #417.
-
-Tasks:
-1. Read issue #398 and PR #399 in full.
-2. Inspect the observe hook implementation and tests locally.
-3. Determine whether the PR really prevents observer self-observation,
- automated-session observation, and runaway recursive loops.
-4. Identify any missing env-based bypass, idle gating, or session exclusion
- behavior.
-5. Produce a merge recommendation with findings ordered by severity.
-
-Constraints:
-- Do not merge automatically.
-- Do not rewrite unrelated hook behavior.
-- If you make code changes, keep them tightly scoped to observe behavior and
- tests.
-
-Deliverables:
-- review summary
-- exact findings with file references
-- recommended merge / rework decision
-- test commands run
-```
-
-### Prompt B — Roadmap Issues Extraction
-
-```text
-Work in: /everything-claude-code
-
-Goal:
-Convert recurring discussion pressure from the mega plan into concrete GitHub
-issues. Focus on high-signal roadmap items that unblock ECC 1.x and ECC 2.0.
-
-Create issue drafts or a ready-to-post issue bundle for:
-1. selective install profiles
-2. uninstall / doctor / repair lifecycle
-3. generated skill placement and provenance policy
-4. governance past the tool call
-5. ECC 2.0 discovery doc / adapter contracts
-
-Tasks:
-1. Read the March 11 mega plan and March 12 handoff.
-2. Deduplicate against already-open issues.
-3. Draft issue titles, problem statements, scope, non-goals, acceptance
- criteria, and file/system areas affected.
-
-Constraints:
-- Do not create filler issues.
-- Prefer 4-6 high-value issues over a large backlog dump.
-- Keep each issue scoped so it could plausibly land in one focused PR series.
-
-Deliverables:
-- issue shortlist
-- ready-to-post issue bodies
-- duplication notes against existing issues
-```
-
-### Prompt C — ECC 2.0 Discovery and Adapter Spec
-
-```text
-Work in: /everything-claude-code
-
-Goal:
-Turn the existing ECC 2.0 vision into a first concrete discovery doc focused on
-adapter contracts, session/task state, token accounting, and security/policy
-events.
-
-Tasks:
-1. Use the current orchestration/session snapshot code as the baseline.
-2. Define a normalized adapter contract for Claude Code, Codex, OpenCode, and
- later Cursor / GitHub App integration.
-3. Define the initial SQLite-backed data model for sessions, tasks, worktrees,
- events, findings, and approvals.
-4. Define what stays in ECC 1.x versus what belongs in ECC 2.0.
-5. Call out unresolved product decisions separately from implementation
- requirements.
-
-Constraints:
-- Treat the current tmux/worktree/session snapshot substrate as the starting
- point, not a blank slate.
-- Keep the doc implementation-oriented.
-
-Deliverables:
-- discovery doc
-- adapter contract sketch
-- event model sketch
-- unresolved questions list
-```
-
-## Repo: `agentshield`
-
-### Prompt — False Positive Audit and Regression Plan
-
-```text
-Work in: /agentshield
-
-Goal:
-Advance the AgentShield Phase 2 workstream from the mega plan: reduce false
-positives, especially where declarative deny rules, block hooks, docs examples,
-or config snippets are misclassified as executable risk.
-
-Important repo state:
-- branch is currently main
-- dirty files exist in CLAUDE.md and README.md
-- classify or park existing edits before broader changes
-
-Tasks:
-1. Inspect the current false-positive behavior around:
- - .claude hook configs
- - AGENTS.md / CLAUDE.md
- - .cursor rules
- - .opencode plugin configs
- - sample deny-list patterns
-2. Separate parser behavior for declarative patterns vs executable commands.
-3. Propose regression coverage additions and the exact fixture set needed.
-4. If safe after branch setup, implement the first pass of the classifier fix.
-
-Constraints:
-- do not work directly on dirty main
-- keep fixes parser/classifier-scoped
-- document any remaining ambiguity explicitly
-
-Deliverables:
-- branch recommendation
-- false-positive taxonomy
-- proposed or landed regression tests
-- remaining edge cases
-```
-
-## Repo: `ECC-website`
-
-### Prompt — Landing Rewrite and Product Framing
-
-```text
-Work in: /ECC-website
-
-Goal:
-Execute the website lane from the mega plan by rewriting the landing/product
-framing away from "config repo" and toward "open agent harness system" plus
-future control-plane direction.
-
-Important repo state:
-- branch is currently main
-- dirty files exist in favicon assets and multiple page/component files
-- branch before meaningful work and preserve existing edits unless explicitly
- classified as stale
-
-Tasks:
-1. Classify the dirty main worktree state.
-2. Rewrite the landing page narrative around:
- - open agent harness system
- - runtime guardrails
- - cross-harness parity
- - operator visibility and security
-3. Define or update the next key pages:
- - /skills
- - /security
- - /platforms
- - /system or /dashboard
-4. Keep the page visually intentional and product-forward, not generic SaaS.
-
-Constraints:
-- do not silently overwrite existing dirty work
-- preserve existing design system where it is coherent
-- distinguish ECC 1.x toolkit from ECC 2.0 control plane clearly
-
-Deliverables:
-- branch recommendation
-- landing-page rewrite diff or content spec
-- follow-up page map
-- deployment readiness notes
-```
-
-## Repo: `skill-creator-app`
-
-### Prompt — Skill Import Pipeline and Product Fit
-
-```text
-Work in: /skill-creator-app
-
-Goal:
-Align skill-creator-app with the mega-plan external skill sourcing and audited
-import pipeline workstream.
-
-Important repo state:
-- branch is currently main
-- dirty files exist in README.md and src/lib/github.ts
-- classify or park existing changes before broader work
-
-Tasks:
-1. Assess whether the app should support:
- - inventorying external skills
- - provenance tagging
- - dependency/risk audit fields
- - ECC convention adaptation workflows
-2. Review the existing GitHub integration surface in src/lib/github.ts.
-3. Produce a concrete product/technical scope for an audited import pipeline.
-4. If safe after branching, land the smallest enabling changes for metadata
- capture or GitHub ingestion.
-
-Constraints:
-- do not turn this into a generic prompt-builder
-- keep the focus on audited skill ingestion and ECC-compatible output
-
-Deliverables:
-- product-fit summary
-- recommended scope for v1
-- data fields / workflow steps for the import pipeline
-- code changes if they are small and clearly justified
-```
-
-## Repo: `ECC` Workspace (`applications/`, `knowledge/`, `tasks/`)
-
-### Prompt — Example Apps and Workflow Reliability Proofs
-
-```text
-Work in:
-
-Goal:
-Use the parent ECC workspace to support the mega-plan hosted/workflow lanes.
-This is not a standalone applications repo; it is the umbrella workspace that
-contains applications/, knowledge/, tasks/, and related planning assets.
-
-Tasks:
-1. Inventory what in applications/ is real product code vs placeholder.
-2. Identify where example repos or demo apps should live for:
- - GitHub App workflow proofs
- - ECC 2.0 prototype spikes
- - example install / setup reliability checks
-3. Propose a clean workspace structure so product code, research, and planning
- stop bleeding into each other.
-4. Recommend which proof-of-concept should be built first.
-
-Constraints:
-- do not move large directories blindly
-- distinguish repo structure recommendations from immediate code changes
-- keep recommendations compatible with the current multi-repo ECC setup
-
-Deliverables:
-- workspace inventory
-- proposed structure
-- first demo/app recommendation
-- follow-up branch/worktree plan
-```
-
-## Local Continuation
-
-The current worktree should stay on ECC-native Phase 1 work that does not touch
-the existing dirty skill-file changes here. The best next local tasks are:
-
-1. selective-install architecture
-2. ECC 2.0 discovery doc
-3. PR `#399` review
diff --git a/docs/PHASE1-ISSUE-BUNDLE-2026-03-12.md b/docs/PHASE1-ISSUE-BUNDLE-2026-03-12.md
deleted file mode 100644
index d1594a3af..000000000
--- a/docs/PHASE1-ISSUE-BUNDLE-2026-03-12.md
+++ /dev/null
@@ -1,272 +0,0 @@
-# Phase 1 Issue Bundle — March 12, 2026
-
-## Status
-
-These issue drafts were prepared from the March 11 mega plan plus the March 12
-handoff. I attempted to open them directly in GitHub, but issue creation was
-blocked by missing GitHub authentication in the MCP session.
-
-## GitHub Status
-
-These drafts were later posted via `gh`:
-
-- `#423` Implement manifest-driven selective install profiles for ECC
-- `#421` Add ECC install-state plus uninstall / doctor / repair lifecycle
-- `#424` Define canonical session adapter contract for ECC 2.0 control plane
-- `#422` Define generated skill placement and provenance policy
-- `#425` Define governance and visibility past the tool call
-
-The bodies below are preserved as the local source bundle used to create the
-issues.
-
-## Issue 1
-
-### Title
-
-Implement manifest-driven selective install profiles for ECC
-
-### Labels
-
-- `enhancement`
-
-### Body
-
-```md
-## Problem
-
-ECC still installs primarily by target and language. The repo now has first-pass
-selective-install manifests and a non-mutating plan resolver, but the installer
-itself does not yet consume those profiles.
-
-Current groundwork already landed in-repo:
-
-- `manifests/install-modules.json`
-- `manifests/install-profiles.json`
-- `scripts/ci/validate-install-manifests.js`
-- `scripts/lib/install-manifests.js`
-- `scripts/install-plan.js`
-
-That means the missing step is no longer design discovery. The missing step is
-execution: wire profile/module resolution into the actual install flow while
-preserving backward compatibility.
-
-## Scope
-
-Implement manifest-driven install execution for current ECC targets:
-
-- `claude`
-- `cursor`
-- `antigravity`
-
-Add first-pass support for:
-
-- `ecc-install --profile `
-- `ecc-install --modules `
-- target-aware filtering based on module target support
-- backward-compatible legacy language installs during rollout
-
-## Non-Goals
-
-- Full uninstall/doctor/repair lifecycle in the same issue
-- Codex/OpenCode install targets in the first pass if that blocks rollout
-- Reorganizing the repository into separate published packages
-
-## Acceptance Criteria
-
-- `install.sh` can resolve and install a named profile
-- `install.sh` can resolve explicit module IDs
-- Unsupported modules for a target are skipped or rejected deterministically
-- Legacy language-based install mode still works
-- Tests cover profile resolution and installer behavior
-- Docs explain the new preferred profile/module install path
-```
-
-## Issue 2
-
-### Title
-
-Add ECC install-state plus uninstall / doctor / repair lifecycle
-
-### Labels
-
-- `enhancement`
-
-### Body
-
-```md
-## Problem
-
-ECC has no canonical installed-state record. That makes uninstall, repair, and
-post-install inspection nondeterministic.
-
-Today the repo can classify installable content, but it still cannot reliably
-answer:
-
-- what profile/modules were installed
-- what target they were installed into
-- what paths ECC owns
-- how to remove or repair only ECC-managed files
-
-Without install-state, lifecycle commands are guesswork.
-
-## Scope
-
-Introduce a durable install-state contract and the first lifecycle commands:
-
-- `ecc list-installed`
-- `ecc uninstall`
-- `ecc doctor`
-- `ecc repair`
-
-Suggested state locations:
-
-- Claude: `~/.claude/ecc/install-state.json`
-- Cursor: `./.cursor/ecc-install-state.json`
-- Antigravity: `./.agent/ecc-install-state.json`
-
-The state file should capture at minimum:
-
-- installed version
-- timestamp
-- target
-- profile
-- resolved modules
-- copied/managed paths
-- source repo version or package version
-
-## Non-Goals
-
-- Rebuilding the installer architecture from scratch
-- Full remote/cloud control-plane functionality
-- Target support expansion beyond the current local installers unless it falls
- out naturally
-
-## Acceptance Criteria
-
-- Successful installs write install-state deterministically
-- `list-installed` reports target/profile/modules/version cleanly
-- `doctor` reports missing or drifted managed paths
-- `repair` restores missing managed files from recorded install-state
-- `uninstall` removes only ECC-managed files and leaves unrelated local files
- alone
-- Tests cover install-state creation and lifecycle behavior
-```
-
-## Issue 3
-
-### Title
-
-Define canonical session adapter contract for ECC 2.0 control plane
-
-### Labels
-
-- `enhancement`
-
-### Body
-
-```md
-## Problem
-
-ECC now has real orchestration/session substrate, but it is still
-implementation-specific.
-
-Current state:
-
-- tmux/worktree orchestration exists
-- machine-readable session snapshots exist
-- Claude local session-history commands exist
-
-What does not exist yet is a harness-neutral adapter boundary that can normalize
-session/task state across:
-
-- tmux-orchestrated workers
-- plain Claude sessions
-- Codex worktrees
-- OpenCode sessions
-- later remote or GitHub-integrated operator surfaces
-
-Without that adapter contract, any future ECC 2.0 operator shell will be forced
-to read tmux-specific and markdown-coordination details directly.
-
-## Scope
-
-Define and implement the first-pass canonical session adapter layer.
-
-Suggested deliverables:
-
-- adapter registry
-- canonical session snapshot schema
-- `dmux-tmux` adapter backed by current orchestration code
-- `claude-history` adapter backed by current session history utilities
-- read-only inspection CLI for canonical session snapshots
-
-## Non-Goals
-
-- Full ECC 2.0 UI in the same issue
-- Monetization/GitHub App implementation
-- Remote multi-user control plane
-
-## Acceptance Criteria
-
-- There is a documented canonical snapshot contract
-- Current tmux orchestration snapshot code is wrapped as an adapter rather than
- the top-level product contract
-- A second non-tmux adapter exists to prove the abstraction is real
-- Tests cover adapter selection and normalized snapshot output
-- The design clearly separates adapter concerns from orchestration and UI
- concerns
-```
-
-## Issue 4
-
-### Title
-
-Define generated skill placement and provenance policy
-
-### Labels
-
-- `enhancement`
-
-### Body
-
-```md
-## Problem
-
-ECC now has a large and growing skill surface, but generated/imported/learned
-skills do not yet have a clear long-term placement and provenance policy.
-
-This creates several problems:
-
-- unclear separation between curated skills and generated/learned skills
-- validator noise around directories that may or may not exist locally
-- weak provenance for imported or machine-generated skill content
-- uncertainty about where future automated learning outputs should live
-
-As ECC grows, the repo needs explicit rules for where generated skill artifacts
-belong and how they are identified.
-
-## Scope
-
-Define a repo-wide policy for:
-
-- curated vs generated vs imported skill placement
-- provenance metadata requirements
-- validator behavior for optional/generated skill directories
-- whether generated skills are shipped, ignored, or materialized during
- install/build steps
-
-## Non-Goals
-
-- Building a full external skill marketplace
-- Rewriting all existing skill content in one pass
-- Solving every content-quality issue in the same issue
-
-## Acceptance Criteria
-
-- A documented placement policy exists for generated/imported skills
-- Provenance requirements are explicit
-- Validators no longer produce ambiguous behavior around optional/generated
- skill locations
-- The policy clearly states what is publishable vs local-only
-- Follow-on implementation work is split into concrete, bounded PR-sized steps
-```
diff --git a/docs/PR-399-REVIEW-2026-03-12.md b/docs/PR-399-REVIEW-2026-03-12.md
deleted file mode 100644
index 98a2ef238..000000000
--- a/docs/PR-399-REVIEW-2026-03-12.md
+++ /dev/null
@@ -1,59 +0,0 @@
-# PR 399 Review — March 12, 2026
-
-## Scope
-
-Reviewed `#399`:
-
-- title: `fix(observe): 5-layer automated session guard to prevent self-loop observations`
-- head: `e7df0e588ceecfcd1072ef616034ccd33bb0f251`
-- files changed:
- - `skills/continuous-learning-v2/hooks/observe.sh`
- - `skills/continuous-learning-v2/agents/observer-loop.sh`
-
-## Findings
-
-### Medium
-
-1. `skills/continuous-learning-v2/hooks/observe.sh`
-
-The new `CLAUDE_CODE_ENTRYPOINT` guard uses a finite allowlist of known
-non-`cli` values (`sdk-ts`, `sdk-py`, `sdk-cli`, `mcp`, `remote`).
-
-That leaves a forward-compatibility hole: any future non-`cli` entrypoint value
-will fall through and be treated as interactive. That reintroduces the exact
-class of automated-session observation the PR is trying to prevent.
-
-The safer rule is:
-
-- allow only `cli`
-- treat every other explicit entrypoint as automated
-- keep the default fallback as `cli` when the variable is unset
-
-Suggested shape:
-
-```bash
-case "${CLAUDE_CODE_ENTRYPOINT:-cli}" in
- cli) ;;
- *) exit 0 ;;
-esac
-```
-
-## Merge Recommendation
-
-`Needs one follow-up change before merge.`
-
-The PR direction is correct:
-
-- it closes the ECC self-observation loop in `observer-loop.sh`
-- it adds multiple guard layers in the right area of `observe.sh`
-- it already addressed the cheaper-first ordering and skip-path trimming issues
-
-But the entrypoint guard should be generalized before merge so the automation
-filter does not silently age out when Claude Code introduces additional
-non-interactive entrypoints.
-
-## Residual Risk
-
-- There is still no dedicated regression test coverage around the new shell
- guard behavior, so the final merge should include at least one executable
- verification pass for the entrypoint and skip-path cases.
diff --git a/docs/PR-QUEUE-TRIAGE-2026-03-13.md b/docs/PR-QUEUE-TRIAGE-2026-03-13.md
deleted file mode 100644
index 892ff579f..000000000
--- a/docs/PR-QUEUE-TRIAGE-2026-03-13.md
+++ /dev/null
@@ -1,355 +0,0 @@
-# PR Review And Queue Triage — March 13, 2026
-
-## Snapshot
-
-This document records a live GitHub triage snapshot for the
-`everything-claude-code` pull-request queue as of `2026-03-13T08:33:31Z`.
-
-Sources used:
-
-- `gh pr view`
-- `gh pr checks`
-- `gh pr diff --name-only`
-- targeted local verification against the merged `#399` head
-
-Stale threshold used for this pass:
-
-- `last updated before 2026-02-11` (`>30` days before March 13, 2026)
-
-## PR `#399` Retrospective Review
-
-PR:
-
-- `#399` — `fix(observe): 5-layer automated session guard to prevent self-loop observations`
-- state: `MERGED`
-- merged at: `2026-03-13T06:40:03Z`
-- merge commit: `c52a28ace9e7e84c00309fc7b629955dfc46ecf9`
-
-Files changed:
-
-- `skills/continuous-learning-v2/hooks/observe.sh`
-- `skills/continuous-learning-v2/agents/observer-loop.sh`
-
-Validation performed against merged head `546628182200c16cc222b97673ddd79e942eacce`:
-
-- `bash -n` on both changed shell scripts
-- `node tests/hooks/hooks.test.js` (`204` passed, `0` failed)
-- targeted hook invocations for:
- - interactive CLI session
- - `CLAUDE_CODE_ENTRYPOINT=mcp`
- - `ECC_HOOK_PROFILE=minimal`
- - `ECC_SKIP_OBSERVE=1`
- - `agent_id` payload
- - trimmed `ECC_OBSERVE_SKIP_PATHS`
-
-Behavioral result:
-
-- the core self-loop fix works
-- automated-session guard branches suppress observation writes as intended
-- the final `non-cli => exit` entrypoint logic is the correct fail-closed shape
-
-Remaining findings:
-
-1. Medium: skipped automated sessions still create homunculus project state
- before the new guards exit.
- `observe.sh` resolves `cwd` and sources project detection before reaching the
- automated-session guard block, so `detect-project.sh` still creates
- `projects//...` directories and updates `projects.json` for sessions that
- later exit early.
-2. Low: the new guard matrix shipped without direct regression coverage.
- The hook test suite still validates adjacent behavior, but it does not
- directly assert the new `CLAUDE_CODE_ENTRYPOINT`, `ECC_HOOK_PROFILE`,
- `ECC_SKIP_OBSERVE`, `agent_id`, or trimmed skip-path branches.
-
-Verdict:
-
-- `#399` is technically correct for its primary goal and was safe to merge as
- the urgent loop-stop fix.
-- It still warrants a follow-up issue or patch to move automated-session guards
- ahead of project-registration side effects and to add explicit guard-path
- tests.
-
-## Open PR Inventory
-
-There are currently `4` open PRs.
-
-### Queue Table
-
-| PR | Title | Draft | Mergeable | Merge State | Updated | Stale | Current Verdict |
-| --- | --- | --- | --- | --- | --- | --- | --- |
-| `#292` | `chore(config): governance and config foundation (PR #272 split 1/6)` | `false` | `MERGEABLE` | `UNSTABLE` | `2026-03-13T07:26:55Z` | `No` | `Best current merge candidate` |
-| `#298` | `feat(agents,skills,rules): add Rust, Java, mobile, DevOps, and performance content` | `false` | `CONFLICTING` | `DIRTY` | `2026-03-11T04:29:07Z` | `No` | `Needs changes before review can finish` |
-| `#336` | `Customisation for Codex CLI - Features from Claude Code and OpenCode` | `true` | `MERGEABLE` | `UNSTABLE` | `2026-03-13T07:26:12Z` | `No` | `Needs manual review and draft exit` |
-| `#420` | `feat: add laravel skills` | `true` | `MERGEABLE` | `UNSTABLE` | `2026-03-12T22:57:36Z` | `No` | `Low-risk draft, review after draft exit` |
-
-No currently open PR is stale by the `>30 days since last update` rule.
-
-## Per-PR Assessment
-
-### `#292` — Governance / Config Foundation
-
-Live state:
-
-- open
-- non-draft
-- `MERGEABLE`
-- merge state `UNSTABLE`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
-
-Scope:
-
-- `.env.example`
-- `.github/ISSUE_TEMPLATE/copilot-task.md`
-- `.github/PULL_REQUEST_TEMPLATE.md`
-- `.gitignore`
-- `.markdownlint.json`
-- `.tool-versions`
-- `VERSION`
-
-Assessment:
-
-- This is the cleanest merge candidate in the current queue.
-- The branch was already refreshed onto current `main`.
-- The currently visible bot feedback is minor/nit-level rather than obviously
- merge-blocking.
-- The main caution is that only external bot checks are visible right now; no
- GitHub Actions matrix run appears in the current PR checks output.
-
-Current recommendation:
-
-- `Mergeable after one final owner pass.`
-- If you want a conservative path, do one quick human review of the remaining
- `.env.example`, PR-template, and `.tool-versions` nitpicks before merge.
-
-### `#298` — Large Multi-Domain Content Expansion
-
-Live state:
-
-- open
-- non-draft
-- `CONFLICTING`
-- merge state `DIRTY`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
- - `cubic · AI code reviewer` passed
-
-Scope:
-
-- `35` files
-- large documentation and skill/rule expansion across Java, Rust, mobile,
- DevOps, performance, data, and MLOps
-
-Assessment:
-
-- This PR is not ready for merge.
-- It conflicts with current `main`, so it is not even mergeable at the branch
- level yet.
-- cubic identified `34` issues across `35` files in the current review.
- Those findings are substantive and technical, not just style cleanup, and
- they cover broken or misleading examples across several new skills.
-- Even without the conflict, the scope is large enough that it needs a deliberate
- content-fix pass rather than a quick merge decision.
-
-Current recommendation:
-
-- `Needs changes.`
-- Rebase or restack first, then resolve the substantive example-quality issues.
-- If momentum matters, split by domain rather than carrying one very large PR.
-
-### `#336` — Codex CLI Customization
-
-Live state:
-
-- open
-- draft
-- `MERGEABLE`
-- merge state `UNSTABLE`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
-
-Scope:
-
-- `scripts/codex-git-hooks/pre-commit`
-- `scripts/codex-git-hooks/pre-push`
-- `scripts/codex/check-codex-global-state.sh`
-- `scripts/codex/install-global-git-hooks.sh`
-- `scripts/sync-ecc-to-codex.sh`
-
-Assessment:
-
-- This PR is no longer conflicting, but it is still draft-only and has not had
- a meaningful first-party review pass.
-- It modifies user-global Codex setup behavior and git-hook installation, so the
- operational blast radius is higher than a docs-only PR.
-- The visible checks are only external bots; there is no full GitHub Actions run
- shown in the current check set.
-- Because the branch comes from a contributor fork `main`, it also deserves an
- extra sanity pass on what exactly is being proposed before changing status.
-
-Current recommendation:
-
-- `Needs changes before merge readiness`, where the required changes are process
- and review oriented rather than an already-proven code defect:
- - finish manual review
- - run or confirm validation on the global-state scripts
- - take it out of draft only after that review is complete
-
-### `#420` — Laravel Skills
-
-Live state:
-
-- open
-- draft
-- `MERGEABLE`
-- merge state `UNSTABLE`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
-
-Scope:
-
-- `README.md`
-- `examples/laravel-api-CLAUDE.md`
-- `rules/php/patterns.md`
-- `rules/php/security.md`
-- `rules/php/testing.md`
-- `skills/configure-ecc/SKILL.md`
-- `skills/laravel-patterns/SKILL.md`
-- `skills/laravel-security/SKILL.md`
-- `skills/laravel-tdd/SKILL.md`
-- `skills/laravel-verification/SKILL.md`
-
-Assessment:
-
-- This is content-heavy and operationally lower risk than `#336`.
-- It is still draft and has not had a substantive human review pass yet.
-- The visible checks are external bots only.
-- Nothing in the live PR state suggests a merge blocker yet, but it is not ready
- to be merged simply because it is still draft and under-reviewed.
-
-Current recommendation:
-
-- `Review next after the highest-priority non-draft work.`
-- Likely a good review candidate once the author is ready to exit draft.
-
-## Mergeability Buckets
-
-### Mergeable Now Or After A Final Owner Pass
-
-- `#292`
-
-### Needs Changes Before Merge
-
-- `#298`
-- `#336`
-
-### Draft / Needs Review Before Any Merge Decision
-
-- `#420`
-
-### Stale `>30 Days`
-
-- none
-
-## Recommended Order
-
-1. `#292`
- This is the cleanest live merge candidate.
-2. `#420`
- Low runtime risk, but wait for draft exit and a real review pass.
-3. `#336`
- Review carefully because it changes global Codex sync and hook behavior.
-4. `#298`
- Rebase and fix the substantive content issues before spending more review time
- on it.
-
-## Bottom Line
-
-- `#399`: safe bugfix merge with one follow-up cleanup still warranted
-- `#292`: highest-priority merge candidate in the current open queue
-- `#298`: not mergeable; conflicts plus substantive content defects
-- `#336`: no longer conflicting, but not ready while still draft and lightly
- validated
-- `#420`: draft, low-risk content lane, review after the non-draft queue
-
-## Live Refresh
-
-Refreshed at `2026-03-13T22:11:40Z`.
-
-### Main Branch
-
-- `origin/main` is green right now, including the Windows test matrix.
-- Mainline CI repair is not the current bottleneck.
-
-### Updated Queue Read
-
-#### `#292` — Governance / Config Foundation
-
-- open
-- non-draft
-- `MERGEABLE`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
-- highest-signal remaining work is not CI repair; it is the small correctness
- pass on `.env.example` and PR-template alignment before merge
-
-Current recommendation:
-
-- `Next actionable PR.`
-- Either patch the remaining doc/config correctness issues, or do one final
- owner pass and merge if you accept the current tradeoffs.
-
-#### `#420` — Laravel Skills
-
-- open
-- draft
-- `MERGEABLE`
-- visible checks:
- - `CodeRabbit` skipped because the PR is draft
- - `GitGuardian Security Checks` passed
-- no substantive human review is visible yet
-
-Current recommendation:
-
-- `Review after the non-draft queue.`
-- Low implementation risk, but not merge-ready while still draft and
- under-reviewed.
-
-#### `#336` — Codex CLI Customization
-
-- open
-- draft
-- `MERGEABLE`
-- visible checks:
- - `CodeRabbit` passed
- - `GitGuardian Security Checks` passed
-- still needs a deliberate manual review because it touches global Codex sync
- and git-hook installation behavior
-
-Current recommendation:
-
-- `Manual-review lane, not immediate merge lane.`
-
-#### `#298` — Large Content Expansion
-
-- open
-- non-draft
-- `CONFLICTING`
-- still the hardest remaining PR in the queue
-
-Current recommendation:
-
-- `Last priority among current open PRs.`
-- Rebase first, then handle the substantive content/example corrections.
-
-### Current Order
-
-1. `#292`
-2. `#420`
-3. `#336`
-4. `#298`
diff --git a/docs/ROADMAP.md b/docs/ROADMAP.md
new file mode 100644
index 000000000..38c18e1a6
--- /dev/null
+++ b/docs/ROADMAP.md
@@ -0,0 +1,152 @@
+# ECC Roadmap
+
+Status: maintainer planning draft, updated 2026-09-09 against the integrated
+source candidate based on release 2.2.1. Source inclusion is not a release or live
+verification claim. Dates are targets, not commitments; bracketed numbers remain
+planning choices.
+
+The two older planning docs stay as evidence and history:
+`docs/ECC-2.0-GA-ROADMAP.md` (2.0 milestones and control-plane deltas) and
+`docs/ECC-PRO-SECURITY-ROADMAP.md` (AgentShield and Pro conversion). This file
+is the short, current view.
+
+## Vision
+
+ECC is the operating layer between a developer and whatever coding agent they
+run. Shared skills, rules, and agent guidance provide portable core workflows
+across Claude Code, Codex, OpenCode, Cursor, Gemini, and other harnesses.
+Hooks, installation paths, and feature coverage vary by host; consult the
+[support status matrix](../README.md#platform-support) for current limits.
+The bar for everything that ships: simpler to read, faster to run, and
+traceable after the fact, for agents and humans alike.
+
+Three things follow from that.
+
+1. **The repo is the product.** Curated skills, hooks, and rules are the
+ surface people install. Anything that is not installed, tested, or read by
+ someone should not be in the tree.
+2. **Evidence over assertion.** A harness change earns trust through a gate
+ receipt, a capsule, and a reproducible verdict, not through a paragraph
+ saying it works. The offline eval framework provides the recording and review primitives;
+ isolated candidate execution remains future work.
+3. **Operator patterns travel.** Approval loops, channel discipline,
+ agreement generation, and e-sign placement were built for one desk. As
+ generic skills they are useful to anyone running agents next to
+ counterparties, customers, or money.
+
+## Where we are
+
+- The 2.2.1 source baseline includes guided manifest-driven setup, install-state
+ ownership, repair and uninstall. Its release workflow requires exact-head
+ validation; this roadmap is not release-signature evidence.
+- Catalog in this source snapshot: 68 agents, 289 skills, 94 legacy commands. The
+ count is a liability as much as an asset. Overlapping and unreferenced
+ skills exist.
+- The README now has one primary install section, with per-harness details
+ and release history linked to `CHANGELOG.md`. Further shortening is a target,
+ not a completed claim.
+- Eval source now includes capsule journals, replay matching and offline
+ receipt inspection, plus a protocol example. Candidate execution and staged
+ gate runs are disabled: no actual OS containment exists. Offline validation
+ and a receipt signature do not establish safe execution or promotion authority.
+- The README describes AgentShield scanning and the hosted ECC Pro surface.
+ Further conversion and scan-history improvements below are proposals, not
+ evidence of missing paid functionality or verified adoption.
+
+## Plan
+
+### Track A: condense
+
+Cut what nobody reads or installs. Merge what overlaps. One README that reads
+top to bottom in one pass. Exit criteria: no zero-reference tracked doc
+outside `docs/releases/`, no deprecated skill still shipped by default,
+README under [1,200] lines with one install path per harness.
+
+### Track B: evidence
+
+Implement and independently test an OS executor before enabling the gate:
+contain child processes, filesystem and network access, scrub inherited
+capabilities, enforce resource limits, and bind replay and result provenance.
+Keep execution disabled until those boundaries are proven. Then wire the
+`harness-optimizer` agent and `/harness-audit` to emit gate receipts. Add
+capsule recording to the hooks that already log session activity. Then the
+next two plan slices: offline retrospective grouping over capsules (no new
+rollouts) and forced-compaction tests that prove pinned constraints survive.
+
+### Track C: operator skills
+
+The four desk-pattern skills are present in this candidate: operator approval
+loop, counterparty channel discipline, master agreement drafting with bounded
+schedule append, and e-sign field placement guidance. Validate each with its
+actual consumer and collect outside feedback before adding more. Written send
+and audience contracts do not claim transport enforcement; generated agreements
+remain drafts and DOCX conversion does not establish execution readiness.
+
+### Track D: distribution and revenue
+
+Keep the release path boring: tag on main, CI green at the exact head, packed
+artifact tested on three platforms. Improve the AgentShield-to-Pro conversion path, evaluating hosted scan history
+and a PR-comment autofix loop against what the hosted product already supports. Details and
+scoring live in the security roadmap.
+
+## Next 90 days
+
+Window: 2026-09-02 to 2026-12-01.
+
+### September
+
+- Review and release the composed 2026-09-02 program: offline eval frameworks,
+ desk-pattern skills, condensation and this roadmap. The source candidate
+ incorporates them; merge and release remain separate maintainer decisions.
+- README linear pass merged. Release notes move to `CHANGELOG.md` only.
+- Delete list from the condensation survey executed, with catalog counts,
+ manifests, and locale mirrors updated in the same PR.
+- Decide the fate of `continuous-learning` v1 (deprecated since April): remove
+ in [2.3.0] with a migration note, or keep as an archive outside the default
+ install.
+
+### October
+
+- `harness-optimizer` and `/harness-audit` produce gate receipts. A skill,
+ hook, or agent change in this repo can cite a receipt in its PR.
+- Capsule recording behind an opt-in hook flag, journaling tool calls and
+ session boundaries with the default-deny payload allowlist.
+- First taskset beyond the example: [20 to 60] tasks over one real skill
+ family, with a held-out split and a reward-hack fixture.
+- Skill catalog review: every skill has a test, a command, an agent, or a
+ README mention, or it is marked for removal in [2.4.0].
+
+### November
+
+- 2.3.0: condensation, eval frameworks, and operator skills in one release
+ with the packed-artifact gate.
+- Retrospective grouping over recorded capsules for one task family, report
+ only, no promotion.
+- Forced-compaction invariance test in CI for the pinned-state pattern.
+- AgentShield Pro conversion CTA and hosted scan history behind a flag.
+
+### Decision points
+
+- 2026-09-30: is the README under the line target with no test regressions?
+ If not, cut scope on Track A rather than slipping the release.
+- 2026-10-31: does a real taskset produce a stable verdict across three runs?
+ If variance is high, hold Track B at receipts and do not start retrospective
+ grouping.
+- 2026-11-30: did any outside user adopt a desk-pattern skill? If none, stop
+ adding operator skills and fold the four into a single guide.
+
+## Not on this roadmap
+
+- Online reinforcement learning or weight updates from capsule data.
+- Production transparency-log witnessing, GPU attestation, or key management
+ inside the ECC package.
+- Automatic merge or release driven by a gate verdict. The gate stops changes.
+ A person promotes them.
+- Any desk, payment, provider, or counterparty integration. Those belong to
+ the systems that own them, not to a portable plugin.
+
+## How to edit this file
+
+Change the bracketed numbers first. Move items between months freely. When a
+line ships, delete it here and record it in `CHANGELOG.md`. Keep the file
+under [200] lines.
diff --git a/docs/SELECTIVE-INSTALL-DESIGN.md b/docs/SELECTIVE-INSTALL-DESIGN.md
deleted file mode 100644
index 817210ce8..000000000
--- a/docs/SELECTIVE-INSTALL-DESIGN.md
+++ /dev/null
@@ -1,489 +0,0 @@
-# ECC Selective Install Design
-
-## Purpose
-
-This document defines the user-facing selective-install design for ECC.
-
-It complements
-`docs/SELECTIVE-INSTALL-ARCHITECTURE.md`, which focuses on internal runtime
-architecture and code boundaries.
-
-This document answers the product and operator questions first:
-
-- how users choose ECC components
-- what the CLI should feel like
-- what config file should exist
-- how installation should behave across harness targets
-- how the design maps onto the current ECC codebase without requiring a rewrite
-
-## Problem
-
-Today ECC still feels like a large payload installer even though the repo now
-has first-pass manifest and lifecycle support.
-
-Users need a simpler mental model:
-
-- install the baseline
-- add the language packs they actually use
-- add the framework configs they actually want
-- add optional capability packs like security, research, or orchestration
-
-The selective-install system should make ECC feel composable instead of
-all-or-nothing.
-
-In the current substrate, user-facing components are still an alias layer over
-coarser internal install modules. That means include/exclude is already useful
-at the module-selection level, but some file-level boundaries remain imperfect
-until the underlying module graph is split more finely.
-
-## Goals
-
-1. Let users install a small default ECC footprint quickly.
-2. Let users compose installs from reusable component families:
- - core rules
- - language packs
- - framework packs
- - capability packs
- - target/platform configs
-3. Keep one consistent UX across Claude, Cursor, Antigravity, Codex, and
- OpenCode.
-4. Keep installs inspectable, repairable, and uninstallable.
-5. Preserve backward compatibility with the current `ecc-install typescript`
- style during rollout.
-
-## Non-Goals
-
-- packaging ECC into multiple npm packages in the first phase
-- building a remote marketplace
-- full control-plane UI in the same phase
-- solving every skill-classification problem before selective install ships
-
-## User Experience Principles
-
-### 1. Start Small
-
-A user should be able to get a useful ECC install with one command:
-
-```bash
-ecc install --target claude --profile core
-```
-
-The default experience should not assume the user wants every skill family and
-every framework.
-
-### 2. Build Up By Intent
-
-The user should think in terms of:
-
-- "I want the developer baseline"
-- "I need TypeScript and Python"
-- "I want Next.js and Django"
-- "I want the security pack"
-
-The user should not have to know raw internal repo paths.
-
-### 3. Preview Before Mutation
-
-Every install path should support dry-run planning:
-
-```bash
-ecc install --target cursor --profile developer --with lang:typescript --with framework:nextjs --dry-run
-```
-
-The plan should clearly show:
-
-- selected components
-- skipped components
-- target root
-- managed paths
-- expected install-state location
-
-### 4. Local Configuration Should Be First-Class
-
-Teams should be able to commit a project-level install config and use:
-
-```bash
-ecc install --config ecc-install.json
-```
-
-That allows deterministic installs across contributors and CI.
-
-## Component Model
-
-The current manifest already uses install modules and profiles. The user-facing
-design should keep that internal structure, but present it as four main
-component families.
-
-Near-term implementation note: some user-facing component IDs still resolve to
-shared internal modules, especially in the language/framework layer. The
-catalog improves UX immediately while preserving a clean path toward finer
-module granularity in later phases.
-
-### 1. Baseline
-
-These are the default ECC building blocks:
-
-- core rules
-- baseline agents
-- core commands
-- runtime hooks
-- platform configs
-- workflow quality primitives
-
-Examples of current internal modules:
-
-- `rules-core`
-- `agents-core`
-- `commands-core`
-- `hooks-runtime`
-- `platform-configs`
-- `workflow-quality`
-
-### 2. Language Packs
-
-Language packs group rules, guidance, and workflows for a language ecosystem.
-
-Examples:
-
-- `lang:typescript`
-- `lang:python`
-- `lang:go`
-- `lang:java`
-- `lang:rust`
-
-Each language pack should resolve to one or more internal modules plus
-target-specific assets.
-
-### 3. Framework Packs
-
-Framework packs sit above language packs and pull in framework-specific rules,
-skills, and optional setup.
-
-Examples:
-
-- `framework:react`
-- `framework:nextjs`
-- `framework:django`
-- `framework:springboot`
-- `framework:laravel`
-
-Framework packs should depend on the correct language pack or baseline
-primitives where appropriate.
-
-### 4. Capability Packs
-
-Capability packs are cross-cutting ECC feature bundles.
-
-Examples:
-
-- `capability:security`
-- `capability:research`
-- `capability:orchestration`
-- `capability:media`
-- `capability:content`
-
-These should map onto the current module families already being introduced in
-the manifests.
-
-## Profiles
-
-Profiles remain the fastest on-ramp.
-
-Recommended user-facing profiles:
-
-- `core`
- minimal baseline, safe default for most users trying ECC
-- `developer`
- best default for active software engineering work
-- `security`
- baseline plus security-heavy guidance
-- `research`
- baseline plus research/content/investigation tools
-- `full`
- everything classified and currently supported
-
-Profiles should be composable with additional `--with` and `--without` flags.
-
-Example:
-
-```bash
-ecc install --target claude --profile developer --with lang:typescript --with framework:nextjs --without capability:orchestration
-```
-
-## Proposed CLI Design
-
-### Primary Commands
-
-```bash
-ecc install
-ecc plan
-ecc list-installed
-ecc doctor
-ecc repair
-ecc uninstall
-ecc catalog
-```
-
-### Install CLI
-
-Recommended shape:
-
-```bash
-ecc install [--target ] [--profile ] [--with ]... [--without ]... [--config ] [--dry-run] [--json]
-```
-
-Examples:
-
-```bash
-ecc install --target claude --profile core
-ecc install --target cursor --profile developer --with lang:typescript --with framework:nextjs
-ecc install --target antigravity --with capability:security --with lang:python
-ecc install --config ecc-install.json
-```
-
-### Plan CLI
-
-Recommended shape:
-
-```bash
-ecc plan [same selection flags as install]
-```
-
-Purpose:
-
-- produce a preview without mutation
-- act as the canonical debugging surface for selective install
-
-### Catalog CLI
-
-Recommended shape:
-
-```bash
-ecc catalog profiles
-ecc catalog components
-ecc catalog components --family language
-ecc catalog show framework:nextjs
-```
-
-Purpose:
-
-- let users discover valid component names without reading docs
-- keep config authoring approachable
-
-### Compatibility CLI
-
-These legacy flows should still work during migration:
-
-```bash
-ecc-install typescript
-ecc-install --target cursor typescript
-ecc typescript
-```
-
-Internally these should normalize into the new request model and write
-install-state the same way as modern installs.
-
-## Proposed Config File
-
-### Filename
-
-Recommended default:
-
-- `ecc-install.json`
-
-Optional future support:
-
-- `.ecc/install.json`
-
-### Config Shape
-
-```json
-{
- "$schema": "./schemas/ecc-install-config.schema.json",
- "version": 1,
- "target": "cursor",
- "profile": "developer",
- "include": [
- "lang:typescript",
- "lang:python",
- "framework:nextjs",
- "capability:security"
- ],
- "exclude": [
- "capability:media"
- ],
- "options": {
- "hooksProfile": "standard",
- "mcpCatalog": "baseline",
- "includeExamples": false
- }
-}
-```
-
-### Field Semantics
-
-- `target`
- selected harness target such as `claude`, `cursor`, or `antigravity`
-- `profile`
- baseline profile to start from
-- `include`
- additional components to add
-- `exclude`
- components to subtract from the profile result
-- `options`
- target/runtime tuning flags that do not change component identity
-
-### Precedence Rules
-
-1. CLI arguments override config file values.
-2. config file overrides profile defaults.
-3. profile defaults override internal module defaults.
-
-This keeps the behavior predictable and easy to explain.
-
-## Modular Installation Flow
-
-The user-facing flow should be:
-
-1. load config file if provided or auto-detected
-2. merge CLI intent on top of config intent
-3. normalize the request into a canonical selection
-4. expand profile into baseline components
-5. add `include` components
-6. subtract `exclude` components
-7. resolve dependencies and target compatibility
-8. render a plan
-9. apply operations if not in dry-run mode
-10. write install-state
-
-The important UX property is that the exact same flow powers:
-
-- `install`
-- `plan`
-- `repair`
-- `uninstall`
-
-The commands differ in action, not in how ECC understands the selected install.
-
-## Target Behavior
-
-Selective install should preserve the same conceptual component graph across all
-targets, while letting target adapters decide how content lands.
-
-### Claude
-
-Best fit for:
-
-- home-scoped ECC baseline
-- commands, agents, rules, hooks, platform config, orchestration
-
-### Cursor
-
-Best fit for:
-
-- project-scoped installs
-- rules plus project-local automation and config
-
-### Antigravity
-
-Best fit for:
-
-- project-scoped agent/rule/workflow installs
-
-### Codex / OpenCode
-
-Should remain additive targets rather than special forks of the installer.
-
-The selective-install design should make these just new adapters plus new
-target-specific mapping rules, not new installer architectures.
-
-## Technical Feasibility
-
-This design is feasible because the repo already has:
-
-- install module and profile manifests
-- target adapters with install-state paths
-- plan inspection
-- install-state recording
-- lifecycle commands
-- a unified `ecc` CLI surface
-
-The missing work is not conceptual invention. The missing work is productizing
-the current substrate into a cleaner user-facing component model.
-
-### Feasible In Phase 1
-
-- profile + include/exclude selection
-- `ecc-install.json` config file parsing
-- catalog/discovery command
-- alias mapping from user-facing component IDs to internal module sets
-- dry-run and JSON planning
-
-### Feasible In Phase 2
-
-- richer target adapter semantics
-- merge-aware operations for config-like assets
-- stronger repair/uninstall behavior for non-copy operations
-
-### Later
-
-- reduced publish surface
-- generated slim bundles
-- remote component fetch
-
-## Mapping To Current ECC Manifests
-
-The current manifests do not yet expose a true user-facing `lang:*` /
-`framework:*` / `capability:*` taxonomy. That should be introduced as a
-presentation layer on top of the existing modules, not as a second installer
-engine.
-
-Recommended approach:
-
-- keep `install-modules.json` as the internal resolution catalog
-- add a user-facing component catalog that maps friendly component IDs to one or
- more internal modules
-- let profiles reference either internal modules or user-facing component IDs
- during the migration window
-
-That avoids breaking the current selective-install substrate while improving UX.
-
-## Suggested Rollout
-
-### Phase 1: Design And Discovery
-
-- finalize the user-facing component taxonomy
-- add the config schema
-- add CLI design and precedence rules
-
-### Phase 2: User-Facing Resolution Layer
-
-- implement component aliases
-- implement config-file parsing
-- implement `include` / `exclude`
-- implement `catalog`
-
-### Phase 3: Stronger Target Semantics
-
-- move more logic into target-owned planning
-- support merge/generate operations cleanly
-- improve repair/uninstall fidelity
-
-### Phase 4: Packaging Optimization
-
-- narrow published surface
-- evaluate generated bundles
-
-## Recommendation
-
-The next implementation move should not be "rewrite the installer."
-
-It should be:
-
-1. keep the current manifest/runtime substrate
-2. add a user-facing component catalog and config file
-3. add `include` / `exclude` selection and catalog discovery
-4. let the existing planner and lifecycle stack consume that model
-
-That is the shortest path from the current ECC codebase to a real selective
-install experience that feels like ECC 2.0 instead of a large legacy installer.
diff --git a/docs/architecture/cross-harness.md b/docs/architecture/cross-harness.md
index ec8d21a09..768414b72 100644
--- a/docs/architecture/cross-harness.md
+++ b/docs/architecture/cross-harness.md
@@ -59,6 +59,9 @@ Adapters should stay thin. The shared behavior belongs in `skills/`, `rules/`, `
## Shared Memory Contract
+The session snapshot side of this contract (`ecc.session.v1`) is specified in
+[session-adapter-contract.md](session-adapter-contract.md).
+
ECC Memory Vault is the common knowledge-transfer surface for Claude, Codex,
Hermes, Cursor, OpenCode, and other agents. It stores portable
`ecc.memory.v1` Markdown documents in three scopes:
diff --git a/docs/architecture/eval-harness-frameworks.md b/docs/architecture/eval-harness-frameworks.md
new file mode 100644
index 000000000..9696a13d5
--- /dev/null
+++ b/docs/architecture/eval-harness-frameworks.md
@@ -0,0 +1,330 @@
+# Eval Harness Frameworks
+
+Local capsule, inspection, fixture replay, and receipt building blocks.
+Candidate execution and promotion are unavailable.
+They live in `scripts/lib/eval-harness/`, ship with a CLI at
+`scripts/eval-harness.js`, and have an end-to-end example under
+`examples/eval-harness/`. The example runs locally, offline, and inside temporary
+directories. It does not merge, deploy, publish, or spend.
+
+```sh
+node scripts/eval-harness.js example
+```
+
+## Why these five
+
+The harness engineering plan v2 (August 2026) describes a twelve-layer stack.
+The part that belongs in the portable ECC package is the contract surface any
+harness can install and exercise: record what happened, prove it was not
+altered, gate a proposed change behind an external checker, replay tool calls
+without re-firing effects, and hand a verifier something it can check without
+trusting the producer. The execution gate remains disabled pending a verified OS containment backend.
+The other modules expose local utilities, not a trust decision about code.
+
+| Framework | Module | Plan epic | What it gives you today |
+| --- | --- | --- | --- |
+| Envelope | `envelope.js`, `schemas/capsule-envelope.schema.json` | 01 telemetry and capsule contract | `capsule-envelope/v1`, stable identifiers, effect classes SE0 to SE4, default-deny payload allowlist, secret canaries |
+| Capsule | `capsule.js` | 02 local execution capsule | Append-only NDJSON journal, five lineages, sha256 predecessor links, `verify` that fails at the exact entry, byte-stable projection, minimal export bundle |
+| Gate | `gate.js`, `gate-child.js` | 03 verification gate | Static source digests and syntactic warnings; all execution entrypoints refuse |
+| Replay | `replay.js`, `effect-fence.js` | 04 replay-safe branching | Declared determinism and effect class per tool, content-addressed fixtures, `tool.fixture_missing` fail-closed replay, retired child preload refuses execution |
+| Receipt | `receipt.js` | 07 verifiable receipts | Offline receipt over capsule root, entry count, artifact digest, and gate receipt; detached signature interface; verification names the failing check |
+
+Epics 05 (offline self-improvement) and 06 (causal triage and compaction
+invariance) are not implemented. They consume the records these five produce.
+
+## Effect classes
+
+Every journal entry, tool declaration, and variant manifest carries one class.
+
+| Class | Meaning | Where it is allowed |
+| --- | --- | --- |
+| SE0 | Read-only evaluation or schema validation | Everywhere |
+| SE1 | Reversible local writes inside the capsule or work root | Journal, gate metadata |
+| SE2 | Process or filesystem mutation, no live network writes | Candidate execution unavailable |
+| SE3 | Append-only remote evidence publication | Never in replay; trusted record-mode caller controls authorization; refused in replay |
+| SE4 | Economic, counterparty, payment, provider, or secret-handling effects | Never in replay; record mode requires the trusted caller to forbid it |
+
+Effect classes are declarations, not OS permissions. Static inspection reports
+effect-class expansion but cannot enforce a declaration. The replayer refuses
+SE3 and above in replay mode regardless of fixtures; record mode invokes the
+caller-supplied implementation up to its configured maximum. Only register
+trusted implementations. No JavaScript tool wrapper isolates arbitrary code.
+
+## Capsule journal
+
+A capsule is a directory with `capsule.json`, `journal.ndjson`, and an optional
+`projection.json`. Each line of the journal is one canonical-JSON envelope. The
+first entry links to sixty-four zeros; every later entry links to the previous
+`entry_hash`.
+
+```js
+const { capsule } = require('./scripts/lib/eval-harness');
+const c = capsule.Capsule.create('.ecc/capsules/run-42', { task_family: 'slugify' });
+c.append('plan', 'inspection.start', { task_id: 't01' });
+c.append('attempt', 'gate.unavailable', { status: 'blocked', reason: 'gate.isolation_required' });
+capsule.verify('.ecc/capsules/run-42'); // { ok, code, failed_at, root_hash }
+```
+
+`verify` returns `ok: false` with a stable code and the exact failing index for
+a changed byte (`capsule.invalid_entry`), a dropped or swapped entry
+(`capsule.reordered` or `capsule.broken_link`), and a partial trailing write
+(`capsule.truncated_tail`). The journal digest covers the original bytes;
+invalid UTF-8 is rejected as `capsule.non_canonical`. `project` derives stable
+content from the verified journal snapshot and validated metadata. `exportBundle`
+copies the three capsule files and nothing from the workspace.
+
+Metadata is validated before creation writes and when opening, verifying or
+projecting a capsule. IDs use the envelope ID pattern; harness/task family must
+be nonempty, and created_at must use the canonical ISO timestamp produced by
+Date.toISOString(). Missing, unreadable or malformed metadata returns
+`capsule.metadata_invalid`; invalid UTF-8 is also rejected. Every journal entry must match metadata schema,
+run_id, capsule_id, harness_version and task_family, or verification returns
+`capsule.metadata_mismatch` at that entry. Empty journals have no historical
+identity binding; their projection and receipt bind the metadata values.
+created_at is shape-checked but is not authenticated by journal entries.
+
+Envelope v1 enforces the scalar payload types declared in
+`schemas/capsule-envelope.schema.json`. String fields require strings; number
+fields require finite numbers, and integer fields require integers. Only
+`exit_code` accepts null. No extra nonnegative restrictions are imposed on these
+payload numbers. Omitted append payloads still default to an empty object.
+Explicit null, arrays, primitives, exotic objects, accessors, symbol keys and
+non-enumerable properties are rejected. Plain data objects with either the normal
+or null prototype are accepted. Validation inspects descriptors before reading
+values; it does not isolate proxies or arbitrary caller JavaScript.
+
+Retained fields are validated before canary scanning or hashing. Undefined,
+non-finite numbers, functions, symbols, BigInt and nested/cyclic objects are
+refused instead of coerced, dropped from serialized bytes or recursively scanned.
+`redactPayload` adds an `errors` array to its existing result; callers must check
+it alongside `dropped` and `findings`. Append reports `capsule.payload_invalid`
+without writing a journal entry; the existing finally path releases its owned
+lock. Strict unknown payload keys still report `capsule.payload_denied`.
+`strict: false` permits dropping unknown keys, but never invalid retained values.
+Custom allowlists can narrow v1 fields only, and cannot widen the persisted schema.
+
+Envelope validation also requires its own schema-defined fields and rejects
+unknown top-level fields even when the supplied hash has been recomputed. Invalid
+stored records return `capsule.invalid_entry` at their journal index. This tightens
+acceptance of malformed v1 data: existing nonconforming callers/journals need
+explicit correction; no automatic migration or healing is performed. Valid v1
+bytes and hashes remain unchanged. Generic key preservation and remaining
+non-JSON limitations are described below; neither supplies OS containment.
+
+The generic canonicalizer preserves every selected own enumerable JSON key as an
+own data property, including `__proto__`, `constructor` and `prototype`. It does
+not invoke an inherited setter while constructing the canonical object. Results
+retain their ordinary object prototype. Envelope schema rejection is separate:
+an own `__proto__` key is valid generic JSON data but remains an unknown envelope
+field. Receipt schema acceptance is unchanged; hashing a field is not permission
+from a higher-level schema.
+
+Traversal, key sorting, array handling, undefined omission, JSON.stringify and
+UTF-8 hashing retain their prior policy, including JavaScript's ordering of
+numeric-looking keys. Schema-valid v1 journal/projection bytes and unaffected
+receipt/fixture bytes stay identical. Regression vectors were captured from the
+pre-fix implementation, including unsigned and synthetic string-signed receipts.
+Verification does not rewrite those stored artifacts.
+
+The earlier canonicalizer omitted own `__proto__` keys, creating hash aliases.
+Corrected inputs retaining that key intentionally produce different hashes. An
+artifact retaining it with a legacy digest fails existing hash checks; a fixture
+lookup does not fall back to the old aliased key. Existing key-free stored bytes
+remain readable as those bytes, but cannot authenticate richer original inputs
+whose keys were lost. Recovery requires explicit re-recording from a trusted
+source or receipt rebuilding/re-signing; there is no automatic rekey, migration,
+rewrite, dual-hash acceptance or recovery of already discarded information.
+
+This correction does not define a stricter generic policy for undefined,
+functions/symbols, non-finite numbers, sparse arrays, class/toJSON/getter behavior,
+cycles, resource limits or hostile proxies. Their prior behavior remains; no
+claim of unambiguous hashing for every JavaScript value is made. The envelope's
+stricter scalar validation remains a separate layer.
+
+Append operations serialize cooperating writers using an exclusive local
+`.append.lock` file. Acquisition uses `wx` and fails immediately with
+`capsule.busy` when the path exists, regardless of age or contents. There is no
+waiting, retry, PID/age heuristic, or automatic stale unlocking. Under ownership,
+each append reloads and verifies the complete journal and metadata, then derives
+its sequence and predecessor hash from that snapshot. Preopened handles never
+use cached sequence/hash values as authoritative state. Full validation costs
+O(journal size) per append; this implementation is intended for small local
+journals.
+
+The writer handles short writes until the complete UTF-8 entry has been written,
+then fsyncs the journal. The append lock is released in finally on success,
+validation refusal, or ordinary I/O exceptions. A zero-progress write returns
+`capsule.write_failed`. Release checks the open lock descriptor's device/inode
+against the path before unlinking; a detected missing/replaced lock returns
+`capsule.lock_lost` and a replacement is preserved. This is cooperative ownership
+checking, not atomic protection against an actor replacing paths between syscalls.
+The local filesystem must support exclusive file creation and stable identities.
+
+A process crash can leave `.append.lock` behind. Acquisition/cleanup I/O failures
+can also leave a lock that was not safely released. Further appends stay busy;
+only an operator who has stopped all writers and inspected the capsule should
+perform recovery. The library never guesses ownership, removes an old lock,
+truncates a tail, or repairs journal bytes automatically.
+
+A write failure may leave a partial entry; later appends verify the journal and
+refuse the invalid tail, preserving evidence. A full entry may already exist when
+fsync, close or lock release throws. Such a failure is an ambiguous acknowledgement,
+not proof of rollback: inspect disk before retrying, or a logical event could be
+recorded twice. No transaction, exactly-once retry, parent-directory fsync, or
+power-loss durability guarantee is added here.
+
+Create, read/verify, projection, receipt production and export are not serialized
+by the append lock. Use quiescent capsules for consistent receipts/exports; there
+is no concurrent export guarantee or hostile-filesystem containment. The append
+repair does not change the disabled candidate execution boundary.
+
+What the chain does not claim: it does not stop an operator from replacing the
+whole log. That is the job of a witnessed transparency log, which is a later,
+opt-in layer outside this package.
+
+## Verification gate: unavailable
+
+**Supported candidate execution backends: none, on any OS.** `runGate` and
+`runVariant` throw `gate.isolation_required` unconditionally, before reading
+configuration, copying files, loading candidate modules, or creating receipts.
+`gate run` exits 1 before reading its config or creating a capsule. Direct
+`gate-child.js` invocation and the retired `effect-fence.js` preload also refuse
+before loading requests or candidate code. Trust flags and caller-supplied
+executor objects cannot enable execution. There is no promotion path.
+
+The former directory copy and JavaScript interception did not isolate host
+reads, alternate builtin loaders, or filesystem descriptors and promises.
+Keeping answers in a parent process did not hide the taskset on disk. The
+interception code and staged execution implementation have been removed.
+Node's [permission model](https://nodejs.org/api/permissions.html) and
+[`vm` module](https://nodejs.org/api/vm.html) are not substitutes for isolation
+of malicious code.
+
+A future executor must have a separately reviewed OS containment implementation
+and adversarial evidence on each supported OS. At minimum it must:
+
+- Expose only immutable, digested variant files and task inputs in an ephemeral
+ filesystem. Host tasksets, answers, credentials, configuration, sockets, and
+ other workspaces must be inaccessible, including via links and inherited FDs.
+- Enforce network, process, filesystem, and resource restrictions outside the
+ candidate runtime, with an unprivileged identity and a bounded lifetime.
+- Keep the checker, output/protocol validation, audit channel, and receipt
+ creation outside candidate control. Verify the actual runtime policy using
+ independent canaries before any candidate starts; refuse unavailable backends.
+- Reject failed, timed-out, signalled, incomplete, or malformed baseline runs
+ before evaluating candidate improvements. Require a complete unique result
+ for each task. Container availability or a caller's `verified: true` assertion
+ alone is not policy verification.
+
+Static APIs remain available for trusted, quiescent local source trees:
+`loadTaskset`, `loadVariant`, `digestDir`, and `scanTripwires`. Variant names are
+single components of 1–64 ASCII letters, digits, underscores or hyphens, starting
+with a letter or digit. Entries must be relative regular files included in the
+digest; absolute, parent-traversing, symlinked, and excluded entries are rejected.
+`.git` and `node_modules` remain excluded. Inspection does not resist concurrent
+host filesystem mutation and is not a sandbox or an execution attestation.
+Task IDs must be unique. Syntactic warnings are incomplete by design: zero hits
+prove neither safety nor correctness.
+
+`parseChildResult` and `baselineFailure(run, tasks)` are pure validation helpers
+for bounded protocol and baseline integrity regression checks. No executor calls
+them in this release. Their tests are not evidence of an operational gate or a
+verified OS backend. Existing manifest/config fixtures are preserved as data.
+
+## Replay-safe tool calls
+
+```js
+const { replay } = require('./scripts/lib/eval-harness');
+const store = new replay.FixtureStore('.ecc/fixtures');
+const tools = {
+ read_inventory: { effect_class: 'SE0', determinism: 'deterministic', impl: liveRead },
+ place_order: { effect_class: 'SE4', determinism: 'nondeterministic', impl: livePlace },
+};
+const r = replay.createReplayer(tools, { mode: 'replay', store, maxEffectClass: 'SE2' });
+r.call('read_inventory', { sku: 'gpu-8x' }); // served from fixture or tool.fixture_missing
+r.call('place_order', { sku: 'gpu-8x' }); // tool.effect_forbidden, always
+```
+
+Fixtures are keyed by the canonical hash of `(tool, args)` and store both an
+argument hash and a response hash, so a stale or edited fixture fails with
+`tool.fixture_mismatch`. Record mode executes caller-supplied trusted functions;
+replay uses fixtures. These wrappers do not constrain arbitrary effects inside
+an implementation. The legacy `EFFECT_FENCE_PRELOAD` export remains for import
+compatibility, but loading that file always throws `gate.isolation_required`.
+It no longer attempts JavaScript interception.
+
+## Offline receipts
+
+```sh
+node scripts/eval-harness.js receipt build .ecc/capsules/run-42 \
+ --artifact skills/my-skill/SKILL.md --out run-42.receipt.json
+node scripts/eval-harness.js receipt verify run-42.receipt.json exported-bundle/ \
+ --artifact skills/my-skill/SKILL.md
+```
+
+A receipt names the capsule root, entry count, journal digest, projection
+hash, artifact digest, and optional gate receipt digest, plus its own hash.
+`buildReceipt` now persists `projection.json` using the verified journal snapshot
+before returning the receipt. This is a producer write and can fail on a read-only
+capsule; copy a read-only source to a writable local directory before building.
+An explicit invalid artifact_digest throws `receipt.schema_invalid` before the
+projection write. Other construction failures continue to throw.
+
+`verifyReceipt` is read-only. It never regenerates or heals a missing projection.
+The supplied projection must parse and match the complete deterministic projection
+from the validated metadata/journal snapshot; its computed hash must match both
+its stored projection_hash and the receipt. Missing, unreadable, corrupt or
+substituted projections return `check: 'projection'`; invalid UTF-8 is rejected. Receipt identity mismatches
+and invalid capsule metadata return `check: 'metadata'`.
+
+Schema validation rejects negative, fractional, string or unsafe entry counts,
+invalid identity/schema values and malformed required digests before journal
+indexing. Optional artifact/gate digest fields must be SHA-256 values or null.
+Otherwise valid receipts retain signature, journal integrity, truncation,
+capsule-root and stale-checkpoint checks before projection/artifact comparisons.
+Missing or unreadable artifact files return `check: 'artifact'` rather than
+throwing. Every verification failure has `{ok: false, check, reason}` for these
+validated file/content cases.
+
+Existing v1 exported bundles retain their format. Older source directories whose
+receipts were built without a saved projection must explicitly run `capsule
+project` or rebuild the receipt before verification; verification itself never
+writes a replacement. The CLI validates --artifact, --gate and --out before file
+reads or producer writes: missing values, values that are another flag, and
+repeated flags exit with usage code 2. Disabled gate commands still refuse before
+configuration/capsule I/O.
+
+Signing remains a detached interface: pass a signer when building and a verifier
+when verifying. No key generation, transport or rotation happens in this package.
+A signature proves who vouched for the bytes, not that the run was correct.
+Optional gate-receipt hashing remains for compatibility with existing artifacts;
+accepting externally supplied bytes proves neither containment nor promotion.
+
+This slice addresses receipt/projection validation and metadata identity binding.
+The OS executor is still unavailable. Cooperative append serialization is
+described above; concurrent export/create and broader envelope/review findings
+remain separate. Package/count evidence is a separate ignore-scripts test scope
+and does not validate normal prepack or clear a release.
+
+## Where it plugs in
+
+- `skills/eval-harness/SKILL.md` describes eval-driven development. These
+ frameworks are the mechanical layer under its report format.
+- The `harness-optimizer` agent and `/harness-audit` command must report the gate
+ unavailable until a reviewed OS backend exists. They cannot emit new gate
+ receipts using this implementation.
+- The Rust `ecc2/src/harness_eval.rs` bounded evaluation loop is a separate,
+ earlier experiment. The Node frameworks are the portable surface.
+
+## Tests
+
+```sh
+node tests/lib/eval-harness/envelope.test.js
+node tests/lib/eval-harness/capsule.test.js
+node tests/lib/eval-harness/gate.test.js
+node tests/lib/eval-harness/security.test.js
+node tests/lib/eval-harness/replay.test.js
+node tests/lib/eval-harness/receipt.test.js
+node tests/lib/eval-harness/cli.test.js
+node examples/eval-harness/run-example.js
+```
diff --git a/docs/SESSION-ADAPTER-CONTRACT.md b/docs/architecture/session-adapter-contract.md
similarity index 100%
rename from docs/SESSION-ADAPTER-CONTRACT.md
rename to docs/architecture/session-adapter-contract.md
diff --git a/docs/fixes/HOOK-FIX-20260421-ADDENDUM.md b/docs/fixes/HOOK-FIX-20260421-ADDENDUM.md
deleted file mode 100644
index 331710357..000000000
--- a/docs/fixes/HOOK-FIX-20260421-ADDENDUM.md
+++ /dev/null
@@ -1,109 +0,0 @@
-# HOOK-FIX-20260421 Addendum — v2.1.116 argv 重複バグ
-
-朝セッションで commit 527c18b として修正済み。夜セッションで追加検証と、
-朝fix でカバーしきれない Claude Code 固有のバグを特定したので補遺を記録する。
-
-## 朝fixの形式
-
-```json
-"command": "C:/Users/sugig/.claude/skills/continuous-learning/hooks/observe-wrapper.sh pre"
-```
-
-`.sh` ファイルを直接 command にする形式。Git Bash が shebang 経由で実行する前提。
-
-## 夜 追加検証で判明したこと
-
-Node.js の `child_process.spawn` で `.sh` ファイルを直接実行すると Windows では
-**EFTYPE** で失敗する:
-
-```js
-spawn('C:/Users/sugig/.claude/skills/continuous-learning/hooks/observe-wrapper.sh',
- ['post'], {stdio:['pipe','pipe','pipe']});
-// → Error: spawn EFTYPE (errno -4028)
-```
-
-`shell:true` を付ければ cmd.exe 経由で実行できるが、Claude Code 側の実装
-依存のリスクが残る。
-
-## 夜 適用した追加 fix
-
-第1トークンを `bash`(PATH 解決)に変えた明示的な呼び出しに更新:
-
-```json
-{
- "hooks": {
- "PreToolUse": [{
- "matcher": "*",
- "hooks": [{
- "type": "command",
- "command": "bash \"C:/Users/sugig/.claude/skills/continuous-learning/hooks/observe-wrapper.sh\" pre"
- }]
- }],
- "PostToolUse": [{
- "matcher": "*",
- "hooks": [{
- "type": "command",
- "command": "bash \"C:/Users/sugig/.claude/skills/continuous-learning/hooks/observe-wrapper.sh\" post"
- }]
- }]
- }
-}
-```
-
-この形式は `~/.claude/hooks/hooks.json` 内の ECC 正規 observer 登録と
-同じパターンで、現実にエラーなく動作している実績あり。
-
-### Node spawn 検証
-
-```js
-spawn('bash "C:/Users/sugig/.claude/skills/continuous-learning/hooks/observe-wrapper.sh" post',
- [], {shell:true});
-// exit=0 → observations.jsonl に正常追記
-```
-
-## Claude Code v2.1.116 の argv 重複バグ(詳細)
-
-朝fix docの「Defect 2」として `bash.exe: bash.exe: cannot execute binary file` を
-記録しているが、その根本メカニズムが特定できたので記す。
-
-### 再現
-
-```bash
-"C:\Program Files\Git\bin\bash.exe" "C:\Program Files\Git\bin\bash.exe"
-# stderr: "C:\Program Files\Git\bin\bash.exe: C:\Program Files\Git\bin\bash.exe: cannot execute binary file"
-# exit: 126
-```
-
-bash は argv[1] を script とみなし読み込もうとする。argv[1] が bash.exe 自身なら
-ELF/PE バイナリ検出で失敗 → exit 126。エラー文言は完全一致。
-
-### Claude Code 側の挙動
-
-hook command が `"C:\Program Files\Git\bin\bash.exe" "C:\Users\...\wrapper.sh"`
-のとき、v2.1.116 は**第1トークン(= bash.exe フルパス)を argv[0] と argv[1] の
-両方に渡す**と推定される。結果 bash は argv[1] = bash.exe を script として
-読み込もうとして 126 で落ちる。
-
-### 回避策
-
-第1トークンを bash.exe のフルパス+スペース付きパスにしないこと:
-1. `OK:` `bash` (PATH 解決の単一トークン)— 夜fix / hooks.json パターン
-2. `OK:` `.sh` 直接パス(Claude Code の .sh ハンドリングに依存)— 朝fix
-3. `BAD:` `"C:\Program Files\Git\bin\bash.exe" ""` — 1トークン目が quoted で空白込み
-
-## 結論
-
-朝fix(直接 .sh 指定)と夜fix(明示的 bash prefix)のどちらも argv 重複バグを
-踏まないが、**夜fixの方が Claude Code の実装依存が少ない**ため推奨。
-
-ただし朝fix commit 527c18b は既に docs/fixes/ に入っているため、この Addendum を
-追記することで両論併記とする。次回 CLI 再起動時に夜fix の方が実運用に残る。
-
-## 関連
-
-- 朝 fix commit: 527c18b
-- 朝 fix doc: docs/fixes/HOOK-FIX-20260421.md
-- 朝 apply script: docs/fixes/apply-hook-fix.sh
-- 夜 fix 記録(ローカル): C:\Users\sugig\Documents\Claude\Projects\ECC作成\hook-fix-report-20260421.md
-- 夜 fix 適用ファイル: C:\Users\sugig\.claude\settings.local.json
-- 夜 backup: C:\Users\sugig\.claude\settings.local.json.bak-hook-fix-20260421
diff --git a/docs/fixes/INSTALL-HOOK-WRAPPER-FIX-20260422.md b/docs/fixes/INSTALL-HOOK-WRAPPER-FIX-20260422.md
deleted file mode 100644
index 0572f85f6..000000000
--- a/docs/fixes/INSTALL-HOOK-WRAPPER-FIX-20260422.md
+++ /dev/null
@@ -1,66 +0,0 @@
-# install_hook_wrapper.ps1 argv-dup bug workaround (2026-04-22)
-
-## Summary
-
-`docs/fixes/install_hook_wrapper.ps1` is the PowerShell helper that copies
-`observe-wrapper.sh` into `~/.claude/skills/continuous-learning/hooks/` and
-rewrites `~/.claude/settings.local.json` so the observer hook points at it.
-
-The previous version produced a hook command of the form:
-
-```
-"C:\Program Files\Git\bin\bash.exe" "C:\Users\...\observe-wrapper.sh"
-```
-
-Under Claude Code v2.1.116 the first argv token is duplicated. When that token
-is a quoted Windows executable path, `bash.exe` is re-invoked with itself as
-its `$0`, which fails with `cannot execute binary file` (exit 126). PR #1524
-documents the root cause; this script is a companion that keeps the installer
-in sync with the fixed `settings.local.json` layout.
-
-## What the fix does
-
-- First token is now the PATH-resolved `bash` (no quoted `.exe` path), so the
- argv-dup bug no longer passes a binary as a script.
-- The wrapper path is normalized to forward slashes before it is embedded in
- the hook command, avoiding MSYS backslash handling surprises.
-- `PreToolUse` and `PostToolUse` receive distinct commands with explicit
- `pre` / `post` positional arguments, matching the shape the wrapper expects.
-- The settings file is written with LF line endings so downstream JSON parsers
- never see mixed CRLF/LF output from `ConvertTo-Json`.
-
-## Resulting command shape
-
-```
-bash "C:/Users//.claude/skills/continuous-learning/hooks/observe-wrapper.sh" pre
-bash "C:/Users//.claude/skills/continuous-learning/hooks/observe-wrapper.sh" post
-```
-
-## Usage
-
-```powershell
-# Place observe-wrapper.sh next to this script, then:
-pwsh -File docs/fixes/install_hook_wrapper.ps1
-```
-
-The script backs up `settings.local.json` to
-`settings.local.json.bak-` before writing.
-
-## PowerShell 5.1 compatibility
-
-`ConvertFrom-Json -AsHashtable` is PowerShell 7+ only. The script tries
-`-AsHashtable` first and falls back to a manual `PSCustomObject` →
-`Hashtable` conversion on Windows PowerShell 5.1. Both hook buckets
-(`PreToolUse`, `PostToolUse`) and their inner `hooks` arrays are
-materialized as `System.Collections.ArrayList` before serialization, so
-PS 5.1's `ConvertTo-Json` cannot collapse single-element arrays into
-bare objects. Verified by running `powershell -NoProfile -File
-docs/fixes/install_hook_wrapper.ps1` on a Windows 11 machine with only
-Windows PowerShell 5.1 installed (no `pwsh`).
-
-## Related
-
-- PR #1524 — settings.local.json shape fix (same argv-dup root cause)
-- PR #1511 — skip `AppInstallerPythonRedirector.exe` in observer python resolution
-- PR #1539 — locale-independent `detect-project.sh`
-- PR #1542 — `patch_settings_cl_v2_simple.ps1` companion fix
diff --git a/docs/fixes/PATCH-SETTINGS-SIMPLE-FIX-20260422.md b/docs/fixes/PATCH-SETTINGS-SIMPLE-FIX-20260422.md
deleted file mode 100644
index 4a3e8cdc7..000000000
--- a/docs/fixes/PATCH-SETTINGS-SIMPLE-FIX-20260422.md
+++ /dev/null
@@ -1,78 +0,0 @@
-# patch_settings_cl_v2_simple.ps1 argv-dup bug workaround (2026-04-22)
-
-## Summary
-
-`docs/fixes/patch_settings_cl_v2_simple.ps1` is the minimal PowerShell
-helper that patches `~/.claude/settings.local.json` so the observer hook
-points at `observe-wrapper.sh`. It is the "simple" counterpart of
-`docs/fixes/install_hook_wrapper.ps1` (PR #1540): it never copies the
-wrapper script, it only rewrites the settings file.
-
-The previous version of this helper registered the raw `observe.sh` path
-as the hook command, shared a single command string across `PreToolUse`
-and `PostToolUse`, and relied on `ConvertTo-Json` defaults that can emit
-CRLF line endings. Under Claude Code v2.1.116 the first argv token is
-duplicated, so the wrapper needs to be invoked with a specific shape and
-the two hook phases need distinct entries.
-
-## What the fix does
-
-- First token is the PATH-resolved `bash` (no quoted `.exe` path), so the
- argv-dup bug no longer passes a binary as a script. Matches PR #1524 and
- PR #1540.
-- The wrapper path is normalized to forward slashes before it is embedded
- in the hook command, avoiding MSYS backslash handling surprises.
-- `PreToolUse` and `PostToolUse` receive distinct commands with explicit
- `pre` / `post` positional arguments.
-- The settings file is written UTF-8 (no BOM) with CRLF normalized to LF
- so downstream JSON parsers never see mixed line endings.
-- Existing hooks (including legacy `observe.sh` entries and unrelated
- third-party hooks) are preserved — the script only appends the new
- wrapper entries when they are not already registered.
-- Idempotent on re-runs: a second invocation recognizes the canonical
- command strings and logs `[SKIP]` instead of duplicating entries.
-
-## Resulting command shape
-
-```
-bash "C:/Users//.claude/skills/continuous-learning/hooks/observe-wrapper.sh" pre
-bash "C:/Users//.claude/skills/continuous-learning/hooks/observe-wrapper.sh" post
-```
-
-## Usage
-
-```powershell
-pwsh -File docs/fixes/patch_settings_cl_v2_simple.ps1
-# Windows PowerShell 5.1 is also supported:
-powershell -NoProfile -ExecutionPolicy Bypass -File docs/fixes/patch_settings_cl_v2_simple.ps1
-```
-
-The script backs up the existing settings file to
-`settings.local.json.bak-` before writing.
-
-## PowerShell 5.1 compatibility
-
-`ConvertFrom-Json -AsHashtable` is PowerShell 7+ only. The script tries
-`-AsHashtable` first and falls back to a manual `PSCustomObject` →
-`Hashtable` conversion on Windows PowerShell 5.1. Both hook buckets
-(`PreToolUse`, `PostToolUse`) and their inner `hooks` arrays are
-materialized as `System.Collections.ArrayList` before serialization, so
-PS 5.1's `ConvertTo-Json` cannot collapse single-element arrays into bare
-objects.
-
-## Verified cases (dry-run)
-
-1. Fresh install — no existing settings → creates canonical file.
-2. Idempotent re-run — existing canonical file → `[SKIP]` both phases,
- file contents unchanged apart from the pre-write backup.
-3. Legacy `observe.sh` present → preserves the legacy entries and
- appends the new `observe-wrapper.sh` entries alongside them.
-
-All three cases produce LF-only output and match the shape registered by
-PR #1524's manual fix to `settings.local.json`.
-
-## Related
-
-- PR #1524 — settings.local.json shape fix (same argv-dup root cause)
-- PR #1539 — locale-independent `detect-project.sh`
-- PR #1540 — `install_hook_wrapper.ps1` argv-dup fix (companion script)
diff --git a/docs/ja-JP/skills/motion-ui/SKILL.md b/docs/ja-JP/skills/motion-ui/SKILL.md
deleted file mode 100644
index f0c00fd66..000000000
--- a/docs/ja-JP/skills/motion-ui/SKILL.md
+++ /dev/null
@@ -1,11 +0,0 @@
----
-name: motion-ui
-description: 日本語翻訳:このファイルは motion-ui 用の日本語翻訳が必要です
-origin: ECC
----
-
-# motion-ui - 日本語翻訳進行中
-
-このファイルの翻訳は実装中です。英語版は元のスキルファイルを参照してください。
-
-詳細は:`D:/tmp/everything-claude-code/skills/motion-ui/SKILL.md`
diff --git a/docs/releases/1.10.0/discussion-announcement.md b/docs/releases/1.10.0/discussion-announcement.md
deleted file mode 100644
index 9d4b5a6f3..000000000
--- a/docs/releases/1.10.0/discussion-announcement.md
+++ /dev/null
@@ -1,55 +0,0 @@
-# ECC v1.10.0 is live
-
-ECC just crossed **140K stars**, and the public release surface had drifted too far from the actual repo.
-
-So v1.10.0 is a hard sync release:
-
-- **38 agents**
-- **156 skills**
-- **72 commands**
-- plugin/install metadata corrected
-- top-line docs and release surfaces brought back in line
-
-This release also folds in the operator/media lane that has been growing around the core harness system:
-
-- `brand-voice`
-- `social-graph-ranker`
-- `connections-optimizer`
-- `customer-billing-ops`
-- `google-workspace-ops`
-- `project-flow-ops`
-- `workspace-surface-audit`
-- `manim-video`
-- `remotion-video-creation`
-
-And on the 2.0 side:
-
-ECC 2.0 is now **real as an alpha control-plane surface** in-tree under `ecc2/`.
-
-It builds today and exposes:
-
-- `dashboard`
-- `start`
-- `sessions`
-- `status`
-- `stop`
-- `resume`
-- `daemon`
-
-That does **not** mean the full ECC 2.0 roadmap is done.
-
-It means the control-plane alpha is here, usable, and moving out of the “just a vision” category.
-
-The shortest honest framing right now:
-
-- ECC 1.x is the battle-tested harness/workflow layer shipping broadly today
-- ECC 2.0 is the alpha control-plane growing on top of it
-
-If you have been waiting for:
-
-- cleaner install surfaces
-- stronger cross-harness parity
-- operator workflows instead of just coding primitives
-- a real control-plane direction instead of scattered notes
-
-this is the release that makes the repo feel coherent again.
diff --git a/docs/releases/1.8.0/x-quote-eval-skills.md b/docs/releases/1.8.0/x-quote-eval-skills.md
deleted file mode 100644
index 028a72bb0..000000000
--- a/docs/releases/1.8.0/x-quote-eval-skills.md
+++ /dev/null
@@ -1,5 +0,0 @@
-# X Quote Draft - Eval Skills Post
-
-Strong eval skills are now built deeper into ECC.
-
-v1.8.0 expands eval-harness patterns, pass@k guidance, and release-level verification loops so teams can measure reliability, not guess it.
diff --git a/docs/releases/1.8.0/x-quote-plankton-deslop.md b/docs/releases/1.8.0/x-quote-plankton-deslop.md
deleted file mode 100644
index 8ea7093e1..000000000
--- a/docs/releases/1.8.0/x-quote-plankton-deslop.md
+++ /dev/null
@@ -1,5 +0,0 @@
-# X Quote Draft - Plankton / De-slop Workflow
-
-The quality gate model matters.
-
-In v1.8.0 we pushed harder on write-time quality enforcement, deterministic checks, and cleaner loop recovery so agents converge faster with less noise.
diff --git a/docs/releases/2.1.0/assets/ecc-plan-canvas-demo.webm b/docs/releases/2.1.0/assets/ecc-plan-canvas-demo.webm
deleted file mode 100644
index 3017e32a6148292c4f72dacba71898d7ed28ab97..0000000000000000000000000000000000000000
GIT binary patch
literal 0
HcmV?d00001
literal 286856
zcmcGz^OG+;@Gdw$W81dpjBVSt?U^&SZQHhO+qP|f?)%-lTf6rU*sjhGPjxDJI_ab<
z9crn0{|FwlPjW}ty2o8{6a
z+ZCl;6^tfXVWwOiQ1HJIx=O9}e`sB{EBZehvdWOTa&;gujcixUe-Kx>>px=3Fai=7`lCC2LKVbWCyw0nS=)bg@&l1pt#A1qFk@902X7
z)(3*;cLst6X9j?%)`zP$1c0k{1c3a{8VLA1JLens`KSI8%rZM2M;JIdKYeY#Wxrd$N%ubeeqDh6FE0SYtNYL|;1wXg)%OfA0+ju}{m5@)
zZ0R5S%76F00w#XzP5~8wL7yG~62S7O&&hA?H}37%{yS|Skn%&|koUM}1c(CU0wTZt
zUI{J%HNWCtetGx4@-yFg_jyUz1OtFN0K((1{XO8KukXQc$RQyHdu#R~+s=xE2EKK)qjtUcSv~HZFT49H8qyRl
z{r^S2Hn^uS0PuUN*0)TsSjOf)UtV4=uT?A9aVJaz(H1%Qi)eWd)(d{dfwyngVWFnD
zRo=JO_T2N+Ih*~PM4Sr|O*HmP7bK+>9ClVDVeVaZ-sTl?ULp<_kILYV-rF+_HuUM(
zcR(i7QW(umD@U$w_fcMi9{cR9t+W4$VB!=#5Qn8w4ddFTd{)};TK{C2Yus%rdyjRp*A&xw|>nrN;pbQ
ztk&deNIF>1lI8U&UHcnuyu2n@RKJ5Xbn27N4vi)8L~M}7Mv+00P?Z_Ih|Bdj(8D6L$Dri{
zs;oeL=4lyub1)f)WF>B*Q+H%Zl7|=%QglWgX5Lr6z|IUJ!oM!cJ(AoM
zKc|J?q{?A>cv{ha(>m0c5-pf~E#?mNcbz#06L-_iefq%VXt
zvFoKCr(6P>O(~D+U@2`Pz=$0qT_~MM89WDD*gl)YZlKqXb3;h9^90+;D2d4#f-1q4
zNn~s=-#0s1&AS!ZJ)AX9!n6!7z-sI?E6_(haVqxJ^1CYhnxNLeYG2jlqE^IzDO9Is
z9IL0#s2OgxP9o_E1G8UtWhs^|GL5*_xvCjQK6s22@mHsh#}QAurY2vLQE*A%mh-ZG
zL}63kAs12yjHN0NYGV&8rvVQ?THKIc$pH
zj4=$diyLOIm^8&=)IqdgFH5+2JA8#9S&3Qd--<&hU1|PlHs6Ho(jgDRe`7zYgsqlG
z(-Q1PM*qe<6ypD6Q8#0^LsWF`cjDi$q86OywjPXwgNBW>yyB~4SU}M<$@zccoK{y?{M84Ue`n-o4emxrgRKBWa7I4Ui(sZEXH298S%tN9Ea
zye~QEEg+b|`%VngM2-Al?2Mve6pJY&hAhb)E~bKcoCW&d#buJix;}-G?2ALP_GIk3
zQOEZx`1(kpp42@Cfp_BA+d0?62izK9saKO1V|;yTlZ~Rd?P1-h7{uW(u*jdd2sbWY
z{n_z1d4=n=9nuKCR-7+|@yVms6NAgyw&d?WV5!RSAsB$XH7XBPLFtgc}HZI8poo!vu-=A1(lB1m?Iw)
zzOG=mPBKkz;Xu?|=)a3jgTUSMelN2vu6muwgLONK=$-pfz06hQ={&=~gN_(S9%HL+
zzqmd2?Q?o#C)iY)1tyFteR8o&2a~(Uw$FycT`l~_xvAqT?)|!PLSv%jlVPw)yGe49
z=;Z4kn#u=+`I7|{078_S#6Qja>BXgKHds`uTCbkB7qbyG(Ny8={7~$7iGhIm}{x4V54GOs&MH0Ksaer9Csa(6HBWoI<`+x1KGg(-TYY
z45x-LuNFlU4~xjnZmxP!+m!9pBlY&n%&X}Vo=_6bFqWL7y89wA;K>2|Qd(GWo0JKE
zJm~ZJfU3ITX3+(Q{QI`39T&u`N}d5UHI~ppGy+~LvdYv(KHS>y(YUUx6|m27`RITjyY!F|BUkLqZB9g;-bZm&0M9
zz1%A3#c!GW_e9P2E|IX#N#I|~T2YN?yezVr&HG=L9tyQTC-Jr_tf;&0h$Hzvo~1ec
z5^AO&gyMhwsn)MfA1fF=w$>-y8r~^~k@>SzA%MO6`w~%Q9}6LhC3i7rBrZ8K#lbu+
zMuvkUj;K%6q1GX(PLwR}U8-e3d_*`%IwV>**^m;x
zWOen$1)1*OrLP!+PC_&-It2^_Ilyr(v?&@$aFq{_lA&TM>6iXz!(ciAjWj)XL?ThY$fTY8vs8P|80m6UT_CS%6vY
z*YqP9p6BzW!6Q@Dx8EjX01S0vjMt=w!gqp^Dx~i_$O<_SI<(?Wlw1n$(OzAMNPjbF
zX#{*^vEwN`I5zGFUM37THxC#LkIk>^ZOS5OnTxIM!S`TrQ*cx-n8HFi_C>V%1n
z5JlVdmEVahkF?}Hg8LrDv8|NwCz|CcEW?Z4@q
z&XOm05+kyklp1@p1bKVBTddN66l4wq4!4b<6x^3n;{oUI{fUpf7(-Dd`RAnj5q5(f
zY{7PIsSov(G^L^l6Zx5Tp?Z{8#Jpw=ucZ>2wVJ+>CrRmqY#2rvWeiPyrV?#(Xq^Yg
zk{K&X&rOgBhjDGlBmDUo5jhe5!l6hXio+jdo4&#fX?$kut6{4ERvY1Fa-~7<*Gin6
z^^!+=M)Y1YJ(q?;NASeWy(RRF8sr$ipMT^0pj~|D)|Vm2r_C?vcIO(yvkaXhP<7P&
zG3>uHudKH>lFP)QO*$2tS2P~#H42IB-D+5?4_AbTg0-IaQr)mKKG-P`^6_f*YwR6m
zXvMXtVM@}-u=J0SWhYwW>y`3f|JtJ0TZ`~fY)E8Fa;VQI7FlC0m}4`fVsZNyS=U}=
z&Dr5q$M-3%Mng8^Wc||YFt{e=yox-}^{WI7N13+rJ%Dsrz8_F8|fqveW8YWL&t^I{8-gu
zmU-^l>1|5$h(0)7?CHOsf)ts(oA%t_{;2kz^m(rUKC>1{S^TMNC9hK?6G3ILfA=OJ
zsePv&cRmkZu6IbbH5*Ez2Qeziq5>@YG4+nOCr0lx@6xQGCHooH)5Mzh|6Yy<@W_*qr4jYit*8
zcD@dfKkT@HM6rh+h*Ha&W81ck@Uj>@&ox&ico=C7iEr+wHS#*31e5Vl-QsZsEl!9Y
z2BVe^mrRj0qn%`C$eelY0xjH?iIXEt!RUkHt&-{0`$6{MVT^EI$_y9g5(aU9d)0#-
zm!lSfAHay@BwCY0@*mMf&t3^@Rz~cuY*3u;U}dIf;tk?
zLVVyPyet*)2HVL3t?n5T7%OBP$*P`Z_-w!0KV2V<>n9~BWZg|X+ZVAZQcv)W;Mt$<
zzl`kEs#YQh)!`#WjJ&W)5_#q_M2N9I2ICBR=<1_;5`J?)hsUa3`31M#fglf3MdCV%
zB}S94P{XCG&b0x0Kxd^_KRiG{UNzDBHDzO~R!_bN>!ti?iwajiM*pPB1uGTJA1Q%C
zPK6exkFATfB4n}7ef4oDCpLfjLFD#CWW4j^w0MJ#WY%>aDcaIXY|BFS!bzeZ!iW|i
zO^|>gfHmUoWRzYoEDC>`o_TC)IO`w6{0`PRRjY~Mm3Cv$XG#5Ha2{X9OZJ-ojHr>&
zHY9IU_E?=cIU%FxDv}PejwK`jD-ri3%^1KceKsl@_Fb(!0*YIPZV1iuw@KApS@kAkjIELd-FlE{{>@;bpI0eP6NgZry-kN*_|)$RPE9fvnmk`Qm7b3
zRITNHbPcX8r)25jW_>ZwAE3j{-HP)pQ0mDqwDFzy7i>{mkZA%ZViF9%F)bVSQ|OR?
zKvcoD<0iA<36Kr(jY%p7RX>eE>|Nh95xSDJg4PyqU*W#k)q+
z&rqo;F35Qn-F2-nC%c4?O_DEc8BZEdToS^--qSll;wVe#*0!^tEIv2rk+G;7?MZN3
z#B1=kBi8SS^HWoJvT!So{^{>sMU|8@ihCkd$f=Q`rH$iOTOp1@HdQ9#pU|1C=|=)S
zD|h?IK;x;(8G0c|3j_EO>F7OA)f*v}8^u}Tb*gy#TP97v*LQ5Gu{8+eg+}-_aP;j2
zy+rP&Z{<>}AQfZs&~sosADta0bLS~0kW@@hf0o_rHwCV)4QZu+^!_0t{Ir>xmWMw97u&feI-{vF+z_8u##Hb
zS%BxAPLFuj#~AgCYkuUDk6Km%mt5(ybrm9s26o52iG>kc76-&tnf3Pdht&Su4_sA}
zHoqO&IUlK)C&$0h-lUm6-81pWa3`tZxl
zRS2<@;)?tDfMHnr;Lu4MvnjBFjHJh<;IYOt^Q6h>(%r3_>u3Vd$5YUx3iu_v>i~
zPdW&?Jp1nEw|3zZLOKrGx;VH1+cS_`-0SpHV7e&j-Kv^X;B%rSz~HTQ*t0ah^{uj}
z>zf))l>f_XB4W5i`?nOrvF|PwLtsg9UzZ|pK!*Bq{bzk}ayxag%wpi*k@0(jemDvT
zS!|Ep8oLYlNB16TU9-Sw3Oj@V-(wRcgo*F0=i-2i01u1BH+hPx-gWG8vG`9t?RD(}
zm~~%A{XI)Q(r4j~fy?xZ35#O7u-j2zdr5J`W&8@u-L8;L;ZDxn0<3`EdJ6ERVqkRn
z{3seY5AYW?NZ;4uG;A43h#CUR#wS!@_tuVBx9;gnI`2})9jZAqOZXToA#a$9Ad%)+
z97MC}V9YKWEig@@n7&zCc?gJ+IpR1G=m@wjv59!zR1JkEO_>dK^D>JclF}=^tgJjZ
zPE8<%#JR6RSjTp`JvRNu0297}!%>&4Ty30kIiq0oa=^Z)V6mnIu@l}H4?5Ijp7%23
z58sB)Q(CIRnE1M-Z2D_7JOh=eKmC4cDx9K)*9_W*WvbR
zWdAa~?Q-*J7k7z-TIq)s`rI$p@;PpMTDp8EKjRI;p;MIgge8`)j8_Of^v7+wA!EoT
z(LXcW$yiz>dE0p|Eh$NXx2iwHq#h>Z+mPWMsaGt-kdu8Ls&584icANMT(+ln^CTJL
z?z}Q0o*|-I`Kx(xN_E+NnuPzCkrr(Rp%+aX3|D$tRf=*B8$!BeoN`5m%QNy}R8VaC
z0&E|J9naGStpbGv`7GA7-y?P0q;3vR7xZoIJ0G;pDl^t6ujfa!~2dUzW
z1Hsy7cn1^chbmc!gHZ2Ju6oZU|HGDb}EpsG)y!-JTsquzTgn*
zeC>l76GVHTa&L0N!O6Jm^Pt&i9(sEA5IYo!&mxZ;_yAgnlknoc92aNaP2viH1XLjg
zr5)s*`QSGD%+n$GZV|4agt}Hwbt%hkB)qolE~wz#Fs`b1H4XM%G(PqZ;m)oar6&0C
zL=1Sse*##`A}&N*y{#Gi_Ay3pZY#g$Ym~VvSZATur!*`qV(i6zPhvBDtpFsinXQv!
zl6tHlN+4?BNgJyR%sTv@&3Ts1v)H;(Kozt=
zG3+eL(z!VUI@YQJ3>E$aRhA#`Cj^AexZXmH_9&MhJ!BT`dEsg)r|7_hHjY
zfZNq4{`0*|vAd+*+N(oHtKHKc_o+neIfq;yQ~q*q#CPF-vAO%E?$)nV_h9;l=&S*-
zmo(oi*?#mr=v2CSqD5cugdg4ckB$wKpx$EwlaG&iJFn-9%Bk6LpHqG~pYHvd{I$OY
zcPpr*QB-78NF
zWhe6tPKVyaXi8atAl^^55L6iz;U5SBubVu#BJCII}uz1BCh?rsZJKlh6ss}-d{vfS^-*Kce*iI-df
zUdaZ0l;A~qQ0*_r7`J8WHL~|7Tmc>1W^Cf`6AKN0TC1>-@GVQ;USG=M%10uT?`6nt
z4+}EeNAG#Du>z-xtU7OmPse)~6!l21MYp0pg%}hv1@X4R_G5tVld23uBQho$fIORf
zI$^rp8v!P5VQ^CL5Z$H(YLNG6*sOKv5fNtjazV}zJbs095d!!hqqkr2r=;w-%>rL=
zFY9p>9o(q8euK)EpQq-NqNi$JjW^9y)LSSXm;fZb<;3^5>id1%vECr5GCxsPp7hgM
z4XRB}*`+?LQB8=(Ig3W;o8Ty$9e|ofsF(cpLKMWcr
zUbB(0A}RGTvVPxOj!N+GWPs(N5#g?;ktBDo%|N`~bmF=*l=)m5Tiz@om=<3<#Ph<2A#WEi<@e5|{MQd`|!)YBwvH)${XnW4$Ie^?JiAwa28?qFSc
ztKH9_dC#p>cvq%*Z4m9!;CB%WY>_UL|78)1>|`PK?G$l~_7>Z5J2DLZ2@JQtQ`l=i
zu0O?BR1i?y_2F)mXMk$b7_z5`qDl2>kx!ud003ooLV-^B
zrl|t)7(XoX*-s<_eA?+tu(2N5Y*Kz%Z-
za+TfGs@XFWnR|#n4TcL7tXedh`9w{h7F)kfuZNa)=On=|ScApl%zgr{?dIM4S7DpK965)Ei~w`iJPHxmVJ)9w;|%~D)MQ{)0b5@j|BB|c_IX)sVVGc
zT^!x404VPwY8r1>q90udIsDPWgk(-cQnJmza4ji|ljk`0Js<;6u~Ds^$t90l?Fk?h
z0^4lqNJ~YjPv=(qd@LRducetY}HS{(w=nS7)
z=hC7=eo6_R1x_bm#fP1>H~;>^Dt9Hl6q~j3k(NJf#A2i)@yqK3qbY=e(syVL1&!7foU;VRug2OARIWVMr|zb
z0cN7NgZtTv%FogcW{&@aE)%vsc0L&1+5I*Zo+J9%H6r%o=o(<(EuC+UxnTzEV;^_oe$Ye_91=n1(p?w^15Pm(2gr(-C8
zNYNtV5m&IU;L(cK{La-(<1;pZ5S#GY7#74T{RHgG7NyP7jiwz&`0`KKr2=#dwlVpD
z#QmGv21|3Bd0&ktO4LM6KO27@09#>#I0N<1F`^-NLb3!0yqQp1;3>(p*N&MjszM_
z+RJM_WYmt?;j!lob1eLnDXA4c-9mcKYo(be<}zN=p(p%!6lB{?sJyji716wDMU5f1
zg0*Qd*BCrZt9@%lmvkrv7r&riAo!g^)i@hC2b<;aGSl4oq;XvjqhN$rX_U|_`FBUk
zBax4!E$I#XA^JK~=)%}yby@y5<|JTw~Vz6B{$h&$OT0?KrEWPggwigwtC
zYH%JJK#FuD7H~ev_s5&Rd>)$xzD>fDzjQ!uwu53*r$2tyXMVDSA&3}pt!v)AQ*?{r
z9?Z8~a_>xked2Ylaq$cQH6?DXw&GsY6`4LxGL%yvpUCpK*aUn-#4VCk(K>f#`x|IU
zQu+Ybld8=vIy@5Ra|#nRy6eUg3kx)QFIIS{|Bdpcj%T^L(ad&TfoS?>YCS}LU|U|&p6YG^0tSFog3a!gs9t+UL!i)AC+VH*
zueGP*7UzG2bnFD!7Iq|$P|Z2jXEJqQe!2f{uqV0Rg|U4V@GN5+Kb%lw=IV{W2_fnL
z5&aMzHQ=j<&Hq;Zqm90|69lXxU-x}!0B=0mw65)OUAo1!^A39@tWnmKO&rPE(r$Q0
zXIvq^;T$xp9BnsH`8{bn5l+^+9Xkc<-Z}BclWDtTk0|rDs_D2#)c1Ts5cW1QEJ`IN
zPoJ#Vo>v*azcRy?!{DL$&1>9c`o*01D$d6~6wIlHN5*3VOHG0vmEpO}_{}f>ZDdG9
zmN90i7pnliQBph3BO$c`!88K*J^d{pWY~ziepf>}82a_-7xQH_2Kyr>qDh
zh$w6^ANF1^%ifWKDfGWnG5yR=wzQ<#1zNdFQXl*ag=Q>~+N~}G3Bf5>V}OdXsZ45T
z%MJDmlY?3DD86jj;AWaP=N=vPhZw10D0hshJa5`3gde(1zj0L*Hi9XTErOi*qeoKn
zCSQD?=87ZFr`U_lO
zBd)XDa}?Nh_kmMclY>A2(B5fWw5T?jB1&KYbZnnDV}reb|q
z%Q1@*M=BiG>?`7G+I@(*DS0B_jV)MQknpC6#l`wd9^QVwpR&DZ>w*`rbT-Atl0|}=
zLzey~>!40^?Z*r`m!h>-)lmL_r}h1&I$Qhgq8!e_7q?FxRgXX~=HxBcf8g&7i)Siq
zCcbS%*z82PO+MKE(4o%(j6*-^VT^$BFWyGMIFX>E9>~&9e&cXbfs(EdU?7VG2`}5C
z&j{kWI+B@Ou^vGYR@PuD$<)=ZW*-0%nkhSOY?$`$WM!G8BgTMg%sCE)Dk7x*ODPW~
z+!O@L+MRH1CY}7wn-(}%2)id9nA7w%uBcz^XWmFuJl7d$))j4
zTPPMcX0Nw_HKb9+`UN8++ci_ugWUA}SV}nzoR3$J*!i3a{qB;dB13_Hrduv
zT@5zDC&6K5#dBzl*_`?%H^G?Zp6JMfilFhQGnM?_WyoyvI>l1&?bC&ovUfFU9i@z~n2wMD2&Ff^%8H*QC~7iNq1UyGXZl
zjppA{*1OF__6HKxR>T%Kn-gz?U2Rs+^0#A4%p_cVRpcxI$JEdO$L5zNJF%%I+rwwb
zX;TZu54aG|JIEAvq8Td^9dXJkRTv8N0J9zAnE+XVg5B=*cXFg9Xfkd7?;f<2OaIeo
z{hB>XUv5$GqDqwTh0X+?sR_BZe?gL^5i8OtbgA(uHwOB87+A>HY9u;>ic0=+AgV4W
zLSzr*-a^vX1q^&1)$>;s*&Xm{_CX|%8p%0`06=P*;mx-6B_o*epbFkKD(*7+p~c4V
z2SgOTc4QHu@dN=ka|8o8R*rt2e9F2eil(eUxt5LmL}?7G6q~z5!Fi95e~$D~wL03$
z21V88Q?c!ZJ(Z=Ts*ivU|5LY|Yn6k6L%Sq&SFOEi!+j%)UjRs=aBDUSmqCxZG!C5OuxnZMR
z76IY2+DCbpg};vy48$Etder8gD_gl=2rAQ{5sS9t_)}m-Yiu-8zj;=eFelhZu^mY0
zh=;YOj>DND!_+u3Ydq6#*-}h8DG)XtW#Z(+@#Q6i0Jg$~{q2O;BPP>vum)ZSl^r(@
z$VjI)gXa-0Uhp|DDvHADcrNd)@Q7dQk~-@n8Fp|S!n0Hp5+cnk-QrNq3)QPB$GuhW
z9qfAmPU#BuoM9vbu4~-dxgTg4#ILKHrnA+M&f9jwxlGqbYeZUIVo5?H%X)
z!!XHG+mPTXsUhmNEKIl6_C7Akzw0Yi3m~Zn*kuXYmwlQo?_`wgSQQZKqV>}MW-NOBqq58PJYK8KPYqVFWfP8;keTfAO*DZWk>i6zz92f=f~
zFWuJ0CS6my6#EyZ$NSapa{MC^5X9ZLa~p#8uGP-~GQ)w_-8`f2bHw8XX=H9I!t~BM
zJC9HD0h4GW#Mwpb3iWGs4cT!<3NSlIH96uj7$h;3uQd
z)BS|{(6DwherP&Gr3K!y#+mQDMWn4ERbFE^rJ&zI!x~2pn)1X?>L0Q!^eeUG;U@9@
zeSF+pu~|V82Z4$)I(ni{5wF|^Jfu+JpH8vtVsJKFR{2K>>;=hS@niCr7h(6Ld$m$A
z+d+)f85nNbX@Fzwl@@e6(!t;z5
z#C*vjc6ZEYu{wSuGF%idL_5RvJ*73BcGG-|$^N1xrX1`)+;iy9cLeW-jUW`|Shy>p
zJ1bNtYv+1Y$bwDNhv4&VQ0T-_uY6{|t-EL>B_pPv6J3P@f0i!ICRn#rKA%bj1LEE(
zOhlaB&+)$L~jr-p#rCVqFOMV~+965G4z#vT6!6Dt;IHMswBh1_jb&h5`6V6DOO
zV4^6)JkyHThn;4MP@U!wDhltU4^^c5U%5c68>CFl4JA7XN0q1m@2W}@>8K)h(TD|a
zhdSn_U(oSZ!`}~I%INC2Ugy^v(e%xTZ@ha~@Lm+I5>iv~fCl$H5_--wn270r{%h&=;|s09(St2EfMpEnNtxuOEEw1NtO(9L3AmkbBVbm
z`Q`@ju8A_lMky;T0fc}SGqBv(h?_c|HdVYLfLKu1V}wFJB+QLpxrL~MCvfpI>!sJ(
zFop&AR$;<`aMgTGaBWLA_xn#0_-n4NJ>W(y6MLa5%$0Uje~@q4;wssy_rB_g7nXZd8kvzO^EYDZmVBm00SPk7yhCtjHQp6!!9ayVTAQ!ki%;#C}y
z$52U1+&^8Av6ir>G3lNF(_W|)objqwUG|?tN>_^H%F&?}X7bRHdSC{60hsiH1A97Q
z(S$dn9aixA?qJb^u`}jaJOGUS(A~;FW0~-RMR(W+#^ws>Q8#t)?&z}sJ
z7jI>}(~Bl+z`QQ?7N1y*{zF7ACwux%u82Ie$4kb|MdBRCOhvxIpC*lbY!&X&Ry^6w
z0RB1yTQt8C-%fTT;8(KtL{=cNdZk%vr$a6GG>K&N+8a?2cPXDY;C@ahBOk6RO6uHx
zxDU%<6GtO=cq-75LI)Vp=MW7azl9O@m3g3Wo(O8X?(=64V^6amp|~vPgvT$%hqI5o
z($lgt++YYypi|Fb6Mpr1pw#1_efee{j6V6^%^SU!%xow$>Aeq3m1JOfYs+7opj!$f
z2Ek2St_bSYk$IJ4cx~&ic_jEm!*CopbWpbVw!ZSJd&Iul(7md0C*-aS4w6c-S)oCB
zgUGKT2Bl|slF9~fTA%Vn=_R&mp{7#Ag$wXlg)4_+$x+#mcdByF*nBeI4nZq2A?C*u
zUbuB9>%tw2CW)Cy)(glVhnca2CD(tO6DE{mTYH5t@o$FImU;h
zo}iPkI{IJS$EM(+5hg#N}Y>bOMKlR=8$Suxey
z0&@qRBcvC{Dv8p4!`rZJNfDv1b
z0ctv_x1>1g#y@R^J372oBBDOX_D)~dQvQ3o6kq?!3a+1)7izO(Jj&T~7RG)Db+&AV
z!?uIv2WXoKf++7KYil_ZUI2KfP4MyDq%KODOSC*8C%$M+(Rq7+C0yjbzSO1KJ?<~
z=EF{O<7bw$jGJAFUSLvRm&Q(zgZC=OXo>3dtq4)$j;_c93(thDLk67mIQS0_b1I@z
z1w^L$G`Qk!xzUwg&q@0#1c`qKLXS4djZi;isYQJFZjZ)8QJ4aOhCYkRl>bSCUjS(u
zIU|eQH?NIALBg|DpA_u7j&%L3v-$1!{B<~
ziIYU(%KE}Gpj>06ZLWH8FY{VCpM$H9(i2;|@r2h0D0Wx!?OTVfG`JPiy6ku&eiirS
z*|6pIa1G*l5BArx8DWA7MpNaK>L8xYbNiFDs9WULn%if
zN6uD67C09iJ~!h`+xuv~V8zz731!W^g+n71V$YAk@3x8Tu3x(|X#
zhuVQqwCu_&?U8_1JU3U|Ivaj>?=mECZ;lB?TmdltG77*r0<>;3@_G_?nvLkC1RzTu
zWqszGg9*hCcQ%v8SXjY(ar!n>2O5-*J+u|N^YgAp0%;Fl$#t?Ux7;YE0(
z6>SNJyL)jd_SrD4>b^3amuO4$6GPo?#1KwbvV_fkC4r$tT}J=7OBNc5kSJ%jZU*7+
zx%`OG(GGkO04DKg
zUf(A#vW&xf*|F|(>?Mxzk6UlG;xaeO_sBmln~TS(`X~%3_EQ&JT-87?MHZNNLPGoW
zOQ(XVg0Kyg&EoAI4jLW$$Z^zeB!-W+D(SI^cily~rH>
z^DN#x{lIr4Q0980apOg)dbhPVZy=Vt7(Eazo3hJ-$^54UmEqaLW(}BnK>N?usD%~d
zH5sfX$s`HDwz}su5su8BRiTdRRgC~}$!D~Vu&qWb!4q~TK%L736hoASMh
zzANH+oi_Va)`+?#lM}lmgX`37zg@nD$KK$9$sh@5gW7^?FWSV3VTSOJf+#h?=7;qi
z?QaoED1(=6$6F~;p{pl~op~w`72x6y?#rI1e**&vbHID_G?4Kd@ixYh!%}yeZ2X55
zN4*EQI5gDiIGsu;wYf16`gFm&dIUdEvt4t2lTLs>w(wfH^q3m~iN^@+*de|tM&{$h
z!|8$jkXuqt(evrER*}}(23=rsew8?di>n$=zEFhm>*~__hy!|)3qI0!-W!$yksKHl
zzP3}8K`Q2Q@?S{K%vmcG{I*DX>)JDN+$`k4JTwB)P3_CFJTKy(!b#^4>WA>9C;H}G
zHjzzAYQMQ@8cChko)RCLKJ_2O^lxUn7H40b?UGs_n}IbX!}kWthZk#OBt8BBFsXYF
zzDrW4)NtDCje~v7TdqrsA@tYNWsn9ZC^rKAQrGXuROhBos;0DJXc$7k5VwkvGg8JD
zpYkeyTQwfb^u$xJV^jquf!shYtakT`oIF85v$fF1SC8}
zhFOT_K;r7oc6~S0L}mE*mY0_>Lz$2lDj{PWyq1k?k?2?b=d*kHMYAs`DIO(cUoz72qb?u7#z7s1?U>TBo>JXtyBxv`0N|Ve1@?xBKUv>{T+rls=EtHa
zNy;Q}H0EAXV)^qGK46VJsr+_UlE-ylGYv270;;&b6&*GV@op~v_qC>*T}HfX8rp_2
zlZq*9?=l^i*?MEeBgk<)IQ1z&xeHkUdcB5N2CRvpYK?uIyESaHQ{A6t4iX1_OB%a5
zG5#oV`<&qmatOIe{S%y9+88cvWL?}VZEjkbabHE#cZaR4esu$vdrNm!->
zBER)J6k+nXQ~ojPdEHLlG?)cH;)e2x!p$1r$KO(oU-GB@x6n4kmcfQwFApThl__r8
z*9)iQy-Kpb=QJN@ws14#7Q--XW5{+2uJwX`E#*L$Sv0}0ku-{C(1Sa=9JVO;c5q+)
z0Vkg0&)mPag5AFc>>{~bmAW!4mmV>Y`;_-5Ysu??C#>wbxqLhysCGK$zq*n#KnSQz
zZzATmO1$f6(2=r-@7BqAK)2>#x>6%u05dH#A&|dsSMJG{fQ{eGgfNcSaGrJb$MB!`
z%%%JWWO+63TI*PwTjQkHlnbX%sbo@KVdp-3vVsFvjnha{;Z!E8CJG_N%&tow#J!Y@
zH=~FM^;x?8on&Q&=93&-^G->a7rbWuW;v-I-Q&8O7YfxhI|tJxAUMkmcQrhhJZci+
zca*h#z#K*|7#|UU)7M;CE6&pJt+`yw?pC-;mfk3WM33zWkzcAz5xlo3tCZBfsG2IV
zk117&|I6+Rs`U#^wbvZ0T)hwD!pWwq$V8&Jo8VraBHMH?qGGbJ&Gj?uG5_vG)J!jm
zz~P6Xb>kHX3u8-D5YgF%EFI_Xbs)1w?nYF~05yW%_dp?1%YWs$Sjbed-z2uE7T+00
zI(A1I*&*MmAd5v_be)7!!0&?h+KFTHb?>V;YToM^p6aL;q~NpDh-F3F)$6X1HF)G0
z*|_%uQwH9rMJ2_P8_
zdMuLKAZDr1FwjVx(x~UV$$3a@+ewSYSewC7xHSL&YW>EcVP>8%>~o?M^>=P)D{S7$
z^wE!Xp@gufYLSr2e6JB<1RRe*?&{&Rf-W%oTA)B16JN;MIzsE8>$FE&$TjT^*67fJ
zFM>ZqLyR$omk&}q|9p%%{9=Uz%jZEsSKmI!dWYHfR@$LWGQI7T*<^Gx9hK%+*ckiHQdEqp+gTbrMY}rmuIf3$p-nt<
z0Y9frW*JnhIXL6EmlYPkwwR&28ts!DFRZm^vQ#Kx$MbnJPss^DOmxxpq_X~+06&vm
zfJjb`zTTyL*GP|wfmoMwV1QJ7;sKFdu{RRx67fqlGhB;CFzW=!DckGV=;*#tc87JY
zVIBh%Jdin%$S{5R0rvj_GCbnZDq0!nDPK+k~nHDZX%&6SJ%{Xfk}
zQai-^waLGA2l2N#dpheTvN^%NWX)R54B|m3<&n@-Gk!`Q4Tp>ed;vn}|E0mm_6|MvEdP`F&4Ftgol)3E}NGLf&K{NH;p!XSllrrWsH6M!vb&T77$
zj~nJ=n$)&j;G}6HSZ(k}hY+gW4G4FVy0S*$%&iv9LS)VDIYsHc$~O4ZXNEt+BmcRx
zB)gy$!NAH5k&i=0Ue$3G)`6~V0yxSE5bxyEj_5S|u>N&f5wMEHy01^&wr`h^^b2Vx
z*#*RLJ?fV`b}FBlR9ao_9g*`7+)^5YOPUS4#4^`7s_;y
z-O^!{#^pvK)imXjQ8`syKq{%g40SOo49~Dh{2viP0%ri)l_kB(kBjyFrKGCJrEk!*@fq
zfA$RLAwYNXL;y~Ma8Aq^Xv^y+9K&yK6f>hJNaHbfW`24ZQj+|N-{xz>fJyG58crS>;fy+m9L
zeVlzZdIP5EWf8SZ%OK?{oP;;~%+SM47+&-#uRUH$H?q1WO(nbuUw_wshO
zmY%nh$fUVEXD;<q)bvJxZK(Qq{u1*#vq8-{hBkEMQ
zl_M?LyNsE{eufE?C+^B^(#+0}{mtlA!T`M#K2M0<1C^m2z!rcOT@cHo^Yqa?{HF;8
zF{0E`^}DN~57viz@=ZGS3+yx0XC>1GHP2d+B#jFr{c>*GvwA{wP7iwzS4a`#D-c(#
zEKE7P&_(mcimIrcg|
zI6B*En_SkR3{i??u^|rjFNwfMth^;6e$u2G&ygdhTYJ8|#EvRB$5u#X;7tT5H=2!5
z$z&hYiC}v>OI&?+n85x~lpP`4WeII^tFNmqt3>$iyrC9>VB4H1txVmrR#O0v8$6uE
z;KB6+$Wh;)-+VbK6DWr_Y-OAgoC#=Z>2jY{g2?3DacL`bQLAA?S`Cyib?g)%;tl2b
z+;PZ@<&<6Bao9#gU#_uJnhX57gt8apjFj&*m41Sz@uCR017Y0a0tqd#oHle2@SNQ!
z6Foh5F6um6Ql6Q$^z_K1;?ua%&Ii9*v1BiZ`t6aPqmRws1NE&xx!SR((cs(BasO~D
zuc30%*f|e5#%;1#2NIt?gr>V#<+ZKfCu}ld4TE&=-gxQ6boe<(SSC4s7{QaY=Wdfv
zV4)>|iFfM1uWVLPz}HwaO{07W3ACzi|N8W1D}Z@b_BS8>*rHoZuOHhLg4tKf6*WYD
zo<-`K8bQZBAfB5kFyRpKQVPb0TGt@k^GUIG_r==RM<(%dJ^3@y*sSH
zaed^I#u+%aYk{%n&xla95+?6I`bu^VV=G03eo{eQ^XY~9x-Jn_gUX$239FDIkcAD-
zMJ{`S|7(|e{glJV)crj|)Wd9~UmvaeJvaawMoUwe{TbXsDXmA$y^Zwu%BD^=SyNvo
z?>u$Hql#mUM;1lF6e&AF86|YpXViLt>NU1-XEtta&9t*Mb|ALC*b8}~>`^8`1C`4(
zp)i@?Yc?{wttth6g4)Vhxxh?T#of}1-bROF0293q-W1jn@_kh61%6j;Y)Gbk8iJb3
z$_{1U{w*0?2YF;=V@k6_spje;Y~MmlEwCX&G62|!i_!}wZ9C2*F+gm%#XDHexX;jT
zMf!yrrmlM0ltlb^wTf3S8{Mif`4d8xOpGHfZH!a689#m_wW5|@}VKhR4@@QRrY3Me=)268_C^tq$u{FaQESeiA<8F6BZ^A%_vrz;x~sdInB>j0W|F6Nq}#zRl#a=jM!-
z6j3Pr(&N_2-ZuT!qrjeBvHz#et_N(1vPzK87iH`G%|%pfsDLk2AqeQ?aTDyv4_utT-Czu34YQmCry)?a?NhoJryXf@?2EfO)S0(ju9S_9Q7l(78n
zSlWA%eG|?H7Voej?uc1Ar_0Lc0OO5DrUf7fLiS#}ErLQnfqlvonaZSL)M&oG9M%kcz
zdtKh~#aDH&C?3@sNP2?^CVV4sZT}qd--Z3=Z1HdF67>gjwW-@+2k|)iNiyStCQWuViaFXnBckvTuOw?*^LINCx
z(SMEkRx(kvlh7xIODu;(h!bUhQR(7(??d~5p)Su#!h?KTS8@O74~tdeRHUCISr25~
zqi!g-?k|cM>ZEnEuQsb~i&OQY4rZ;HNA;yGzaUuE>@Fpa`*Rdb-+?U{&&-HtQKCgo
zw0{Y69&#%2rOq@?xD>%KuY-91f?zLWY9fP)LhM2eCU#TsvMMs6dt@^j;Pt6jH_!9r
zXz3LH9Em=C+MVi3(*KYo$uh?usih!GEMJ?OreT~%TvDwhDY6vz-(lXCX+&i=G4+aB
z+HZSwscbyG;_4oH^xi&(vicm
z2`Bzi2GZ51h0$t%8Wf*Y{D0b`#Cr%nIl*7YyCyI4#r72dLj(IZg#Ua3QzxLpSDZ^k
z{`3T?)u{%T?U!nL8FHU>bBEO9F)-mCJZ@V(_PP4N7`ET@1l5L$V0N*3y`=BE_?>p+
z#AAxO1IMD!Ozdb~o>B|KYoKxRvD-AHO-`S({eO|L(H?ahdhF+1n0W0rkwJgFf>~~`J;7(-ZU|2O6Xo*#pDv2?@zMG;|G+A
z368&HHnWK-!)UwebA)nd^xXVI9os6uM6a%*x{
zR8XDN_0BmKBIyXUf5AjU8~vSsA{RGRtyur`7~laEVJA*~;BA`ns~qV*IKb!c(nxe{
zqsad^3KAiu+v{({v7V-ww)>yzoNN$W^nlmiaI}Y`;r}Ikyt*ZE(m2v0JxGuvKL5zR
zRhNiSdjm`0R*g>{!80x66BBBwO-kGc;ZA!*!4&IPj_s@6f&lljbOZ(}K_{bVYjcEp
zD+~-=tkBVR;hW-U#T(7+1XwpTQ54>*`};zZTILchUYY$T1kDJWlV^y;qfyqlye6D{
zfNN$hMs`0qd$X%>ikgDd74(=W-4?`2DgzN0keDu_GthI!(m09kLgnWfFauCQhe{)+C4s6boIgn_gonx&wivowtFn!$pe>*
zWiZ-A&Aq6wWbK4lP)U9cZU%1q_;nN$diB?Mmh$|7sn3R74nvrzv+tc(zBB<)u>7s@
zJ5116FE197u3QbtnMf9QH^!Xn@n9L;vITF9kUO)cdscLL6wJmKqFpIWq5u-q&ktTSRLiqUVkcM=g<*=
zi)xf8$(X&775cp%VIf+Y<&GtfIaVyvEB6A(a4D!{eA3y%Z4!Z3P&q>+5Awgm@_!kt
zf4`i<-w%^pI>A9;2=ZLm(B|qi`KE$%XW;&!-m8u%pP}QTo6GAEI*x2mtRY7WN4$t5
zKE6B8$c}Q+f8|Vl2n?+2TGyy$GQ+<*~>{
zNNu(HBjTlZX`&Mv^L|EaIle`K3cFwf8jKcNVL;BJsEfJ@1{;7GPw|=D-s;u}m*g+p
z#95isiC_9bA`w$xy(r^#3E}!X6JlfwiQ{Y^HrIJjSFLS!b1ul{l_*5Vay-1SoYV+)
zxF64^`W*38DRkxo?Id`KTO*fHDv{VnvmF>Rcohcv7SVxLF#aF
zB~hgeI}d;FOmDIgW%aET(VjjcWcl-Q{-QIBn7jDRk!rz>uilDyK%W!}g`RXey=JM_
zp*5Riq0>EOj%K?>sOk0!{Iq8w-D{$Y#kX4g@$$u0Ds4SH_5^TnR|3x=Xqbu0$Wq4=
zxfDj1EfH(tDO$ok#ZQSOB4Oj*KtoFPB7guUjAv{*jYydr98iPRCtAGdee6OVnJqL~
z`p8CG8HssM_?OD@YIn_#^y{WdI7J`K+dQ?#??IZnFh2R2fbyYTO5>INfhAt8GL>IC^VbFl4uW5Sn!QDerb*V=%
zoas7p>U#Q`b&6HAU_eS|<|HvM@lxfEK-sJ~0WgK(l@!TM8}nc!523kI_GtTz$o^Rz
z>7zq$SX2qDTGV_rk~`!o_g3*Dz6;yt?v_?j>CakNrsTl0>u`K|g|Whr&*{y+;OE3T
z^_Zi94VPrBY)3=v*bY4-N1w?|M3VeV2<};$D`f&*;0vQ;Vbl3#0ZPrGRD#!jM&xL-
z!!~>nxvvkncHmVseCQvdZ<_>8F(-weEzp~l#}&<5%+xB2>DI0z>iTp{c#J_v%=-U$
zVr0W!Dtdf;j2A>}V~_c=ZrOjC)r0at^qf%8-Yq^hXU!}z<&H|k+mwvyQcXfJdp}f2
z!{(A20dK*cK4WsfvPDba2S^d*lb)w0lAyeqE~z5eAO3f@is2#ZP>*Q8u?h=iwn@_{
zi+76n!{DrrrATN$uW5dc%+&wSGXcb93oMeREfI{yp;lBDbi>tZ1Rb%5j+_p50J{?g
z{%An5tH!q8ij@L*CH_VLZPn6t^6O|J**InyV&mbYjpP=-|6W_;n4!QC0<&?OJRYX1
zIB{h!2F?+mws+3?ho>$8uK`JYN9heTg{>DSw`gH=>K7T9@IQ|imA6pCmjqpJx7ca8
zq6~KrZ&Ohd-bBeskEBj+k<4NxQ-im#Y}WfYuf3dOf>S@eKaKT+qa$6C6P}pY(TEJa
z{V>|CsYPH%6t@1PXg~|(|H|~b|IgRMvL@z?(34fg9i7!H4|cq&;?ctX5AlnN4HdRQ
zIWnA<#riP;Sb)q030$lQq)Y@;g-?JvRii-5{iu^Q!xb!F*rUtrqkv5C+1erK{SN~n
zp74H0X;SPyVuT`$SOn#`HT8iu?0^eRf?lj4ACz~=LpiI0S_vE#ma<|PDR^Vo~I?IY=f4zXWngB@K9T4YQds5Qis=hKDhG+)=O
z4f+)*kH7={&p0m(jsmThmWVW0PnA!W-&w32&m2LmTO9NiOcaNA1#@8zCq8m1$TcYS
z$TRmDShaEfZnxLN*?)m}5&0oYbcQ1eMhrwLsv^|dH;U95pV@`C#ogsBzOsBz8%~4N
zjrITafB&R-hZ}o=ofBanxoKIrF9%z0{3*b|z|CgJA|%cj+n8+ed#6vLbL@8id78(-
z_!yXbs(c0oRY+g**ih?6*9I@qIlLlbFPBNQm8NEqu+wQ^N-i1?R!F-*ZND}EJBGZ^kmERP^KIHzYN}Qb5<595}n{k`H6(J
z|9`Yd9%#J7jYmJKL=RPJ)%%`$S5J>i{=kbzoQpM*Jj&dxr9Qh8^lt5aAMDCpoT=sd
zdl0S4Hm$ZXd~x|~dsz-0TVOV^t0YQ2@3z>ZA`~ZCPx=R|Q@(e~SN_64Eo%&UorVN6
zQGqSs#8!ai+4|?xm!*zVEp^+xt;Tdl8rS7oI`AvK#d;gFJ7LYQ4$^I*K48&dHTc5#
zjfE9x0-YjtD0J4h@X^bh`xGD2Ls56Q!q7pMz!Glc6+X7~@i26xBp>ZScK)1)qz|1p#HIs
z6WrTth(@9vdk?`^j`%jI9RQa%LJx$8mvto47`H(-KBk?-eHFh(|MuL`eMsbjkZJn{ieO85%l<{VrRGz
zM(G~Scakt8TnYC}!5Zp`%fhmP5mZQZFT!Idm&0ox?7Ag;er9oMh(;5cj51=KMTYvr}$e2#-wiEsyhQi&9$ZCAac5`1zJbxNyK<)pN$kEjgA|r77-T#U0
z>WO$)@e~=MqA>;v=`S(4gK7uIhmr!0VNB6wgvpe;U9@ig-0GQ5A`>Bop5uvJ8Vsu|<+yVwWO_oVJG5iJA-bkk;KNDGLYkv4cEIiEddF0yAC$ovWIl^mpY
zxX6`F<|;U>lfhtF@{!1um=!1#j(U<_WAM%N`RODnqDu`8wEez;++;ckFDpk7
z;yUNU70pJ^aSkJ{GI!zFIiwq>K$!wVlu(c%x%9A_5qIAj(m>)BCiEsh|LYBX&rYKS
zMr8q~^w+%(*GkewFAxe*bJ3);3+pIBUY`mettlLz5Kjk1GkGG-HW{F;tGDIrB9rC`
zh&QBmZYef{8%bZ18D!=qS*qKcb-ooNwzL|uMo~^CI%~g*ML89xh4L$f?fBsHRgMXO
zB-@zMlzk)$q}ABN%T!ObL~sS=kSF$uCu`M*Wz4(x@^odu`-Jn$bABw`W4sI4ncaYj
zTmJK5O&uRV00(XWCO@2z#MXSotn(TVV@6
z36XsFcXXU|`yQJ$3{XmreHqr2pAk-d=!ay#zYSiculJ2rrTVF)rP#{7B?E`|8*0J?
z`xj5|iN0Kkc%4c+)Q)QmKg88z3^m<^V5{{VlA&---cwQ#zv!SFb(`AR1hICC{Oy1K
zdy_xZ4f?>U7A(=jh4GU;1i!M%@PF5OX$lb!6u~8eVhl{l
z4?tll7ql?TqidKbE!d$T`f9xvc!YIuJTt$|I4{Kgn{XZ2w~GP|fO^aCA*P`Wzbj@v
zt3k=ZKy0{WkD>aU$h^yTGI^Ut3Z#$yh%IsT~mlLT>nPsVldB
zo3>vEI}iiTXmv_mrY^lH0yob)iEHs^k2eR$6rq{StxO&3|
zpuh5i`OV3mWv4j%WyP8XkTvczlSPh+xc{4J(Fdm*p3NRFcN&^KCPA|Q`%X=aH&(=0
zcN~Qjn^lc~pxN}Fu9v8Qm^qdnKX_7|UIt0wDPr~TFBo#EpzpC&0l~RC{&S}>U%?nq
z{fh@$m9^I9#()2Wf9HgIh4{B=!$jjzk$L9jSWLO2PK}nmoPG&x)y0mRIE&Z?|E{Uu
z(*4v0=T#8TU+EmLGNI$a1f^QPe^2H8CRKuy|G+Tdn;Op~GC2@!|9rJj>uj4u^;&5%
zET>%8q4Uh*)2%)yL@07BF*)Evkcsv_nfMo&*0cKdhM-;A05CrJ*O;EuE#(k31SF*J
z@5t){QjtK*DHj#(SFa(b-EgA-fz~;*0}84=<5u#a9rf#dTTua5=jI+qNc`N%BLaE80mFv(
z_zf}1odXA-`mVp;I1&G`PPH4j5R)E{-IIrw%rr*V^XsaY_#^Sx+z$^z8`Qa!r36&i
z9ai;Z;kl&eLceeS`U;^q5WNi)FizrAs<1Wrz0hppZ7;4VG(3yMn|Mh-R=xJ73Nru~
zx9|gqE$i$My~U#sx8x$AZ!`3f4Y`>sM|UNuFNjkG
zH10oW%yM63ox#;un|(PKVg;sHEAFX|GI-%(+ZiYZ?s$sVF#shd61YS`HK>YXgKcv;
zkT$2_n71;^!JFKR#%!wU#&ET*C&;T!MIwj#Wp@kbEAb6dgOTf+4fE@jbP4R1+VtIN
zh-4qt`1UAis&nIXM^H?rA+N6LsMt^WcR;gVR*rrbclE{8&6Xkx9oI%IilF^_Ro&sU$@6>XeAAs9;B-KHVH$aRfZu#pXDn
zum%g?mbLKd&t+ljFsDTmicZ!U9LhDW89Ah}hJw;ML4fhqX@MhEQn_i;5wJ?U7c>u$
zNl`yNW~K+DD;;|NzCgs82;d}chnb99sJ*a)w43?I%RH*>d_M|@=dp22PH;znQ~$kG
znZ|Q}MCgg2i&(5Q?g_V^Qp(BUMgg3!?q?%sX6+l&d)f8Ee*do`*sF}aj7zy{0b5!U
zI*#?jix&UHg_AEsl*^ETCs=pw2w1F|D�H_I9PvyZ19!f22zd~2n<6^Dp03?rK@h>*M7dhTp%>UTcY
z_V`h~4|iFn^@q0g+nGh{2<(p)5~E0$aVE?F@j;dfNWpiwr{kUTNA?93gCYsY06P6w
zLQ2rdeIWCpDPS2H&egU7<)KNoVBI0xcGpY1;(V2HNVgh=(hS|E9Qx$
zBwnqCRuUPL>Ukk03d9U?q+OFzVMc4}IkG=-&bB$G(gih_^&`6vd$5#$JaB<={Tyh>
z>kK#H>QPayEw4b7|1GAP4XzSx$>**D$}5B!d9Fb#2_!s8qR}6zrPpH>j4_4>Wtuan
zrGlX9&JpGY<*(!R=Ca7E)LPxI5xv0zUwG-GjoAJw4=2rz-+GnT<|V^|cs=$8MSH(=d-00J(BJud3G(~|#tqfCksEw5_c7s>uV?=otoD79o!
zJUfLjI}o%^k?}WGZdZ^MQEDj*ou-f9$2x>+-~bny{o^9hTe|bDyeS!p>D$gkZYm>L
z7=Ke55(-Qa!EQZDF);&*#u)`t
znfWlg6;pfb#1FS@94VLdp;~r}hNSsAaZ5vScs5aN-&*XYT*1O}Gb}-}1>>)*ZdK}~
z^{tWMvU5ZQ4kbOoZLMn!J*;JpVQI-zNmu{tqMd<={fdenlS$`0yM@Qzk_`S3I5;7Z
z&wE<|n_fyZDEA`8fvGe9{BQkCnE&yCc99t&j%9)~zI?$5C4v&C0dYpE8`%+NG*g*kheU|-k@Jeb@bO15-*kpiNNd89RO*#w38r}(U@HK9s`zo|Mt
z21SOZlB&s9*hI0j0u9d8Yqr1cI|XV-fp2Sj#y*<02+mw121hK;ftpaR0N+^t3hCK^
zed5NmsbP#XDCf2yIMHk*%C4I%@I^$X=b8Cc|g?Z$TH`JH0a`*f7AT
zx6x$NqPFvE=R-A3TidyG$*H3X=U0UPy2ICZVlr<>B|2)AIU-}G$S>I+tqXd|I>2n6
z6#Stsd@%c~t<9nj<`>Iq*
z@3b#@s`k+CuLe|;dv!53d>LaemzAq)rcQqw8|&Lr`}v;2x=PltMX=ZGl82M(*4><)EP=#Kw}
zd@VU?J$?Q$1PS66D`T7$IxItMtoDEQhPBLF9}EAdKlW(&-YOiw&V2+l;`*L|~n<
z^RRuDmbY|sxo@I^!`t`RiF?-OeK7a4rLTsH6$Ud47E=+%I?FikFy0M7^*yVuet{-*
z3B(Zu*u4bH`(Q6nKW2mTq)BIsIDz04d(@~~*T4UZdx>g^rTfq{FJg3J_+;~8o)6E-
zguC%I-bkgLsL?1Y`H`O-F6SbWGET0Bi?wgdWXriU2*dE(RGRrIC4<;Z-$5-y2fxRF
z%KSPy@AMi}=GrLn#_9A+RYf@YIy#ON;`6!4>k~3Z5RVfHPwXQ0D)mTkQ)Fff%Fcx`
zJ@VV~L=k=Ji=qAY<$87(s$#Z`VEA-pHX4bxJ9)qo!DgC3$kn`0GhSxK{8u`$z)1&J
zqjPcETSz<;QgSRVJavqu*Vx7UmuZR<^ufID);xuL(TohqpqLXalW%ss{fY;dwe~(hM3N_6ks~(PS3(~z;*$=F2PMiQ#MgMdvkwE
zGy~2GmG5{1j$*vL;vNamR{C-7El6j5F^8mOOsq-==TJSBQXRiZAn>6wX3x49@c;yxPp0S=Zs2}@vw$w
zc$DlaBA{d78Mo6Y$ta>0y3>z@<@ib=%pU7sA1si2yCnAf!*rfW+L*VmRnEGVNs2F-
zauI&S%)=&y{}+Pi-9`?c`N6r7vjN
zWmRuoPsucs2uuDk6n`A#M(>jI!KKE*Z`W{LgDa|
z)^=(K{{R2~C<8}u3+Yjft5NpBq<6#6@aJQW#Q}FHvg+r$0C&CGoM8TfRSmdDtekTo
z;lWwxqC&2nxgA*04WCt?wM3x}TI#=-H%wMkU(s-#B>EzQQVkn9G)xQGFWVntmv2`k
z#k#+%=-HiC&HYfW!O$3o6W^5A7dxNFQrmzI_{a5V=bgn4_`eD|+&C_~ZxDh+n#i<&
z_6_l~{y-}kS6+Q#GZnTIRxHm%>-pljQ&EQtGDf>F{`L}UX_56zqc<#nAf*!992%f;
zh<)#6gnecDvo4dxD)}eFeR!Nk)?czBG`HntgZ0OU|8y*t{l1CS90s4v`nn2Ravv)Nnr--l1O#o
zy4XW-fSPI6*kQyKb6`&v6@IAwN>ct~=NY@s2C5*v`D-CAR
zr@h}7s|yF#CJ`GFG>`VaaPU#Wb|RHhzWDyuAUcraWF3bYrtKUFWwalmw6^1$BN{fa
z`NLh8W~ulQ&5a`{ouK0#Q})uiI|>*AfE=2%UhW6xPR{1FGt?VqfAXK9mtul5*-b{k
zYMo~Sk%2D5hLa%OIJOnRJ~G{FlvE54BWAQaVL=&Bl8j$vLq!4b`}{iKJ~ZSUmCwG4
zN`xG+657lNK7pVw#cPd(4VBdL|CaZV$6aZWhi>5nRy|&3kJ9W6f*P+pZbIB5yH=D92%VZO#
z5qOy^Ot^eOc*&Y>Gh#g72wfk2XmKmS%afUwSIFI!W-LJ-feD=69m$Bx;cj#~vxJJ-
zPY~~ZgG5PbsoET|FsvM$rx@_w*`JjzOZ=6AJk`9!)9FMavh<*zV1D8#7jxbS#j@8c%9!xRQ0Mcmvvk(l~$Mk-=&{##K8fW>#fiKp`F
zCz0c5oAQoC`iAYdyLQmO?f2`-cp!86rTdVTn5nupE-`BGRA9UVX}XCH`eDGaGlDRQ
z;Q>o+=`E(VG&7cz!S^ZaD7rP;?CUReJ{bxscREVq?EC;F`An5mwhkz32Q#yk13s7lgWBWV)1ujzH5IwvD%n&(ZB170cu8F2DnO{jvM#{p_Va|MM
zU%&nFWSxkhxSg2&R`;jMk!6o=`el||JJM>#qp-$6!oRB5;zK_<$(pVvrfx(rboO0}
zW>%@Z=D^&HJiR)6xD`ut$h!_Sr+8x#uhI>9Ic;%bCtH9AL-O+wymTu-9saQP3P!7ds
zWOL3~res_n^bN*TspiW)rDLX3-$B!b<{`fwxwl8+&?uD?jfD+67)gk~!i7@Eesg!p
zo#4~7=p`EgX)St!GH|awKUa{5QBFyz*f;EpCEub(dm)BGYq9_;OE*gLFDIyGIU`1ctG|5vH
zN0~x-a$;{bG5zg$w(x!mn@h!le%#U#Ub2Rwt5YexJ&(~qgCV*(C-eq#Jzaq;#Ja=3
zV-tZ*w&^r;BrZB)B(g_IeRwP1e0IGBkHgw~=XghafL8bGL`n4>BNZ5rX=@5Rk{w8G
zusLI3p>wE45x5+B+DS!+Zyo&7p9NNf{a4>`$*@#)R>avgr%7?Eb1X}t3q6evu0g8I
zZs{qo8olP6OGyD`60y@aE7*A*@K6z^2{$Qo>o-C!*Q;$(21if91c&CM&_gEk+I)ED
zo@IT&QUwN5zH`0PMhO*QWx~}073l>}v``D5Mggwa^@1eHfxpw6p6la_G0!+3LcT3~
z8L}+)Yu`WZ9VIR-p0{pt&pJLYs`g~J8J88#T#@0#X7#FfG;+r)pR|J9`t75GGk%w;
z8O<1j791wg@xBv!wyPW$JtL(8%oS>>GS0q$(#NaXcEFX-!7``i#Ky*&hq73qs0F4|
zg~nm^WUcV8$~ob~n731oOKrb@8%F9o8b>}QoI5lon=vS%*|JHV&2WSlo+aw;mk*-v
zi}f_)ZwLSkkZ-7S?6wuzo=8p(;$d8ZZUjjL!C
zPL;*sn~OEqN7aJcB&Yv-j!Z&_dX`{2Pc(LaDVpTsWzUYf=?2Q7+TZ_(6x<_l&7n=JpRNxrXWkHA_~x#${eYfOA?F^`=wZZRSgrHa
zRBzwqX*D!mPL@x9?J0Lkae)!vL6iIVLVx}?8H4c829T+1cg-4;^6sjo;2ScBFiqb5
z$v^U+mDow>d7;Q3g!$ng;vvhl7{_2#4@ZL?-hOSUn>R
zh9tw2jTVUn#WtK)H4hu?{Mid4-AO*Zt-MAxdidZc3g=`Bp7e00og9VB+4uLq4_Bbo
zEQ+E>0=3rfgi;oC$h2C!Rr5KRc~td{pSn>7+rtI~xQQICsR!r^nXbEc-`z!vaU6l;
z3xLC{o~L7ot4~!jFApm)8VGPcK&-VBgT-_Rn&l7Tv*(!Mb4yXv|1_J)0ZP*E-x
zOv(=T_Q2~5+8BiWXO+pTJ2>tGo3>?H!0>TV9A>_6z0v17b@
zpq>fB$z*i^Jp1Q`lJb8~L)(~W!H|*5?cs;jv^bSP-zT+~+p`wp=uh&GGdI$Hz%c(2
zhs2M+F?zXBicl1sn5&ynA)BydvHX%OW5P#jkY}3$%-xf>xfH(F<&9!{&X%8^0H3gn
zqm9%51eCWSa-8y;@51&i2&4N$(3*d>9tz=GyW0Y{>-g9;H_hk7-j*gu)xLNrpe@sS
zR>mZY?^9T1i&0wV19IhxWN*Zg{F<`L;ObU();Ci%7(3Yv-XHFez`G(0@
z92ZCht7IRyAf~#*c5uBg4k*+CFWD)3y)
z;m2SxRJLCr-y~pY@=xEJTM7LQ;Jpt?e|jey`h(^wLV}wmP_#Sm1?MUSmXMBf}6=?_NXcW^V9z8^7)D)-u2`dBz-~
z(Onp*$yWa>=|5Tnb8Lv`K(AzmbJj&9on>|$H^mL{J?-7!5eOq#Vv!*kjxJ!6@X)5j
zRh|18BFWNzY=bOqh(ks5+1r!jPODSM;A)24tF%OIukUb%>T(9QaD+pB
ztAs2lI1sJjbA+Nd=uS=ZPgL_><2uisPXE1@s}oxYvK4czyOxZXtpl=ji>i2wL#(Hi
zLRAZ^$Y)-lE
zOJAF2KrVgq)WCg9&)dmUk^a=~)AG)F>W&=_kfqm%)1?!wN@S24^g2k0+NRnNy5h-)
z8jX7fgFl6w>?VI~$bXDrB=K}K(mQ*MSH3O&t}s+>Ul-)+RaOR~r@l{Jrugz{=8Ww1
zG4H>>s8-6UQ##Q3;g>JP6-#+U);8
zME!R?583H;qp<)C>Pd8x;^Q#H4Q7ZiUU>)T{>*qC24PLH6^L31=euj9$DC@E=}}dv
z_rk&f=*5K#A+xqdZ4r$=ZgAsE(#GWGV7`n@X_2a)UYDUL=Y)Sb(R#BmWG0
zb}(#7dA@}MwhM73VSLB~G$na^)5uG!aSdsL9%_+WAg^c$5I9|9ylclXpVcl-ed>OJ
ztV{uT&d+vz%5vb2{AdG;c;q@x$HS583dO#iMNbRpn2O2j{_N
zY9@T|0re={J3G2u4y#<^$yuD&Skg=0GusR?7s|$hw9SF*`v-;milSihYhIQ4rn8MH
zb{~4LW>kqzi~ag#@`8H}Va4Xs-qXG@Z^ra
zH9u+xv|(qi2g90w9c3MA+9~_4^{nZ7e@;8TIQPta6B&)YgK0Lh>A=FE_Y^<5+hNP`
zF&mzT6%fjz?1VH4?499~VqzZ|JP@^2K<(q@Jla1QM~
zhEH4gOd0%i?DUH*ym&fykYzO19c^46u*qp&<7)AxwY(nHAM+@19%jD%zJ9a0OkN<6
z2w!a22bg&9>i^Z)|G{BTA`0~5!+qkNP`ctoQRF*+3TfNkDc{O5@#HgN6=N^j_EjrU
zta~e12mfTRxn=}LzwFCDpwW^6`{`_~*+NL#4$ok(%~`?v4{oW$M#`D4l@LyZTk}0H
zJ8CAM9(2&DUu;8>srS*BH|Tf3eF_C4o~X-MMSPRl=&*xA({NY+BJPJW_;ypoa3qd!
zuV{YjQhwNX>pDnbXD2$mK<$M6lolM?!@r}r^pNMrZ;meqF%Q#`KMi!BXZ_iXI(0)!
zJW(K`R9-KCgD>RX3QzOtuv8smPB8#eK&-#bX$Jo^q;5Q020}gc@vET|uSNts#MQ@Z
z&tEvA3;`Z{yb?ZFhOc!W`j*m*TZx11{JakaxlXeD94Z=NA};riZbKWgc@Fj&)y1UF
zb3YfhYH5tu8r^=rrMpP&z;0S4rVwnMy7#$BNG~hm2*<4QTv3fL@2K*JBg73BGC;U7
zga7%Y5nDAng&!zaHkok(m{IIX&C$RO?$2tF?dy&h<|%J@JvS>9Hyg7KU?liVEc^;s
z4gpbjhWx0KSRyT|266@YJRvg>P00WGQ}n#rgQF0OpJxA8nKD`c6SkxL`0#&GPQF&L
zqAB*@miXfMAy|fpFv8=55-6hr#KwsZk$LL5wxKTzPyZwu{#V?Z!CM;j^=yThG(v2W
z9`JOZkTIH^c86PpSUUXmTMSi+bh~X>S4{U|pVX(xzkUG2c4miFT@1@xD#(s$w^&;2
zG=_oUMVPxVsCKJqP*D0DtXtGf_TFo(+Ag}7IMxfeGP%j8rXX*K?5HN~QPt&a72e}C
zui2$gaOP+T@4Hyc(ZgaA4U3GMjE>a?VN;8SeFS%wBGelx(81K{=LyKas>daN7wNRh
zl$C>i$vj6?E!fWMeJWSF-t-TE0~MeBR7FUiKYE29Gq<{!Xh8b-MhE4hUR1IVjoQ-}hX_3b8?ajFMy!T-HDA>J$
zKpQH&6JN7t=H&bcTPbNTtmM4wrtMe)2c
z=uFw~wQqe?WTU4c8?Ku-tL=!u4M!+%{nnImpiPDc&yo)xM@9P4b4oiYibX)({7p!w
zvmQmSU$|^>ROmn_w6V*Tau4am?d~eV_iQ!r
znR36K0yOp%;Vf}_7a(q!dZPaIXQKB8Z_$-}7fsH+yGz8eBv$^JiMuiN<@CI{bN>Ng
zu9ogTQ
z=Fy!KXF1*8!q~;&k)?qD4MFdJD7(BtZdCh9%?_QC2Dt63>%kqtT1upJgOVzRE{mwgtJ}2
ze!nj{qvE0}QX=3W;yW2lKB>k@+#y`Y;)R8@dJh=?+{K`N0ZM2OB9Mfw%C{jOJ)@eK
zT!Yq!enqa4~~d6)%MeD%F9dIqjZ
zey<~}q*K9aOvOR}m6)l!Kh|A_KfZUHss5c%_%7x@MsV(<3F|sV#DJgXxVc+Wxz%0=
z2iU~>@@<+^wGrPT6;ixhB_tKl73?!~W-T_ayJYFiWrm|6KX$
zhk`OFMaHvkv3%f^UZ()~ZsA}9Mu@x};`9^+{F@`zc|w`TL#6SYTt1;fj_Io_k9h^GURm?V4poQ{qEMb|
ze2XaJ1!WOqyz``x+aAo<-g7@kOaixt=u6~?E6dLo4JdpvBIDNDJRW%}AMpDBGEt^B
z0i4<=HhjmhQm1C?h{L_t@1yJ1|KD&OhB}Vb>jR)!BN0ULg#!>^FA06M@4~>PT&<8^
zPy=x3WYuJQear*Zvs$wn2`EjGDL4-{@Qgx!A!L}E=6}%*2j0iHO-Hiv&aT|MC7@*hqHSyvmRew|{DL
z5}53YBEs=Q;<6W!3$*;C*W-6CuH0ak5>ud+AWI1oFl0rxn8
zWf9~ejHP7%2JW=y!z^GdZ#(eh5>ij5##S3cpI!+z6Alt3I3cZX2#Ec6zN=(B
zY#r0(7`2t($3yQ&>x0hH^K(MV00RF-RYLm|1Uf?Ac}jIB1|>Hd#W3%l_ciN9{bFo?
z*BqG2=5kSB{;_mk6pcGFCRHmLZ#TiN3cR)y;Bn~hrtuI#IFC{$UI%%8HFK>KA6M1s
z#tQxzeHHN}dkA@#|4E0({da|+JRaQ!10Da^AtcGD*v9O!pNfFWyh-UC=HLbzn#W?l
zgp{M@FhMNn2?zgD1d6ALf3J;>jx(Vd!+meeqpNTbtg8QWZOBkzJQHC}E$w~J<<(b3
zU_9M{nivj8_$gji&aZn0Nqj-*WEBSF^>(VH01&oJW+F)JHO?x`Nj66TV3YitM{BIq8d
z4`WVoL;vfz{ANk3BQD$*JjW^*>tVzHt(hG}n)MvAuBk!AKVir0)E8!)nEgurL^lgP
z>)KhRJd7$Xc%6q&{})Bxr{EcY2MCyu6EsY?1M6J6<A5q{XwG@}g-0lH#rpKySo&>kXd97fUCVoYZLSSFKy=;MR9GBw7(czvj&!Eu~v
z5nnE~uj6xS!RRUaOt}n#9!jD9BGb42#S=*vYwW$A*#}k4>bxwxv7@+5YB!uppQJ=;KVUEW~f`t9!{b5JCFpf@H9(t2efw@==~!k>#k3FlhhI
zY+-tDw!f^kA&78KWVAXra0CzJ^Us_20l+_vI2KebN{PF$#=a5uIxIym_xdA>>LeN&M4fai`_J3*}aohaZ6Uxo`wUr~VUk|y&tFl8}*BQ?0)*iw84K&|1cjB4+i?+wL=9Pg5o
zWb5Q;T&PtL2l%~}KrYQy|KzDltd{cg-Hz4T00tpCzy1p)RUf324xsu^
zJ5<=<;N>uawJ=*_v4bdzqL}ylu^WgkE;nLOBvFTu}LD*
z{9Qf@8~Q_&OON6-ZOY~uC|JJAI_DvHrfV#aSn1J5Crid4&o1>goJ3RZOlh!_+At&A
z2J1NS?qiktWj#hqoi)E9bSES|2e1yFRV6OIqYNkg78YPwjfVlj?`@{D5zmB-V;7XNYgtm&&mO7i%5#R`eg4q+a5?HbjUPyrgXi4QVo{!PngcZPD}aDLIN9QY=Ke
zeWInD;!n1G!1?*#|8Byb(+`8TxY^NgPmd=s4AcQfjw-OwkIZFYxniKfMPP@9HK{lr
zvNCH{p9YVfg-QZ`liXZ#$4Q@wYfBRzPCg2ILKhbri}%xNn#QqKM~%+nS6dTQ)yQip
z|L1UCKSqCZBYU&Z0hO~pk$e+k?1d_0F0^HGiE)*NP);1`oP>^`6d&+9My>eWh021b
zoK;x7EE998YyNThoJ>V0(iTt4R4Uz$e%lV^nqUBG+MWIb7>hKvi7ov&^Vvb)j*yz~
zwgfeLmJN579sj~jlbbjUOWkesL8&mfRkW_7s%ZLIv`4?Hcp>pLGCR%7-Xw+!Wj9g3
z@9Lq{iYF@>xW^KtBJG+z=U-moJH$e1WBNt4;ak1vpf|bt%1fx)
zM@H|Lj_W+ehmdM+Gz9>Kf?oYUr^OmDbCLvOhUv)A-PQN@5!Mz7!r?fYO!6kJe>sCN
zDUF3%w+lBd@2i6MI_=~WSs^!jR{6GJDxk7yvpM6cm45*0zbm#f_Ad0aYx6SJd&B__
zazZ2=;A~~#-z>T3)m+bDMZnQUAjfOQA)P03h&vA0fXpZm;`R>wT)GceSVtP
z{24b~xK)Mzo?I_{)P^HjjFvdzh@U8hbNw}vwaG(2D?twq=i~N>zs2dWBqDo~dX-if
zsd%#WhD*;)c$*hx6PFtl?TgNzm3&|G&ymS3;TjLy{@GH&NK}kLwnQgJH@6v?iQ?s|W9|?T
zZ37#L)k54+B3*6@-Th5w3epki`~N*Y^!Us?X$q|5F}
zA9O7?aWHVQMm;PZzAX%>v3M`LfRyn0Ztq+9)uexn2vkLG^{#4+1
zE41+9+=IvTXpE~I-MS2E)(Zj4au`Fgg~F=x(=?HzgLbhlhhp#irrAslP97PN
zLyuPQ1!UltFA&9c{Z#Q9|LpKO$sRg*ssn7y#0Jdr(j2)8D(^NPL(v3Mw(6Bhn`8iA;#^e(B(8~>%rW3
zWFC$7b4NQz-W%JG`+O1C*g}NC5LFZ5+^BX$g0+)Y0*mwoEcU7
z*@ej6p9PPxWB>Nw$?kC!qqz%efui^fFD?-(P`yOk4OdH>(xaHqI{|!c@L0Qz--%ws
zO>d0sNk%1$x}?#~GMlkQL4Ob5J4Nb_MArtUDWM0}z@obT?KBXv#32tAyw>e0kSxt}
ze&|*ot%h)uH{6EV)8OWkvV`QDmb-v4&2(DDxsjEn1<6CKR$RR3mRW1|Hu?uvqYzv`
zVzguM38@Zh6~=*ZueW9&bKSRN&t?69#($A-!q{L=OS{ic5YO8F&9P{nn_p{FQTj`IbTvZp(9*7Hl$jM?nVj
zrP~s4m)EheE;W9hz>9xxE?dP=u_9?Wu$teIgP-|E>ohjZTcac%R<5Yrs+n^<{|<%*+L^m|_A|>anpT3?
zUhiz^R9M;Saoo2GwVu%PBK+!x-tLB*bUabN&W^?TD5)@jTNZmu)6KLg)j)qhD;`M&=y4
zc50G$r9+P#W`CaC3-@ZO_`BV@K*^dzk1I0$DS>+vtJiN0NKV>K)fpQ%tO@KjN~vG*
z_B;;X!7b9m=AZmuF77~k9;mXLRgf2WuvdLY^wMm0gpi|}{E>_YaCH*9M${v&8|!;;
zIDd<JxA)+w4w}aGL
zYWbQ*5c$qG6*EWu5Z)H#gQH(P)5Ff4tsmV4uJ-G0k}${^)KoJ^L{*lxCeeN+
z%|@u|M969|s(cAvk>N^}9yOg6WsuJavN5IgQU~|jATFLsXgbCF{!(#63RacoY+WWp
zmN63B=gj_uJz(4DK`sCc_g#F?3VnPvcpTqB)nMD-=e^aE{#fGK!iJvlclnJuMI4b3
zvsz1}nR(Whwd-nNa}Vhdan|U1${NI?m0md%=2bZK+i!ve!H^hgJ;GcV`FxgiPUyp|
zrW?j(`1^t%ruCuKF#{#0dm}QrvN$|$Pk!qawN@mLBU5EXx2zjv
z#+$aBA1vl;y?B)(_4JCImVg2%40Axzv5LEDBpG_e$yUC&-9tG5IU3|Q-T_i{^@c)-
zhA8Gi6$w(Ok5QIf_Tbkld+;B(6G${zoXSGQ+Z$Yt;ao8Q8LsH2Hw=AR(@zK|a(x!h
zU6XLBrhnZGxS1)1*|w5WAk}Nz{+Q$14PM2Yb#1&_o|YFdei-GX?kf
zh^sZ0l7h%FKJw_YQpZG1Zjc&E5My^n#jNYZ(J3p+%mT(Ji-B`aph2)3x05nT2-&Vy
zJDbkig)J705n{J~zygP`%J~f0gBtmdE)@TMc%OPeAwK%!sC4&YUEa`RPsn
z5d424bpmb?n~yw8C{T>+z#^H`B+g-{3LZGn?7`9G#6HPLdw}Sat!H@GZ|jr8@hdxP
zta{qKY(CLF%$Wy_3910B4Dv)v`WHQ`O-hQ|A}y~SMPMcjkSJgfB{0Y+m$Tp<
z3ODk`2v@&X#s>k97lnVqMAmFFMbIbEHyI(R|M^Mk_uj;fZoqV6Y|sCR)GCIFzC#<|
z0S*idY~IWZ_j7F-5$Ya`fl?R%4E3@z>~HGl%bwVG=!L{m8tU5U|5YRC2$U7NjQjFw
zpm6xZihsA&arJcp_K&Ydg8!el3Do%Bc5^M%T06EF^KHkY6a(DLODvll)-J4{AIVhD
zsuVxNhk9Yr5C;i^gidK1+JJ>r;ap~nD{#^+n|8(HMfU|N)(o{@$_;EnWGD_8L^=fa
zt*eDR)!zF0P`q9_Ww?|OX|ZTyu!kBkZl<_Ai>prKr|3s6p|&;-MFi`#${xR$mv=32
z*TeCsSBJZ_2bYB15*L+xw!gzn!z$KD{}c#Ck|!Endi>oko1GNFmOpDDeiXkc$`_U>
z@(D^kGTHD|UZ}Z08>v8W6*&oE`9V-aQCEirlkT<^v%lnZ=eD9Q#B#4MObW_WaA)bI
zymxof_wFv6AhZ_ih%6hgn^?{r$7`-5H2=m2*g&@1GzWWg)%jbQZCZp$tWTe-}UOb&NCH(gUEOBp59o=P@-1=-P5lT4NiWN
z4yrzDxVK)1FaPfuAszf4pinf~e2MzK`YU(JpzMow3*+1L6$DPF`kA?ePFF*TXWvK7
z(%*uDn0L3Gmeo@WtjiSk+JtlvdnimbIx^rlN9K#+H)5ko0V+k00Ok!s=*3z;#C7>6
z5e*qcZk&3z85JO~)0P@LmsbQrEtj*QJ(Vrh@Za6wBL327GH%tl_J&?Yvp7Q{;J@sd
z<}Sr9D%-K{&J1uBj>TVvVlZ>GShxE~CXg|GT-{j)xK_lUORX~0phmOfJ+t1H`{StO
zfP~&ynnOa_uYssX6lR_PA{(>%yA3R$5}ocydny*b1Kup6zIMdV1Q$HrLUp;r{ZSN1
zO4KO~ctmaBMP(QgE?2$4*Jc=Kj;Si?tKypkC$FCHus=Ssd?T^;tW-g*Eh8jSuZZ>l
zA@8={$Pj`0i}~OHfBQjKV|nXunHZMACsg9AH1kUwX5wp|!;gQocDlT$ubrwluSh&?
zS8s6qH~Iw!>Dsmlnkm{^2ZlP166-;9e%)`s`yBDvmE(2435E-oW@obhpgrTzoC4kf
zK)jT+OLZwR7rW}Y+MJ}!NHtHacmC*UxeH;2DsXE-EI+--|5MbKhJ*6LPc(9yxuY4i
zGBt*S#Wy8U9~pAnOep8l5LHT4*Wb;6i8XB=jo@Sh_AcNA#`Uhj*<@vX^LWk_6TLCy
zxbOdMpJ-@%p3{O6dnl9rt6>imK9hlw^aD~bbwf)sqcL5>Xjrr8^L87OG70A>erjnv
zB>tbHD9qwxTvln1h=#>4m&JAP0jb3o@U(}PS{lb@ZIQt9O^gQdFV{t7HSpoL)j>mR
zbOQG(?j4^D|IAmY4()%ZV=3_^gESLox6&(-rZ(f`(5Z}oPOyF~`y8NTIUciY_~3!+
zhtkYJwZWtc_0>@SZSkDak8C}8@)sawj!57cShJ|


