


reNgine 2.0
Redefining the future of reconnaissance!
reNgine 2.0 is out now, you can watch reNgine 2.0 release trailer here.
What is reNgine?
reNgine is your go-to web application reconnaissance suite that's designed to simplify and streamline the reconnaissance process for security professionals, penetration testers, and bug bounty hunters. With its highly configurable engines, data correlation capabilities, continuous monitoring, database-backed reconnaissance data, and an intuitive user interface, reNgine redefines how you gather critical information about your target web applications.
Traditional reconnaissance tools often fall short in terms of configurability and efficiency. reNgine addresses these shortcomings and emerges as a excellent alternative to existing commercial tools.
reNgine was created to address the limitations of traditional reconnaissance tools and provide a better alternative, even surpassing some commercial offerings. Whether you're a bug bounty hunter, a penetration tester, or a corporate security team, reNgine is your go-to solution for automating and enhancing your information-gathering efforts.

Documentation
You can find detailed documentation at https://rengine.wiki
Table of Contents
- About reNgine
- Features
- Quick Installation
- What's new in reNgine 2.0
- Screenshots
- Contributing
- reNgine Support
- Support and Sponsoring
- reNgine Bug Bounty Program
- License
About reNgine
reNgine is not an ordinary reconnaissance suite; it's a game-changer! We've turbocharged the traditional workflow with groundbreaking features that is sure to ease your reconnaissance game. reNgine redefines the art of reconnaissance with highly configurable scan engines, recon data correlation, continuous monitoring, GPT powered Vulnerability Report, Project Management and role based access control etc.
🦾 reNgine has advanced reconnaissance capabilities, harnessing a range of open-source tools to deliver a comprehensive web application reconnaissance experience. With it's intuitive User Interface, it excels in subdomain discovery, pinpointing IP addresses and open ports, collecting endpoints, conducting directory and file fuzzing, capturing screenshots, and performing vulnerability scans. To summarize, it does end-to-end reconnaissance. With WHOIS identification and WAF detection, it offers deep insights into target domains. Additionally, reNgine also identifies misconfigured S3 buckets and find interesting subdomains and URLS, based on specific keywords to helps you identify your next target, making it an go to tool for efficient reconnaissance.
🗃️ Say goodbye to recon data chaos! reNgine seamlessly integrates with a database, providing you with unmatched data correlation and organization. Forgot the hassle of grepping through json, txt or csv files. Plus, our custom query language lets you filter reconnaissance data effortlessly using natural language like operators such as filtering all alive subdomains with http_status=200 and also filter all subdomains that are alive and has admin in name http_status=200&name=admin
🔧 reNgine offers unparalleled flexibility through its highly configurable scan engines, based on a YAML-based configuration. It offers the freedom to create and customize recon scan engines based on any kind of requirement, users can tailor them to their specific objectives and preferences, from thread management to timeout settings and rate-limit configurations, everything is Customizable. Additionally, reNgine offers a range of pre-configured scan engines right out of the box, including Full Scan, Passive Scan, Screenshot Gathering, and the OSINT Scan Engine. These ready-to-use engines eliminate the need for extensive manual setup, aligning perfectly with reNgine's core mission of simplifying the reconnaissance process and enabling users to effortlessly access the right reconnaissance data with minimal effort.
📃 PDF Reports: In addition to its robust reconnaissance capabilities, reNgine goes the extra mile by simplifying the report generation process, recognizing the crucial role that PDF reports play in the realm of end-to-end reconnaissance. Users can effortlessly generate and customize PDF reports to suit their exact needs. Whether it's a Full Scan Report, Vulnerability Report, or a concise reconnaissance report, reNgine provides the flexibility to choose the report type that best communicates your findings. Moreover, the level of customization is unparalleled, allowing users to select report colors, fine-tune executive summaries, and even add personalized touches like company names and footers. With GPT integration, your reports aren't just a report, with remediation steps, and impacts, you get 360-degree view of the vulnerabilities you've uncovered.
🔖 Say Hello to Projects! reNgine 2.0 introduces a powerful addition that enables you to efficiently organize your web application reconnaissance efforts. With this feature, you can create distinct project spaces, each tailored to a specific purpose, such as personal bug bounty hunting, client engagements, or any other specialized recon task. Each projects will have separate dashboard and all the scan results will be separated from each projects, while scan engines and configuration will be shared across all the projects.
⚙️ Roles and Permissions! Begining reNgine 2.0, we've taken your web application reconnaissance to a whole new level of control and security. Now, you can assign distinct roles to your team members—Sys Admin, Penetration Tester, and Auditor—each with precisely defined permissions to tailor their access and actions within the reNgine ecosystem.
- 🔐 Sys Admin: Sys Admin is a super user that has permission to modify system and scan related configurations, scan engines, create new users, add new tools etc. Super user can initiate scans and subscans effortlessly.
- 🔍 Penetration Tester: Penetration Tester will be allowed to modify and initiate scans and subscans, add or update targets, etc. A penetration tester will not be allowed to modify system configurations.
- 📊 Auditor: Auditor can only view and download the report. An auditor can not change any system or scan related configurations nor can initiate any scans or subscans.
🚀 GPT Vulnerability Report Generation: Get ready for the future of penetration testing reports with reNgine's groundbreaking feature: "GPT-Powered Report Generation"! With the power of OpenAI's GPT, reNgine now provides you with detailed vulnerability descriptions, remediation strategies, and impact assessments that read like they were written by a human security expert! But that's not all! Our GPT-driven reports go the extra mile by scouring the web for related news articles, blogs, and references, so you have a 360-degree view of the vulnerabilities you've uncovered. With reNgine 2.0 revolutionize your penetration testing game and impress your clients with reports that are not just informative but engaging and comprehensive with detailed analysis on impact assessment and remediation strategies.
🥷 GPT-Powered Attack Surface Generation: With reNgine 2.0, reNgine seamlessly integrates with GPT to identify the attacks that you can likely perform on a subdomain. By making use of reconnaissance data such as page title, open ports, subdomain name etc, reNgine can advice you the attacks you could perform on a target. reNgine will also provide you the rationale on why the specific attack is likely to be successful.
Features
- Reconnaissance: Subdomain Discovery, IP and Open Ports Identification, Endpoints Discovery, Directory and Files fuzzing, - Screenshot gathering, Vulnerability scan using Nuclei, WHOIS Identification, WAF Detection etc.
- Highly configurable YAML-based Scan Engines
- Support for Parallel Scans and Subscans
- Automatically report Vulnerabilities to HackerOne
- Recon Data visualization
- OSINT Capabilities (Meta info Gathering, Employees Gathering, Email Address with an option to look password in the leaked database, - dorks, etc.)
- Customizable Alerts/Notifications on Slack, Discord, and Telegram
- Perform Advanced Query lookup using natural language alike and, or, not operations
- Recon Notes and Todos
- Clocked Scans (Run reconnaissance exactly at X Hours and Y minutes) and Periodic Scans (Runs reconnaissance every X minutes/- hours/days/week)
- Proxy Support
- Screenshot Gallery with Filters
- Powerful recon data filtering with autosuggestions
- Recon Data changes, find new/removed subdomains/endpoints
- Tag targets into the Organization
- Identify Interesting Subdomains
- Custom GF patterns and custom Nuclei Templates
- Edit tool-related configuration files (Nuclei, Subfinder, Naabu, amass)
- Add external tools from Github/Go
- Interoperable with other tools, Import/Export Subdomains/Endpoints
- Import Targets via IP and/or CIDRs
- Report Generation
- Toolbox: Comes bundled with most commonly used tools such as whois lookup, CMS detector, CVE lookup, etc.
- Identification of related domains and related TLDs for targets
- Find actionable insights such as Most Common Vulnerability, Most Common CVE ID, Most Vulnerable Target/Subdomain, etc.
Quick Installation
Note: Only Ubuntu/VPS
-
Clone this repo
git clone https://github.com/yogeshojha/rengine && cd rengine -
Edit the dotenv file, please make sure to change the password for postgresql
POSTGRES_PASSWORD!nano .env -
Run the installation script, Please keep an eye for any prompt, you will also be asked for username and password for reNgine.
sudo ./install.shIf
install.shdoes not have install permission, please change it,chmod +x install.sh
reNgine can now be accessed from https://127.0.0.1 or if you're on the VPS https://your_vps_ip_address
A detailed installation guide can also be found here. Thanks to Rubén!
Installation (Mac/Windows/Other)
Installation instructions can be found at https://reNgine.wiki/install/detailed/
Updating
-
Updating is as simple as running the following command:
sudo ./update.shIf
update.shdoes not have execution permissions, please change it,sudo chmod +x update.sh
Changelog
Please find the latest release notes and changelog here.
Screenshots
Scan Results

General Usage

Initiating Subscan

Recon Data filtering

Report Generation

Toolbox

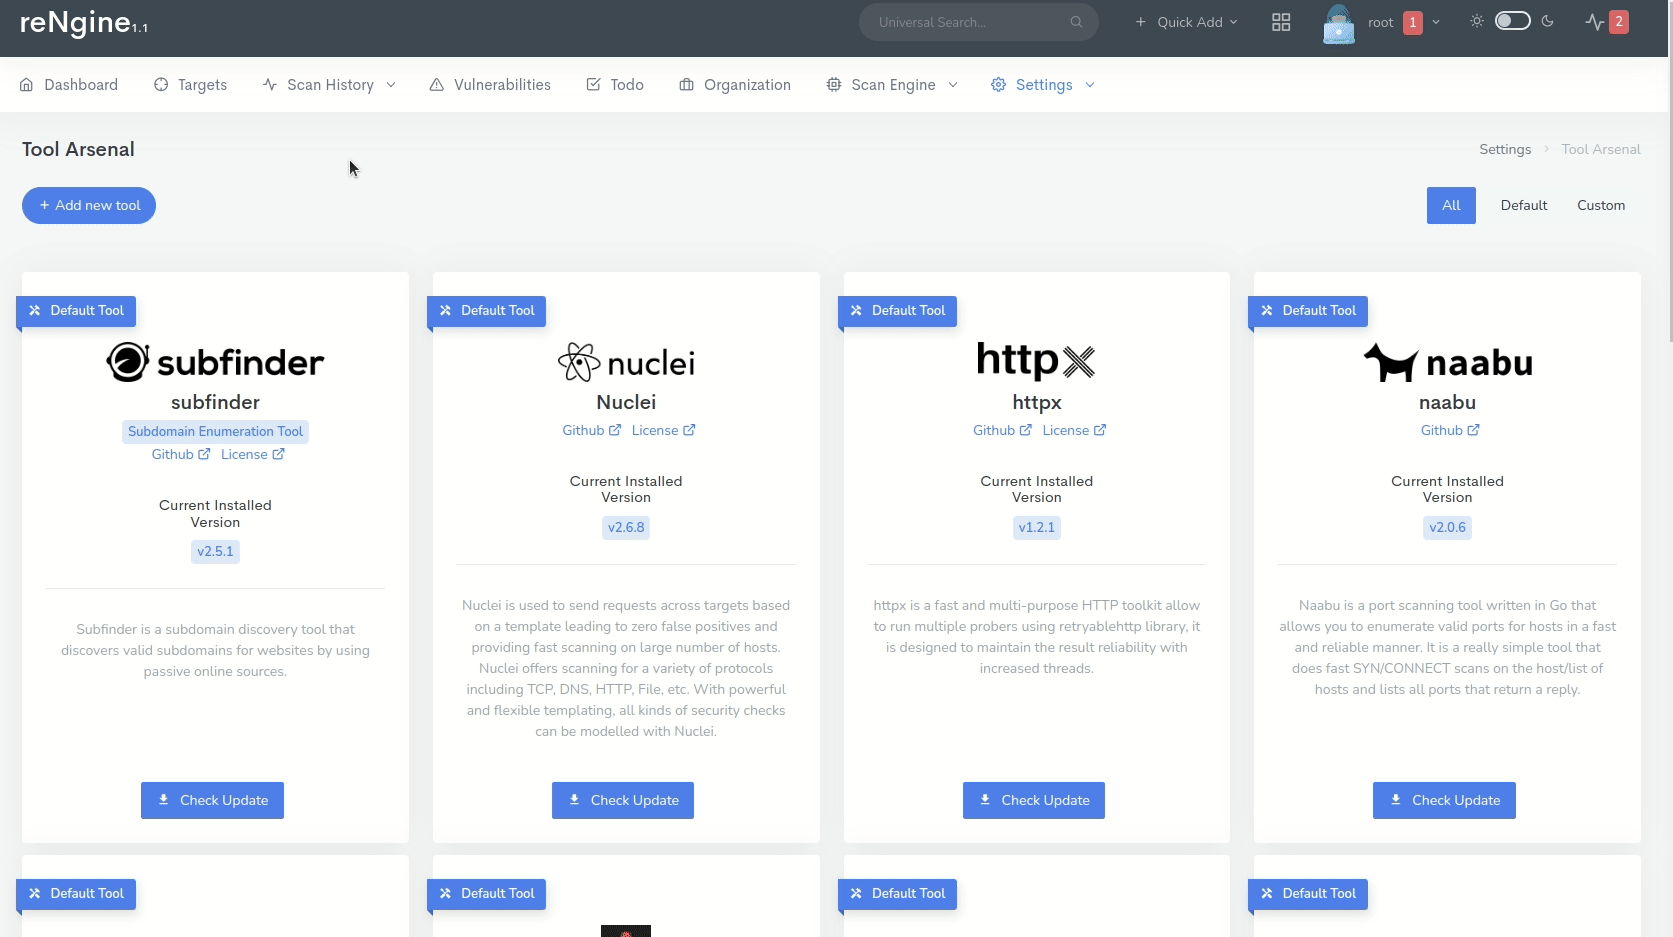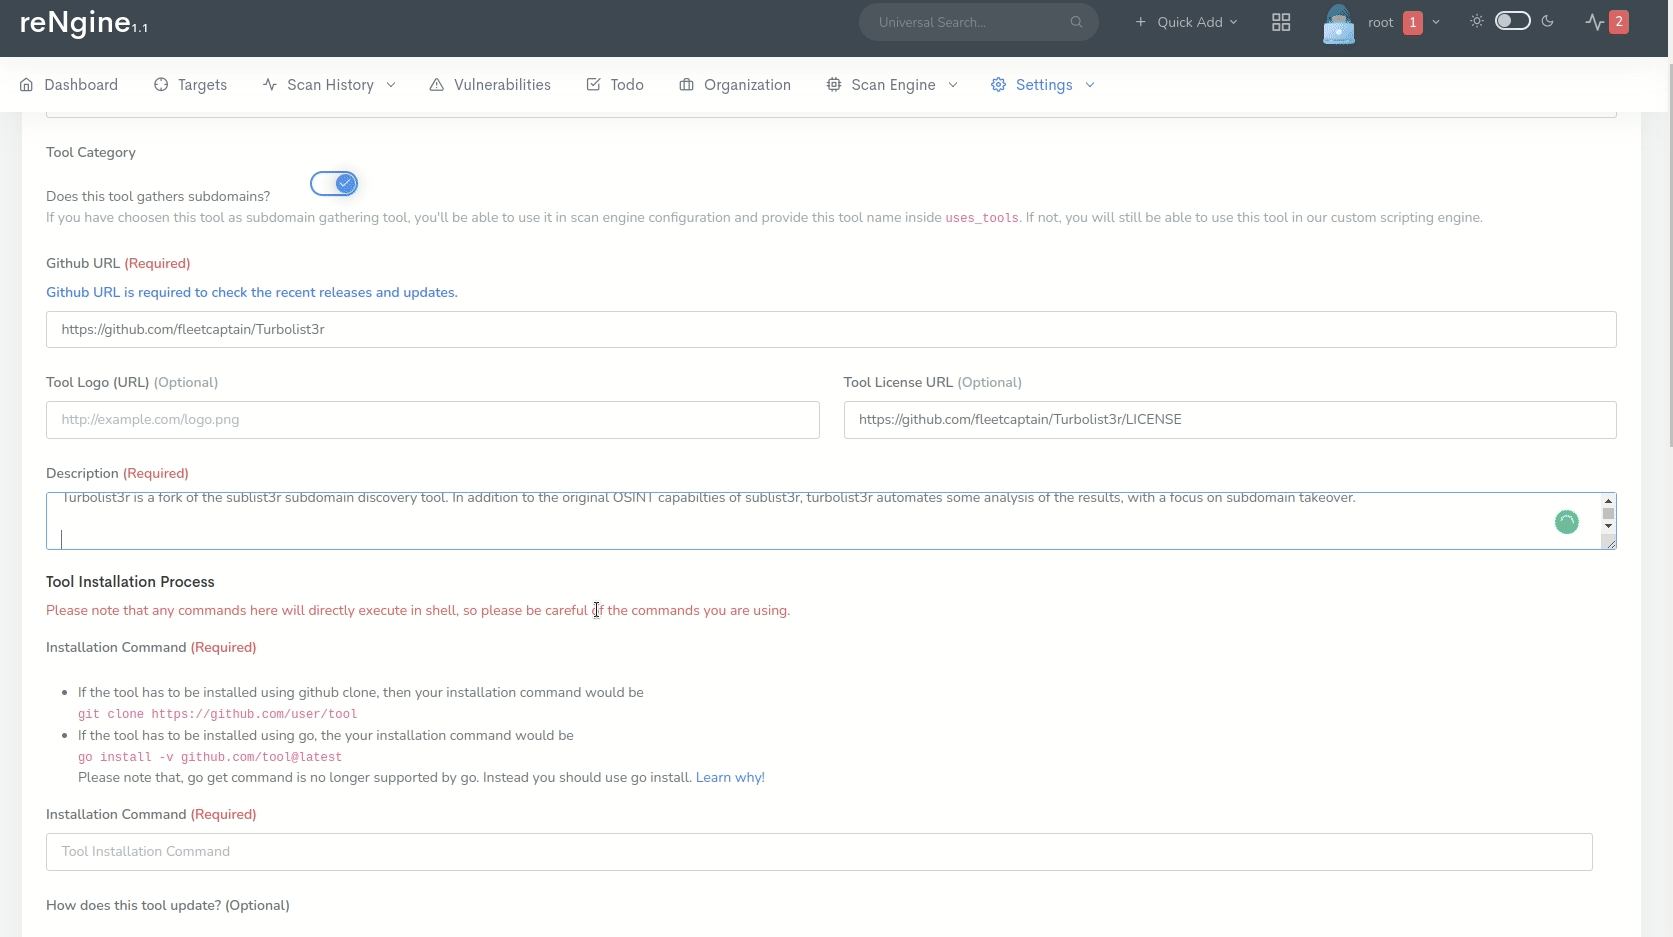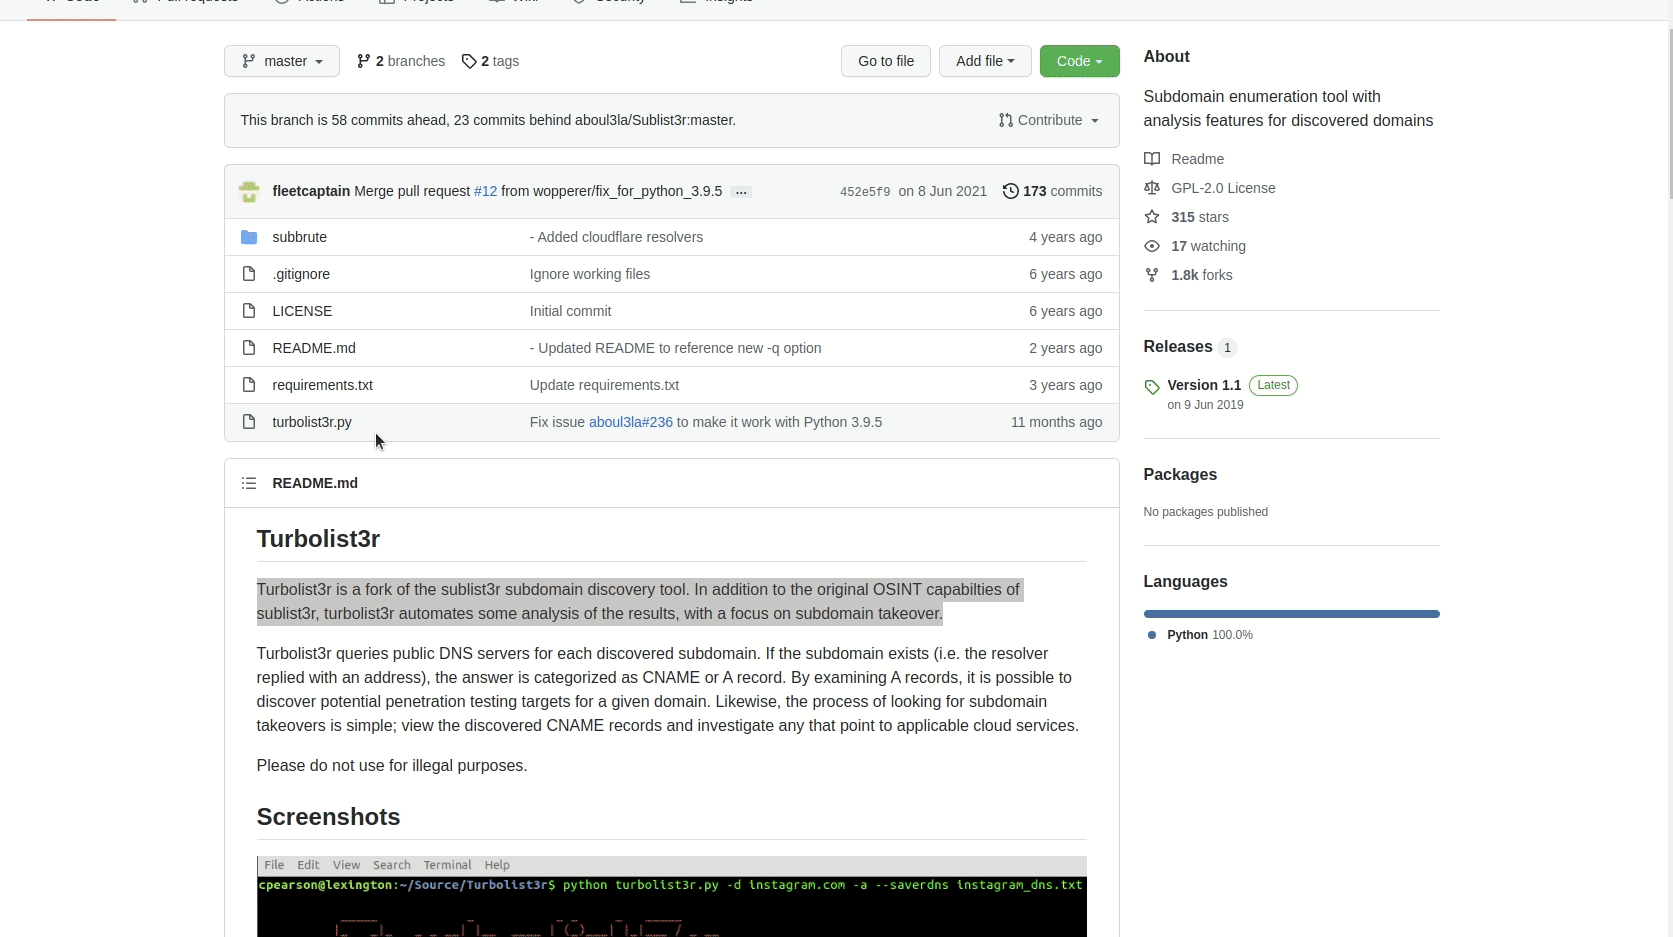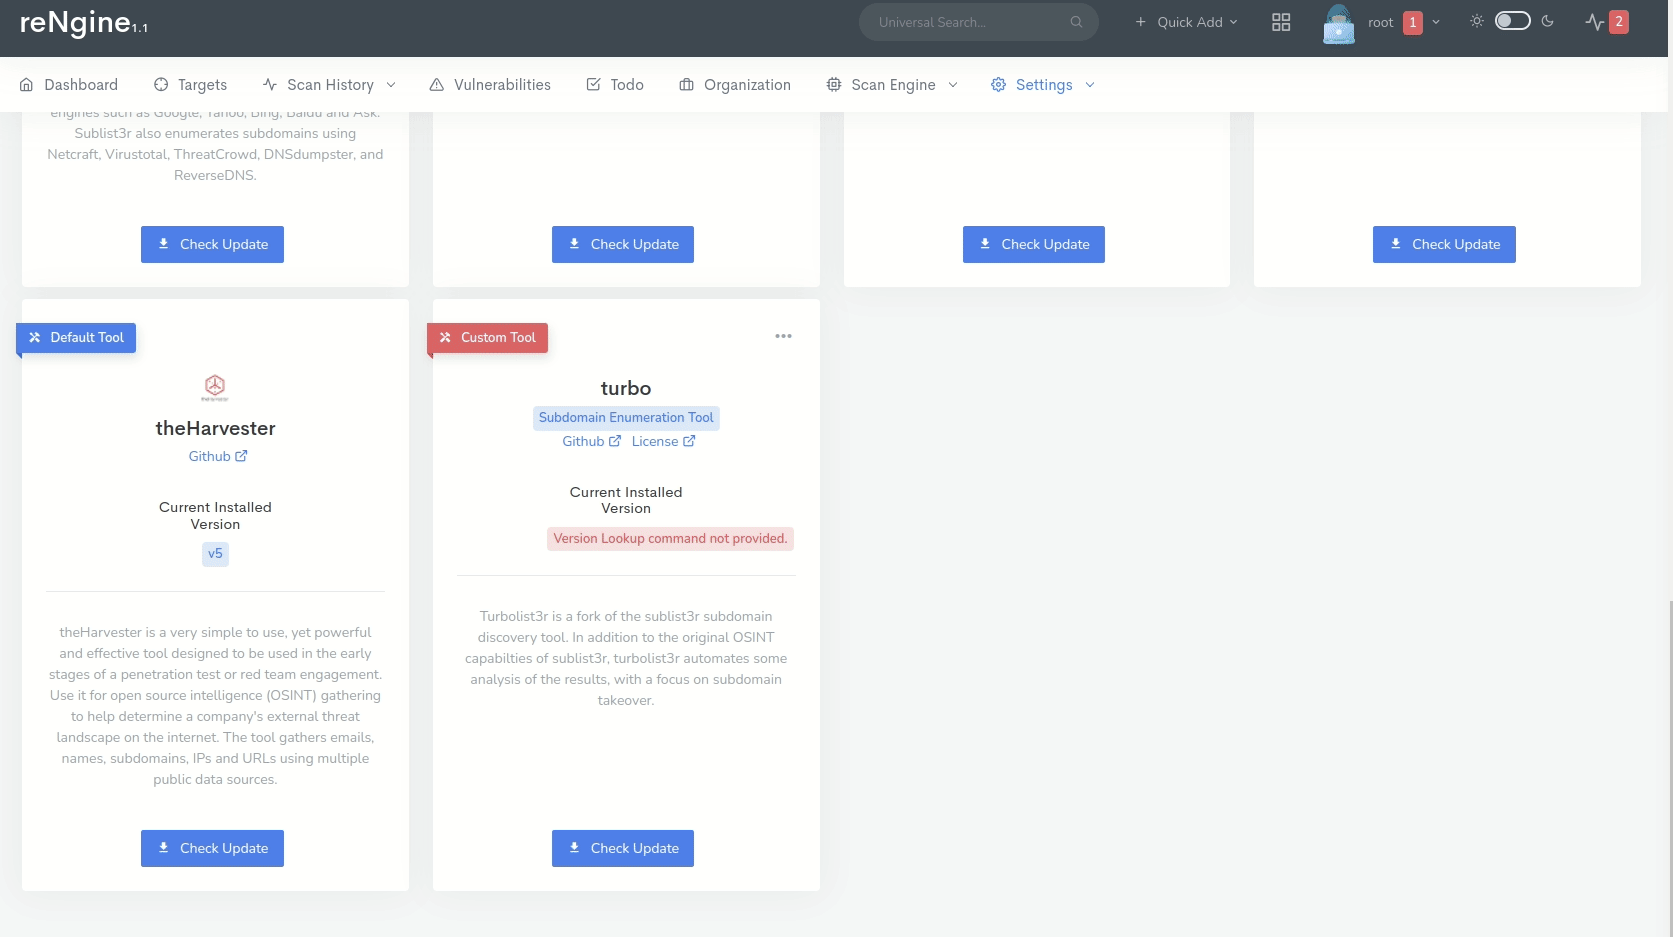
Adding Custom tool in Tools Arsenal
Contributing
Contributions are what make the open-source community such an amazing place to learn, inspire and create. Every contributions you make is greatly appreciated. Your contributions can be as simple as fixing the indentation or UI, or as complex as adding new modules and features.
See the Contributing Guide to get started.
You can also join our Discord channel #development for any development related questions.
First-time Open Source contributors
Please note that reNgine is beginner friendly. If you have never done open-source before, we encourage you to do so. We will be happy and proud of your first PR ever.
You can start by resolving any open issues.
reNgine Support
Please do not use GitHub for support requests. Instead, join our Discord channel #support.
Support and Sponsoring
Over the past few years, I have been working hard on reNgine to add new features with the sole aim of making it the de facto standard for reconnaissance. I spend most of my free time and weekends working on reNgine. I do this in addition to my day job. I am happy to have received such overwhelming support from the community. But to keep this project alive, I am looking for financial support.
| Paypal | Bitcoin | Ethereum |
|---|---|---|
| https://www.paypal.com/paypalme/yogeshojha11 | 35AiKyNswNZ4TZUSdriHopSCjNMPi63BCX |
0xe7A337Da6ff98A28513C26A7Fec8C9b42A63d346 |
OR
- Add a GitHub Star to the project.
- Tweet about this project, or maybe blogs?
- Maybe nominate me for GitHub Stars?
- Join DigitalOcean using my referral link your profit is $100 and I get $25 DO credit. This will help me test reNgine on VPS before I release any major features.
It takes a considerable amount of time to add new features and make sure everything works. Donating is your way of saying: reNgine is awesome.
Any support is greatly appreciated! Thank you!
reNgine Bug Bounty Program
Security researchers, welcome aboard! I'm excited to announce the reNgine bug bounty programme in collaboration with huntr.dev, which means that you will be rewarded for any vulnerabilities you find in reNgine.
Thank you for your interest in reporting reNgine vulnerabilities! If you are aware of any potential security vulnerabilities in reNgine, we encourage you to report them immediately via huntr.dev.
Please do not disclose vulnerabilities via Github issues/blogs/tweets after/before reporting to huntr.dev as this is explicitly against the disclosure policy of huntr.dev and reNgine and will not be considered for monetary rewards.
Please note that the reNgine maintainer does not set the bounty amount. The bounty reward is determined by an industry-first equation developed by huntr.dev to understand the popularity, impact and value of repositories to the open-source community.
What do I expect from security researchers?
- Patience: Please note that I am currently the only maintainer in reNgine and it will take some time to validate your report. I ask for your patience during this process.
- Respect for privacy and security reports: Please do not publicly disclose any vulnerabilities (including GitHub issues) before or after reporting them on huntr.dev! This is against the disclosure policy and will not be rewarded.
- Respect the rules
What do you get in return?
- Thanks from the maintainer
- Monetary rewards
- CVE ID(s)
Please find the FAQ and Responsible disclosure policy from huntr.dev.
License
Distributed under the GNU GPL v3 License. See LICENSE for more information.
(ChatGPT was used to write some or most part of this README section.)